 Do Son
Notepad++ vulnerabilities now have public PoC exploit code. CVE-2026-52886, CVE-2026-54758, and CVE-2026-57233 are fixed in v8.9.7. Update now.
notepad++
Learn about the new Notepad++ security flaws. Public Notepad++ exploit code triggers arbitrary code execution. Update to version v8.9.6.1 now.
Microsoft is quietly rebranding Copilot features in Windows 11. Discover why Notepad’s AI is now called "Advanced Features" and what this means for the OS.
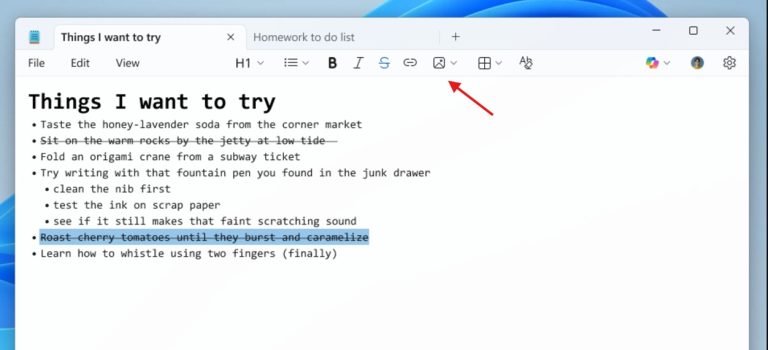
Microsoft is turning Notepad into a powerful Markdown editor with new image support. Discover how the classic text tool is evolving for the Windows 11 era.

Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.
Notepad++ confirms update infrastructure was compromised by state-sponsored actors targeting specific users. Update to version 8.8.9 immediately.

ASEC warns of Larva-25012 using fake Notepad++ installers for Proxyjacking. The malware disables Defender and sells your bandwidth. Check your tasks.

A Notepad++ flaw (now patched in v8.8.9) allowed attackers to hijack the WinGUp update process, serving malware instead of the legitimate executable. Manual update is urged.

Windows 11's Notepad now supports on-device AI, allowing for text generation and summarization without a Microsoft account or cloud connection.

CVE-2025-49144 lets attackers gain NT AUTHORITY\SYSTEM via Notepad++ v8.8.1 installer flaw. PoC available—secure paths and signatures urged.

Explore the Windows 11 Snipping Tool with its latest upgrades, enhancing your screen capture experience effortlessly.

Even without the final payload, WikiLoader poses a significant risk by meticulously gathering information about the infected system

Popular text editing software used by millions across China has become the latest target in a sophisticated cyberattack

MetaStealer found its way into systems primarily through malspam and cracked software distributed via hijacked YouTube accounts.
CVE-2023-40031 (CVSS score of 7.8): heap buffer write overflow in `Utf8_16_Read::convert`. This issue may lead to arbitrary code execution