 Do Son
Microsoft led a coalition disrupting EvilTokens cybercrime platform. Learn how the EvilTokens cybercrime platform used AI and device code phishing.
Phishing-as-a-Service
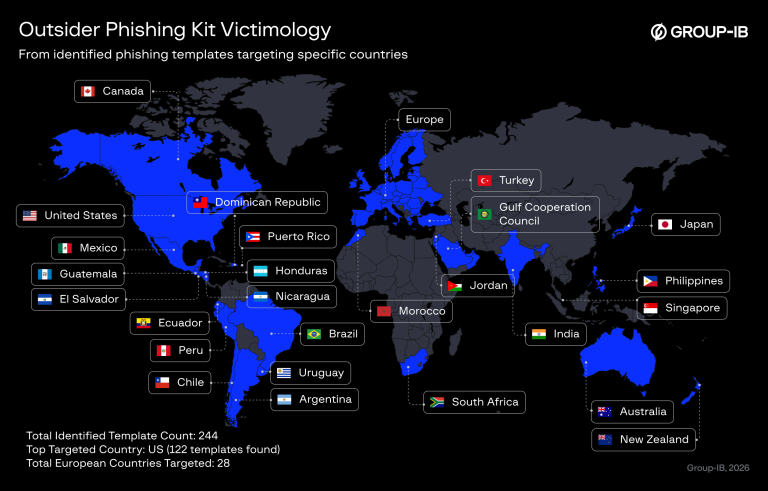
The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
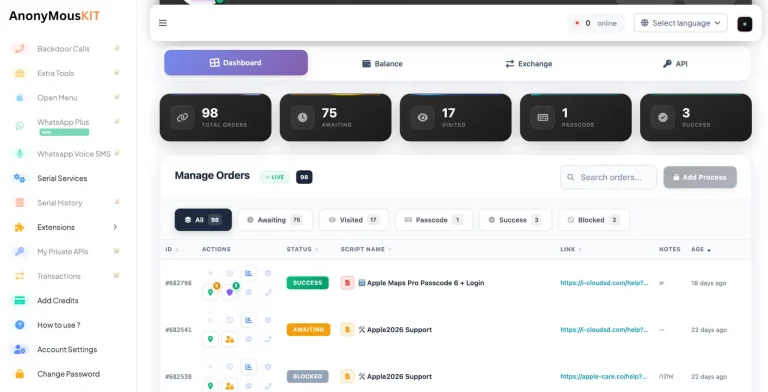
AnonyMousKIT is an AI-powered PhaaS platform that phones iPhone theft victims as fake Apple Support to steal passcodes and beat Activation Lock.
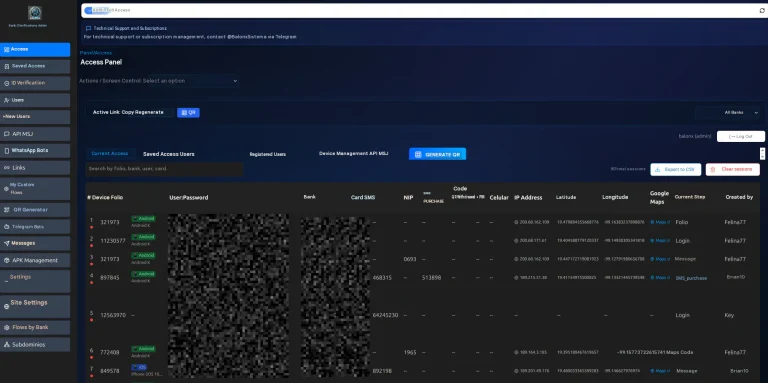
Group-IB exposed Balonx Sistema, a Mexican PhaaS platform bundling real-time phishing, an Android RAT, and AI-driven vishing against 20+ banks.
Cisco Talos exposes ARToken, a phishing platform using device code phishing to steal Microsoft 365 tokens and bypass MFA.

Discover how the Chinese PhaaS ecosystem uses real-time interception and AI automation to bypass MFA and exploit digital wallets.

The FBI issued an alert on the new Kali365 phishing platform. Learn how this PhaaS kit steals Microsoft 365 tokens and bypasses MFA.

Despite a global takedown, Tycoon 2FA is back. It now abuses Microsoft's device code flow to bypass MFA entirely. Disabling this flow is critical.

AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!

Varonis uncovers Bluekit, a new phishing-as-a-service kit using AI and 40+ templates to automate session hijacking and credential theft. See how it works.

Group-IB unmasks the Phoenix System: a PhaaS platform using rogue cell towers and live-dashboards to bypass MFA across 2,500+ domains. Read the full report.
The FBI and Indonesia dismantle W3LL, a $20M phishing kit that bypassed MFA and hijacked live sessions. Learn about the takedown of this MaaS powerhouse.
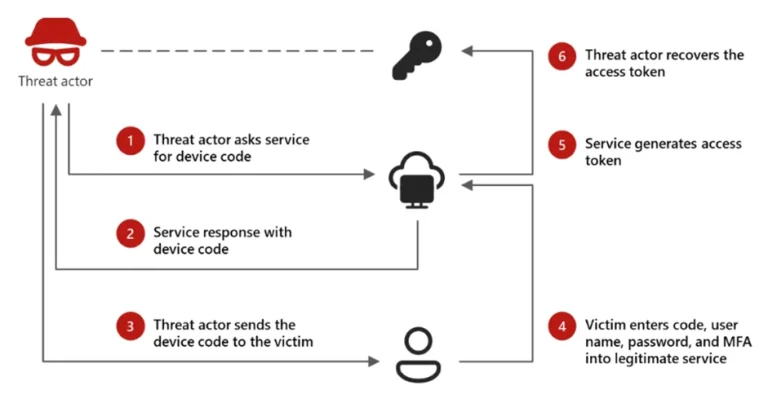
Microsoft uncovers EvilToken, an AI-powered PhaaS toolkit using Dynamic Device Code Generation to bypass MFA and breach high-value accounts. Patch now!
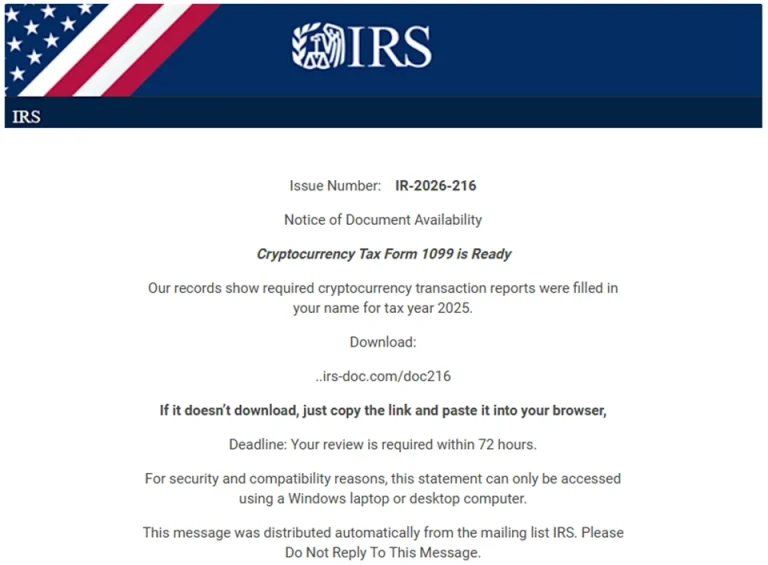
Microsoft warns of a surge in tax-themed phishing using PhaaS and ScreenConnect RATs to bypass MFA and hijack systems. Protect your W-2 data this season.

Microsoft and Europol lead a global coalition to dismantle Tycoon 2FA, a massive AiTM phishing platform that bypassed MFA for over 500,000 organizations.

New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.

BlackForce, a new PhaaS kit, is being sold for €300, using React/React Router to disguise its code. It utilizes stateful sessions and MitB to bypass MFA in real time. Update to V5 shows rapid evolution.

A new report reveals Chinese-speaking smishing syndicates are using phishing-as-a-service, MFA bypass, and stolen cards to conduct a multi-billion dollar fraud campaign targeting digital wallets.
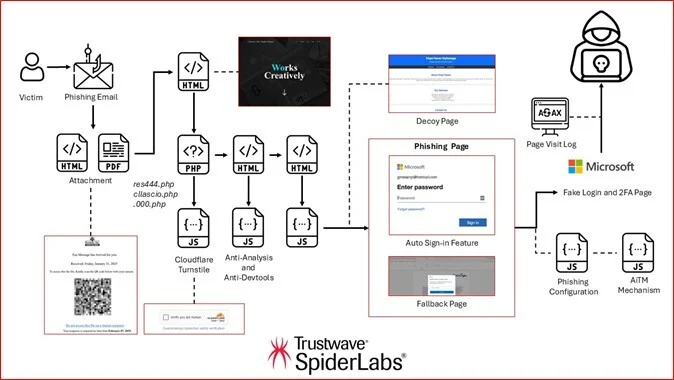
Trustwave uncovers Dadsec and Tycoon2FA, new Phishing-as-a-Service kits bypassing MFA to target Microsoft 365 users with advanced AiTM tactics.

mnemonic exposes Darcula, a global phishing-as-a-service network using the Magic Cat toolkit to target mobile users with encrypted, real-time scam dashboards.
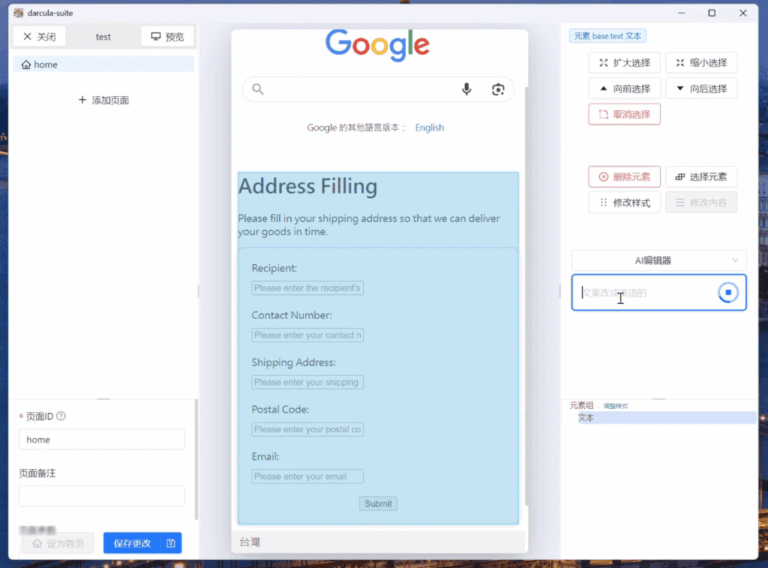
Darcula-Suite integrates AI to supercharge phishing-as-a-service operations, enabling faster, scalable, and more convincing phishing campaigns worldwide.

Explore the dangerous world of Phishing-as-a-Service (PhaaS). Learn about the rise of subscription-based platforms that enable cybercriminals to launch sophisticated phishing campaigns.