
 Do Son
FreeBSD patches a critical jail escape (CVE-2025-15576) and a kernel heap overflow (CVE-2026-3038). Learn how nullfs and routing sockets put hosts at risk.
privilege escalation

NVIDIA warns of three high-severity vulnerabilities (CVE-2025-33179, 33180, 33181) in Cumulus Linux. Low-privileged users can escalate to admin control.
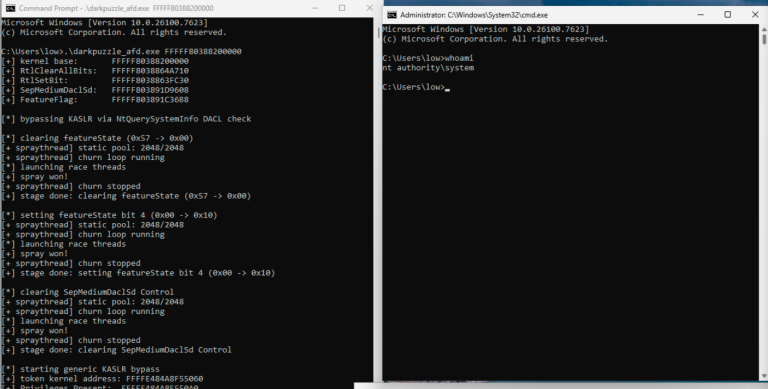
Windows kernel vulnerability CVE-2026-21241 (afd.sys) exposed! A new PoC exploit shows how local attackers can win a race condition to gain SYSTEM privileges.

Researcher Justin Swartz uncovers a regression of the 1999 telnetd flaw. Remote attackers can bypass authentication and seize root control via environment variables.

SolarWinds patches four critical 9.1 CVSS RCE vulnerabilities in Serv-U. Attackers can create admin users and execute code as root. Update to 15.5.4 now!

Broadcom warns of a high-severity RCE flaw (CVE-2026-22719) in VMware Aria Operations. Attackers can execute commands during system migrations. Patch now!

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

NVIDIA warns of 7.8-rated vulnerabilities in Megatron Bridge. Learn how "educational" tutorials could let attackers hijack your AI training infrastructure.

WatchGuard patches two flaws: a VPN privilege escalation (NCPVE-2025-0626) and Fireware LDAP injection (CVE-2026-1498). Update Firebox and VPN clients now.

On January 29, 2026, Synology, a preeminent manufacturer of Network Attached Storage (NAS) solutions, disseminated a series...

Exploit code released for Zabbix flaw CVE-2025-27237. Low-level users can gain SYSTEM privileges on Windows via OpenSSL config. Update now.

Critical Kyverno flaw CVE-2026-22039 (CVSS 10) allows policy creators to gain cluster admin rights. Update to v1.16.3 to fix privilege escalation & DoS.
NVIDIA patches high-severity flaws (CVE-2025-33217) in GPU drivers & vGPU software. Flaws allow code execution. Update Windows/Linux drivers now.

Critical WD Discovery flaw CVE-2025-30248 (CVSS 8.9) allows DLL hijacking during installation. Update to v5.3 immediately to prevent system takeover.
Public PoC exploit for Android CVE-2024-23700 allows critical privilege escalation without user interaction. WearOS & Custom ROMs are at risk.

HPE warns of critical flaw CVE-2026-23594 in Alletra & Nimble Storage. CVSS 8.8 bug allows remote admin access. Update to v6.1.2.800 now to secure data.

Critical Academy LMS flaw CVE-2025-15521 (CVSS 9.8) is being exploited. Unauthenticated attackers can reset admin passwords. Update now to secure your site.
NVIDIA patches 4 high-severity flaws in CUDA Toolkit (up to v13.1). Vulnerabilities in Nsight Systems allow code execution & privilege escalation. Update now.

Critical GNU Inetutils telnetd flaw allows unauthenticated root access via "-f root". Affects v1.9.3-2.7. Disable telnet immediately to stay safe.

Critical ACF Extended flaw CVE-2025-14533 (CVSS 9.8) lets attackers seize admin control. 100k sites at risk. Update to version 0.9.2.2 immediately.
AVEVA issues critical alert for Process Optimization software. CVE-2025-61937 (CVSS 10) allows unauthenticated RCE. Upgrade to version 2025 immediately.

OpenStack patches CVE-2026-22797 (Privilege Escalation). Flaw in OAuth2 middleware allows header forgery for admin access. Update keystonemiddleware now.