
 Do Son
SonicWall patches critical SMA 1000 flaws, including a 7.2 SQL injection for privilege escalation and Unicode-based MFA bypasses. Secure your VPN—update now!
privilege escalation
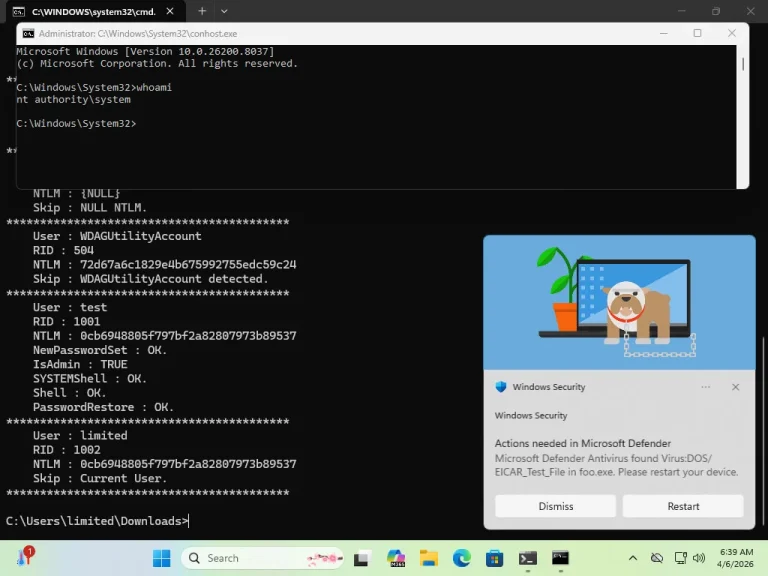
BlueHammer is a functional 0-day exploit targeting Windows Defender’s update engine to achieve SYSTEM privileges. Here is how the unpatched LPE works.
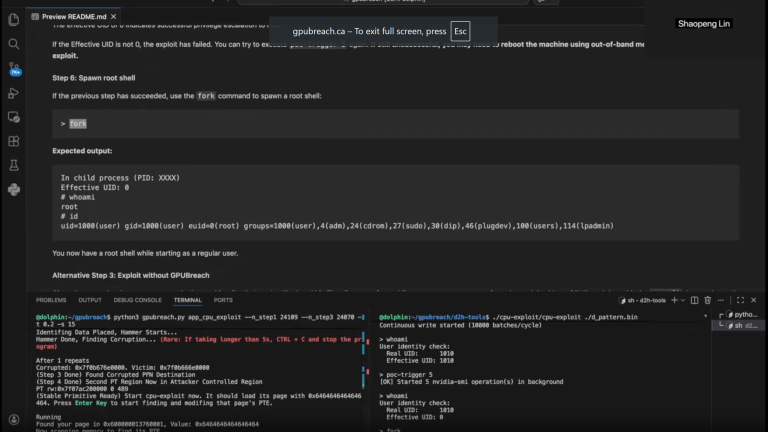
GPUBreach: A new GPU Rowhammer attack from UofT that bypasses IOMMU and ECC to achieve full system root on NVIDIA systems. GitHub code arrives April 13.

OpenSSH 10.3 fixes critical gaps, including client-side command execution and scp privilege escalation flaws. Update your remote access stacks immediately.
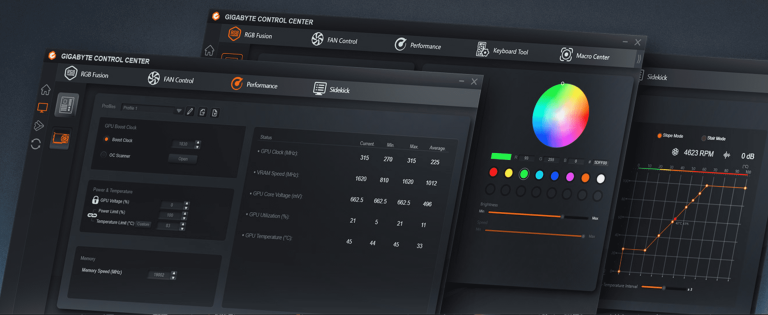
Gigabyte Control Center faces a critical 9.2 severity flaw (CVE-2026-4415). Unauthenticated attackers can write files and execute code—update to 25.12.10.01 now.
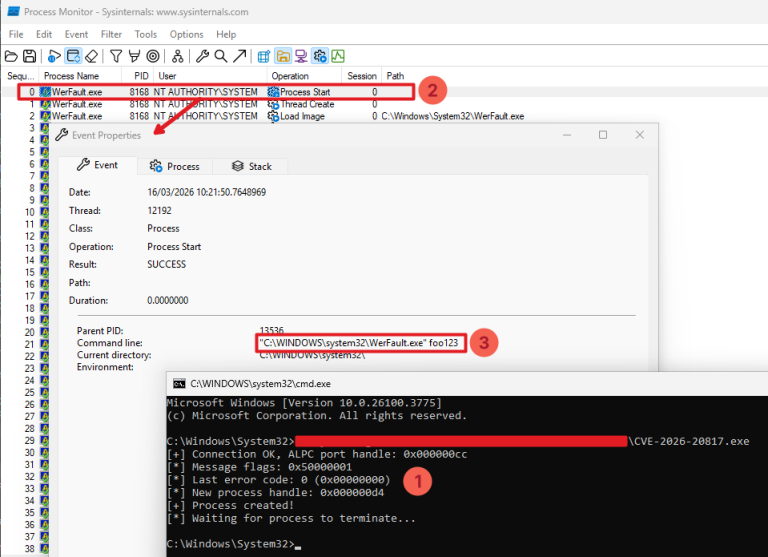
Clément Labro releases a public PoC for CVE-2026-20817, a critical Windows LPE flaw in the WER service. Patch now to prevent SYSTEM-level hijacking.

Cisco alerts of public flaws in IOS XE. Authenticated users can trigger a network-wide DoS or escalate privileges via the Lobby Ambassador API. Patch now.

Full disclosure: Technical details and a GitHub PoC for CVE-2025-39946 are live. This Linux TLS vulnerability allows root escalation via memory shaping.
GeoVision fixes a critical 10.0 CVSS flaw in GV-Edge Recording Manager. CVE-2026-4606 allows local users to gain SYSTEM-level control. Update to V2.3.2 now.
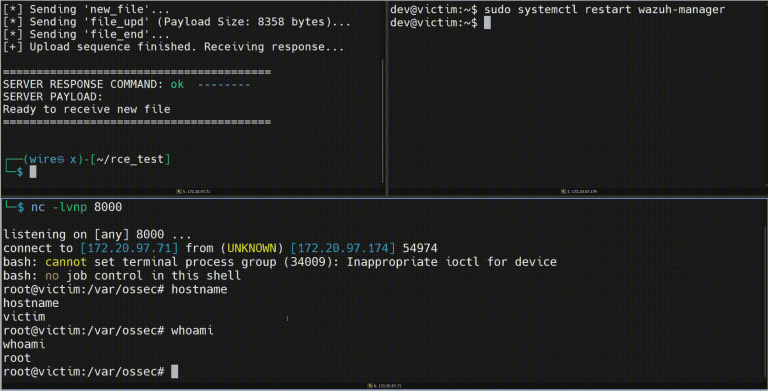
Wazuh patches two critical 9.1 CVSS flaws (CVE-2026-25769 & CVE-2026-25770) allowing total cluster takeover. Upgrade to v4.14.3 now to stay protected.

Craft CMS patches CVE-2026-32267, a critical 7.7 CVSS flaw where a simple Live Preview token grants low-privilege users full admin access. Update today.
A critical 10.0 CVSS logic flaw in File Browser (CVE-2026-32760) grants unauthenticated users automatic admin rights upon signup. Update to 2.62.0 now.
An 8.6 CVSS flaw (CVE-2026-31386) in LiteSpeed Web Server editions allows OS command injection and system compromise. Restrict WebAdmin access immediately.

Winter CMS urgently patches a critical 10.0 CVSS privilege escalation flaw (CVE-2026-27591) allowing low-level backend users to gain full system control.

Veeam urgently patches critical 9.9 CVSS RCE flaws (CVE-2026-21666, CVE-2026-21708) in Backup & Replication 12.3.2. Update your servers immediately.

CrackArmor exposes 12.6M Linux servers to root escalation. Qualys TRU discovers 9 AppArmor flaws letting users bypass security and escape containers.

Veeam releases a critical security update fixing 9.9 CVSS RCE flaws (CVE-2026-21669, CVE-2026-21708) in Backup & Replication. Patch servers immediately.
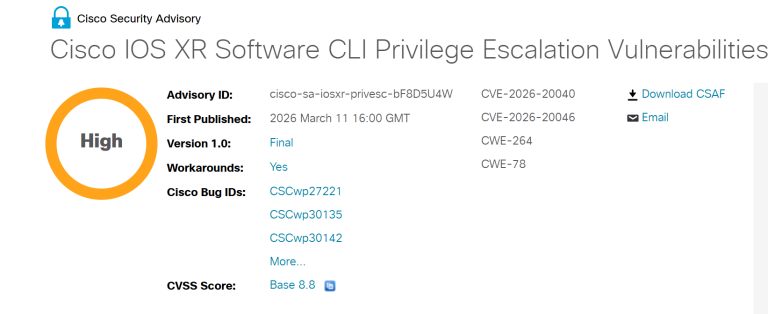
Cisco patches critical privilege escalation flaws (CVE-2026-20040, CVE-2026-20046) in IOS XR software that allow local attackers to gain full root access.
Zoom patches a critical 9.6 CVSS flaw (CVE-2026-30903) allowing unauthenticated remote privilege escalation on Windows. Update your clients immediately.
Critical vulnerabilities in Vaultwarden (like CVE-2026-27898) allow privilege escalation and unauthorized access to secrets. Update to version 1.35.4 now.

Cisco warns that two vulnerabilities (CVE-2026-20122 and CVE-2026-20128) in its Catalyst SD-WAN Manager are being actively exploited. Update immediately.

A critical 9.8 CVSS flaw (CVE-2026-1492) in the WordPress User Registration & Membership plugin lets unauthenticated attackers create admin accounts.