 Do Son
Cisco Talos found msaRAT malware, a Rust RAT from the Chaos ransomware group that hides C2 traffic inside headless Chrome and Edge sessions.
Rust malware
Spirals ransomware hit a South Asian IT firm in a double extortion attack, going from IIS breach to network-wide encryption in under 24 hours.

LabubaRAT is a Rust-based remote access tool disguised as NVIDIA software. It supports HTTPS, WebView2, and DNS tunneling for command and control.

Silver Fox's Ghost distributor delivers MODBEACON, a modular Rust trojan, to picked targets in Operation Phnom Penh, per Qianxin. Here's what to know.
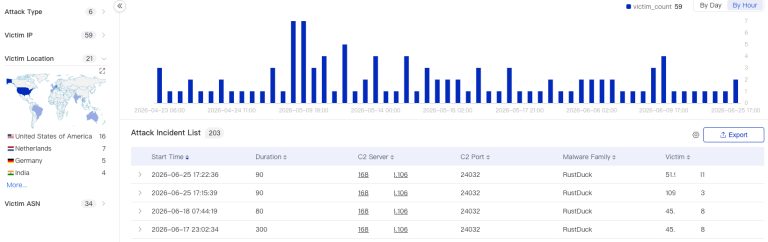
The RustDuck botnet is a fast-evolving two-stage DDoS threat moving from C to Rust, with encrypted C2 and heavy anti-analysis, per XLab.
Check Point exposed a crypto clipboard hijacker spread by fake Ghost Networks. The Rust clipper swaps wallet addresses to steal crypto. Stay alert.
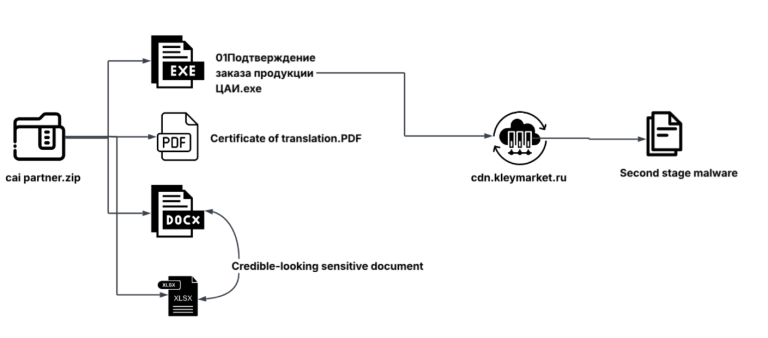
SEQRITE Labs uncovers Operation Silent Rotor, a targeted Rust-based cyberattack on the Eurasian unmanned aviation sector ahead of the 2026 Moscow forum.
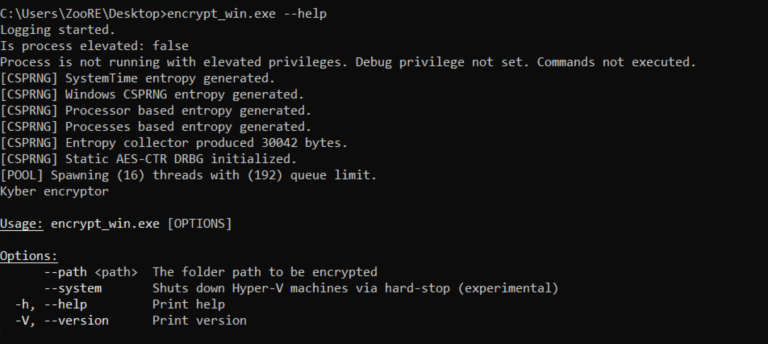
Rapid7 uncovers Kyber, a dual-platform ransomware targeting VMware ESXi and Windows. Learn how it causes operational blackouts and bypasses recovery.
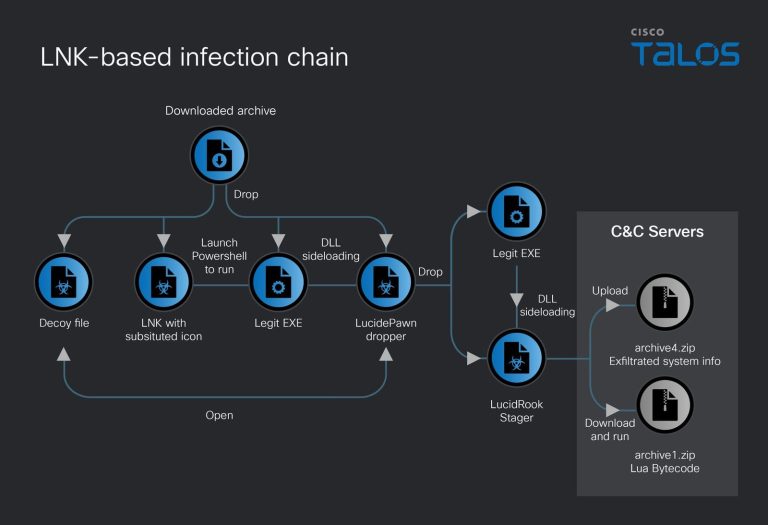
Cisco Talos reveals UAT-10362’s "Lucid" malware family targeting Taiwan. Using Lua, Rust, and regional locks, this threat prioritizes extreme stealth.
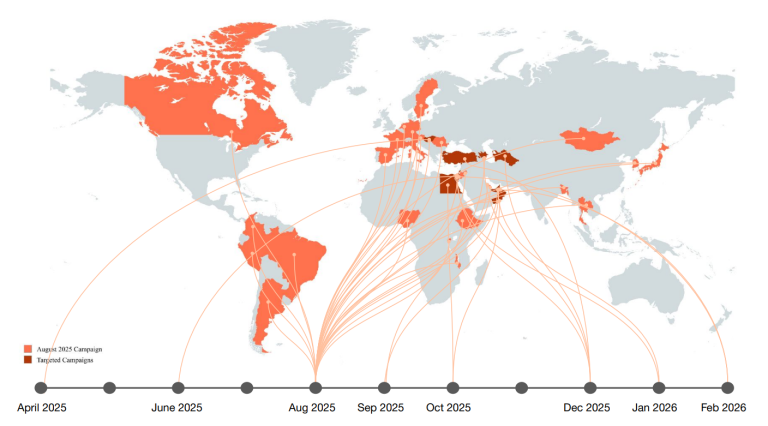
Unit 42 reveals Iranian APT Boggy Serpens is weaponizing hijacked accounts, AI-generated code, and Rust malware to infiltrate critical infrastructure.

Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.

MuddyWater APT deploys new "RustyWater" malware against Middle East targets. CloudSEK reveals how the group is ditching PowerShell for stealthy Rust tools.

Darktrace exposed Xillen Stealer v4/v5, a new MaaS threat using Rust polymorphism and an AIEvasionEngine to target 100+ browsers and Kubernetes/DevOps secrets. It uses steganography for exfiltration.

Learn about the dangerous new Rust-based malware, Fickle Stealer, and its threat to cybersecurity. Stay informed to protect your sensitive information.

Dubbed Operation RusticWeb, this campaign, uncovered in October 2023, demonstrates a nuanced approach to cyber espionage.