
 Do Son
Learn about the critical SQL injection flaw (CVE-2024-42327) in Zabbix and its potential impact on monitoring data and system security.
sql injection
Learn about the high-severity SQL injection flaw CVE-2024-20536 in Cisco Nexus Dashboard and the critical risk it poses to network security.

Centreon issued a critical security bulletin addressing multiple SQLi flaws (CVE-2024-33852 & CVE-2024-33853) in its Centreon Web interface

proof-of-concept (PoC) and technical details for CVE-2024-39911 have already surfaced, raising the specter of widespread exploitation

CVE-2024-6457 leaves over 100,000 WooCommerce-powered online stores susceptible to unauthorized data breaches
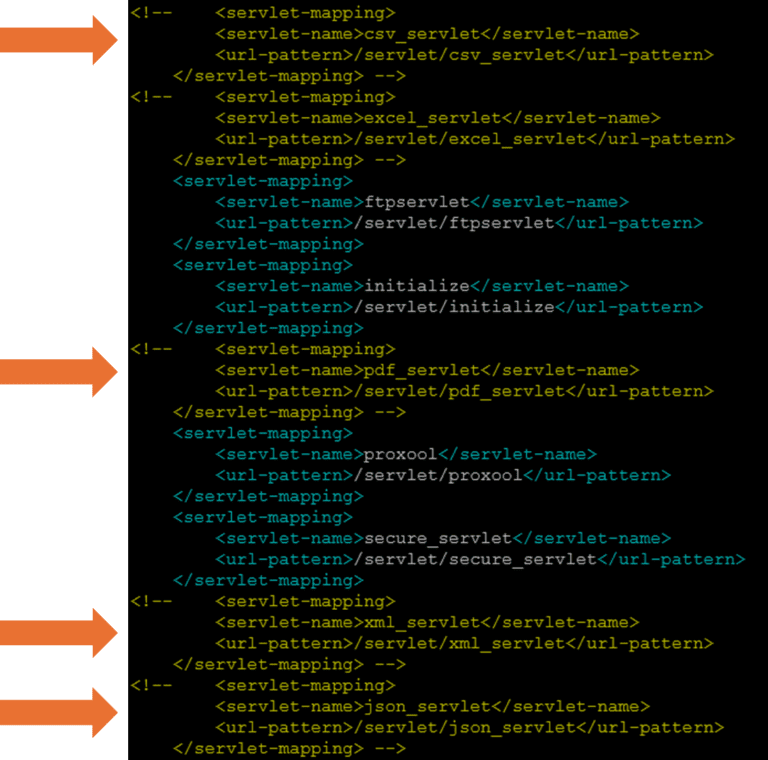
Tenable Research, who discovered and reported the CVE-2024-5276 flaw, has released a proof-of-concept (PoC) exploit code

Researchers have demonstrated that teams of AI agents, powered by large language models, can successfully exploit zero-day vulnerabilities

With a CVSS score of 10, CVE-2024-5522 is classified as an SQL Injection (SQLi) vulnerability, a common yet dangerous type of attack

Exploiting CVE-2024-22120 allows attackers to dump any values from the database, including sensitive information

CVE-2024-21899 (CVSS 9.8): An authentication bypass vulnerability that could allow unauthorized remote access to the NAS device

A critical flaw, CVE-2024-22406 with a CVSS score of 9.3, poses a serious threat to businesses relying on this popular open-source platform

Identified as CVE-2023-48738 and rated 9.3 on the CVSS scale, this vulnerability was a ticking time bomb in the Porto theme's code.

Identified as CVE-2023-49954, this security loophole is an SQL Injection flaw found in 3CX CRM Integration.

CVE-2023-35036 is an SQL injection issue in the MOVEit Transfer web application, posing a risk to all of its versions