 Do Son
A new npm typosquatting malware campaign targets WSL environments to steal crypto wallets. Learn how this npm typosquatting malware infects systems.
Typosquatting

Microsoft found a fake Perplexity AI extension that hijacks browser search and logs keystrokes. Google pulled the malicious Chrome extension.
A Mastra supply chain attack compromised 140+ npm packages, using the typosquatted easy-day-js dependency to drop a crypto-stealing infostealer.
A new malicious PyPI package wave highlights evolving supply chain attacks. Learn how to protect your CI/CD pipelines from credential theft.

Bad actors are running FIFA website spoofing scams. Read the latest FBI World Cup alert to stay safe from fake ticket sites and data theft.
A critical npm supply chain attack exploits lookalike packages to distribute credential harvesting malware. Learn how to protect your cloud assets.

TeamPCP has open-sourced the Shai-Hulud supply chain worm. Multiple malicious typosquatted NPM packages are already weaponizing the AI-synthesized code.

A malicious unscoped "tanstack" npm package used live-debugged postinstall scripts to steal .env secrets via Svix webhooks. Check your dependencies now.

Researchers uncover a fake Telegram site distributing stealthy, memory-resident malware that bypasses Windows Defender. Always verify your download URLs.
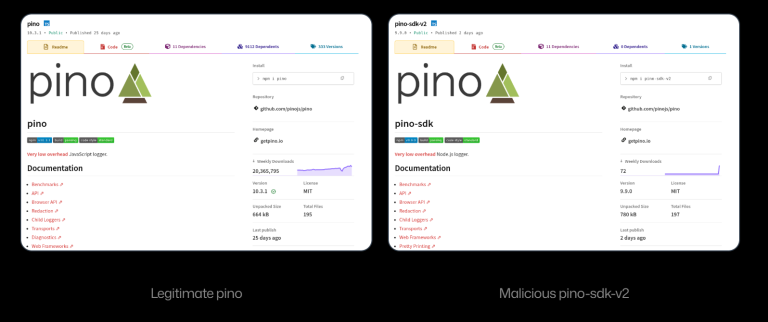
SafeDep uncovers pino-sdk-v2, a malicious npm package impersonating the pino logger to silently steal .env secrets and exfiltrate them via Discord.
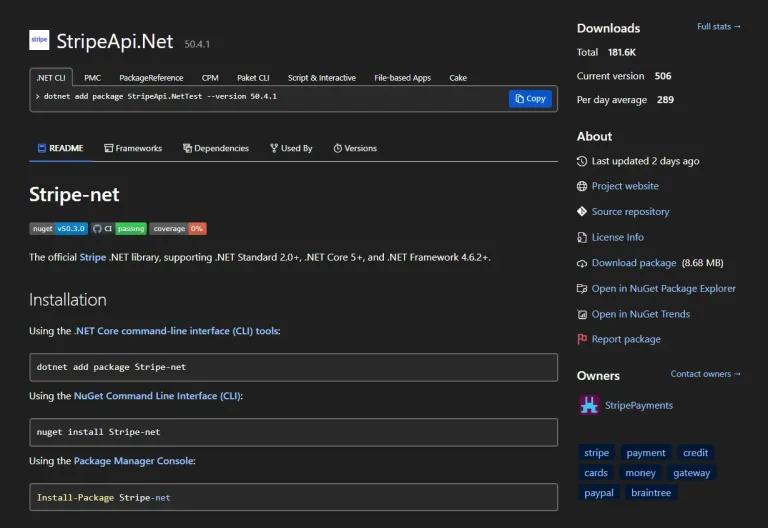
ReversingLabs uncovers a malicious NuGet package mimicking Stripe.net. Discover how attackers are targeting the financial sector via supply chain poisoning.

Tenable uncovers "ambar-src," a malicious npm package mimicking "ember-source." It uses preinstall scripts to deploy reverse shells and Apfell malware.
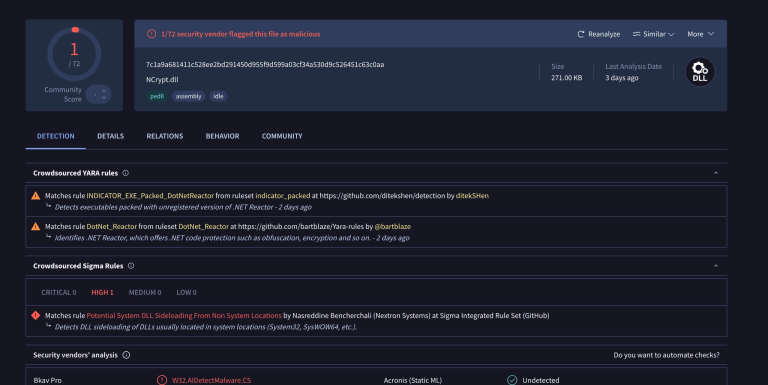
Socket researchers uncover a NuGet supply chain attack using "NCryptYo" to hijack ASP.NET apps. Attackers inject backdoors into production authorization layers.

Critical dYdX supply chain attack: Compromised npm & PyPI packages steal seed phrases & deploy RATs. Remove @dydxprotocol/v4-client-js immediately.

New "PayTool" fraud cluster targets Canadians via fake Gov & Air Canada sites. CloudSEK reveals how this PhaaS operation steals Interac logins.

Malicious PyPI package "sympy-dev" impersonates SymPy to install XMRig miners via fileless execution. Check your dependencies immediately.

Microsoft Defender's new FakeMas filter is erroneously blocking the official MAS activation script due to a typosquatted domain war. Learn the fix.

Aikido Security uncovers the first sophisticated malware on Maven Central: a "prefix swap" attack on the Jackson library used to steal data.

Attackers are using a fake MAS domain (get.activate.win) to deploy Cosmali Loader and XWorm RAT via PowerShell. Verify your command before running it!

ReversingLabs uncovered Nethereum.All, a malicious NuGet package with 10M+ fake downloads designed to drain crypto wallets and steal API secrets.

A malicious NuGet package (Tracer.Fody.NLog) stole crypto wallet data for 5 years using homoglyphs and typosquatting to evade detection. The .NET supply chain attack linked to a Russian C2 server.

19 malicious VS Code extensions bypassed detection by hiding a Rust trojan in tampered node_modules and a fake banner.png using steganography. The attack uses cmstp.exe (LOLBIN) for execution.