 Do Son
Discover how to run Googlebook OS on an Apple Silicon MacBook using QEMU virtualization, MoltenVK, and the open-source GBOS-VM project.
virtualization
Broadcom's unexpected VDDK download removal has severely disrupted VMware migrations. Learn how this impacts Azure and Red Hat enterprise transitions.
PoC exploit code is public for CVE-2026-64561 (Zapscape), a KVM escape that runs commands with kernel root privilege on the host. Details inside.
Proxmox VE Arm64 has officially launched, bringing feature parity, unified lifecycle management, and enterprise support to 64-bit Arm server architectures.
Apple releases the open-source Container 1.0.0 tool on GitHub, giving Apple Silicon Macs native, lightweight per-container Linux virtual machines.
Explore the critical Kata Containers container escape vulnerability (CVE-2026-47243). Technical details and PoC exploit code are now fully public.
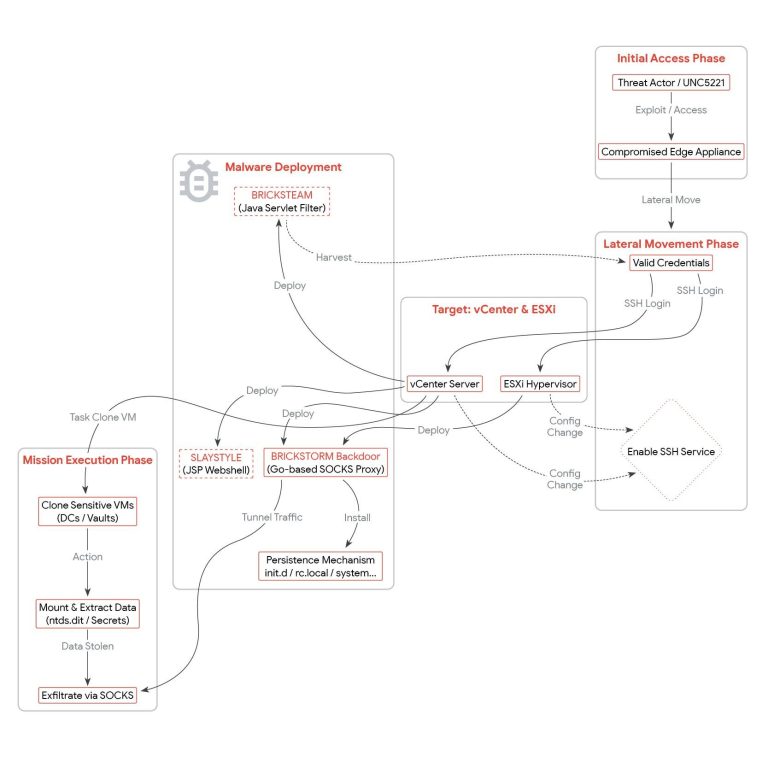
Mandiant uncovers BRICKSTORM, a threat actor hiding in VMware vSphere for 393 days. Learn how to close the visibility gap and harden your ESXi infrastructure.
AWS patches a high-severity (8.7) Firecracker flaw allowing root guests to trigger memory corruption via the virtio-pci transport. Update your microVMs now.
Parallels Desktop confirms Windows 11 runs on the $599 MacBook Neo. Discover how the A18 Pro chip handles virtualization and why 8GB RAM is the ultimate bottleneck.

Microsoft finds hackers using SolarWinds WHD to run hidden QEMU VMs. The attack uses DLL sideloading for full domain compromise. Patch immediately.

QEMU 11.0 Cloud is set to drop 32-bit host support, removing 7,000+ lines of legacy code to boost efficiency and security in cloud environments.

CVE-2025-62877: A 9.8 critical flaw in Harvester HCI allows attackers to hijack servers using default credentials during install. Update to v1.7.0!

A critical Linux KVM flaw allows guests using Intel AMX to trigger host kernel panics. Fixes are underway for modern kernels (5.17+) to prevent host DoS.

CISA/Europol updated their advisory on Akira Ransomware, confirming $244M in profits. The group now encrypts Nutanix AHV VMs and performs data exfiltration in just two hours via VPN flaws.

Bitdefender exposed Curly COMrades (Russian APT) using Hyper-V to run a hidden Alpine Linux VM. The VM hosts the CurlyShell backdoor, effectively bypassing host-based EDR for espionage.

Broadcom is shifting VMware Workstation Pro/Fusion to year-based versioning (e.g., 25H2). The new release adds dictTool for .vmx editing, USB 3.2 support, and Hyper-V VM detection.

ETH Zurich exposed RMPocalypse, a deterministic flaw in AMD SEV-SNP that bypasses memory integrity during initialization, allowing a malicious hypervisor to compromise Confidential VMs (Zen 3/4/5) with 100% success.

LineageOS 23.0, based on Android 16 QPR0, introduces a rewritten Camera app, the Catapult TV Launcher to remove ads, and enhanced virtualization capabilities.

Researchers have found a new Spectre-like attack called VMScape that allows a malicious VM to steal data from a hypervisor on Intel and AMD CPUs.

Tesco is suing Broadcom for £100M, alleging the company breached its perpetual license agreements for VMware, a move that could disrupt the retailer's operations.

Parallels Desktop 26 for Mac is out, optimized for macOS Tahoe and Windows 11 25H2. The new version adds deep integration and performance enhancements for virtualization.
Walmart has selected Broadcom's VMware Cloud Foundation to modernize its tech stack. The partnership will enable the retail giant to scale its private cloud and edge computing infrastructure.