 Do Son
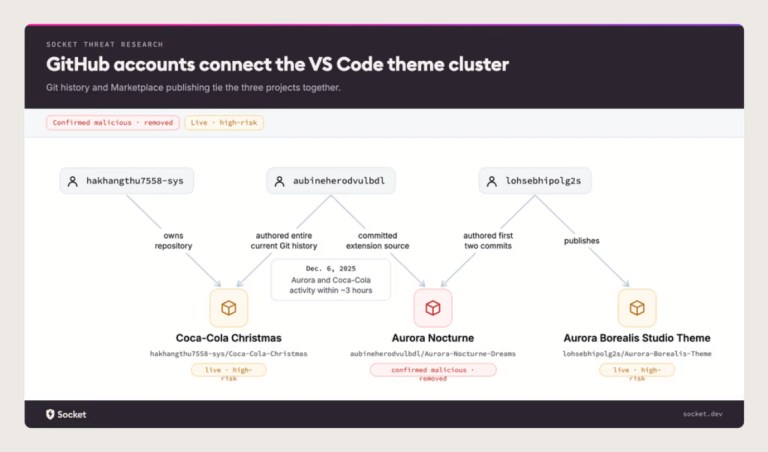
Socket links GlassWorm VS Code themes to malicious VS Code extensions with 8,000+ installs, including a Coca-Cola theme. See how to check yours.
VS Code

UNK_DeadDrop phishing campaigns are targeting developers with fake jobs to deliver Overlord malware. Learn how to defend against this North Korean threat.
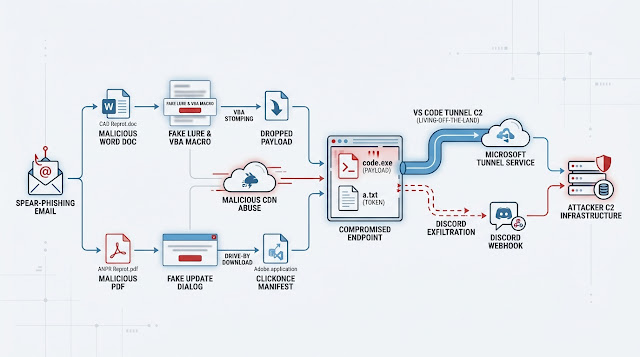
Learn how a sophisticated phishing campaign leverages VS Code Remote Tunnels abuse to bypass security and control enterprise networks.
Socket uncovers GlassWorm: a 73-extension sleeper campaign on Open VSX targeting VS Code and Cursor. Stealthy .node binaries turn trusted tools into malware.
Checkmarx Docker images and VS Code extensions hijacked by TeamPCP to siphon cloud secrets and spread via npm. Audit your "Dune" repositories today.

GitHub has suspended all Copilot Pro trials as of April 13, 2026. Learn how bad-faith exploitation forced a service-wide shutdown and what it means for you.

GitHub Copilot was caught secretly injecting ads for Raycast and Microsoft Teams into 11,000+ PRs. See how they hid the code and why developers are furious.

Socket reveals how an AI bot hijacked the Aqua Trivy VS Code extension, using prompt injection to turn developer AI assistants into stealthy data thieves.

Critical flaws in Live Server, Code Runner, and more expose 128M+ developers to file theft and remote code execution. Is your VS Code workspace secure?

"Contagious Interview" evolves: DPRK hackers now abuse VS Code tasks & npm install to breach developer systems. Jamf warns of new infection vectors.

19 malicious VS Code extensions bypassed detection by hiding a Rust trojan in tampered node_modules and a fake banner.png using steganography. The attack uses cmstp.exe (LOLBIN) for execution.

A new report reveals Chinese threat actor TA415 is targeting U.S. policy organizations with sophisticated spearphishing campaigns to gather intelligence.

A loophole in the VS Code Marketplace allows attackers to reuse names of removed extensions to spread malware, a flaw that creates a new supply chain attack vector.

A Russian crypto developer lost $500K after installing a fraudulent "Solidity Language" extension for Cursor AI IDE from Open VSX, which deployed malware for remote access and data theft.

ReversingLabs exposes a supply chain compromise of the VS Code ETHcode extension via two lines of malicious code in a GitHub PR, leading to malware deployment.

Deceptive VS Code extensions like 'solaibot' are stealing crypto wallet credentials, disabling Defender, and deploying persistent spyware on Windows.

A security flaw in code-server can expose your VS Code sessions. Learn how attackers can steal credentials and what to do.