 Do Son
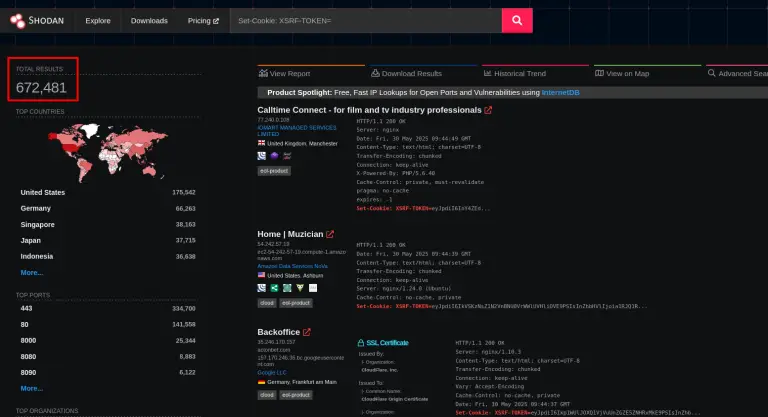
Synacktiv reveals Laravel’s APP_KEY vulnerability allows RCE via deserialization attacks when the key is leaked or guessable, risking full application compromise.
Vulnerability

A flaw in Helm (CVE-2025-53547, CVSS 8.5) allows local code execution when updating dependencies via a malicious Chart.yaml and symlinked Chart.lock file

A critical flaw (CVE-2025-6691, CVSS 8.8) in the SureForms WordPress plugin allows unauthenticated arbitrary file deletion (e.g., wp-config.php), leading to full site takeover.

GitLab releases urgent security updates to fix critical vulnerabilities, including an 8.7 CVSS score XSS flaw. Update your instances now to prevent attacks.

A Windows Update flaw (CVE-2025-48799) allows SYSTEM privilege escalation via arbitrary folder deletion using symlinks on multi-drive systems. PoC available. Patch now!

A critical flaw (CVE-2025-7206, CVSS 9.8) in D-Link DIR-825 firmware 2.10 allows unauthenticated remote buffer overflow, crashing the web interface.

Multiple critical flaws (CVE-2025-44954, -44957, -44963, -44955, -6243) in Ruckus vSZ/RND allow unauthenticated RCE, auth bypass via hardcoded SSH keys and JWT.

The Opossum Attack is a new desynchronization flaw exploiting implicit/opportunistic TLS in protocols like HTTP, allowing MitM to compromise encrypted connections. Over 3M servers affected.

Schneider Electric warns of critical flaws (CVSS 10.0 RCE, SSRF, EoP) in EcoStruxure IT Data Center Expert. Patch to v9.0 immediately to prevent data center disruption.

GeoServer's RCE flaw (CVE-2024-36401) is actively exploited to deploy NetCat reverse shells and XMRig CoinMiners on Windows/Linux, hijacking resources.

CISA warns of critical flaws in Emerson ValveLink software, exposing cleartext data, allowing code execution, and compromising industrial systems. Update to v14.0 now.

HPE Aruba warns of critical flaws in Instant On Access Points (CVE-2025-37103) allowing unauthenticated admin bypass via hardcoded credentials and authenticated command injection.

Zoom rolls out security updates for 6 newly disclosed flaws in Workplace, Rooms, and SDK, addressing DoS, info disclosure, and XSS across all platforms. Update now!

The Git Project has released updates addressing three significant vulnerabilities impacting Git versions up to v2.50.0, including...

Siemens warns of critical flaws (CVE-2025-40736 CVSS 9.8 Auth Bypass, SQLi, Path Traversal) in SINEC NMS, allowing unauthenticated remote root access and RCE.
Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)

Citrix Warns of Privilege Escalation Vulnerability in Windows Virtual Delivery Agent (CVE-2025-6759)
Citrix warns of a high-severity local privilege escalation flaw (CVE-2025-6759, CVSSv4 7.3) in Windows VDA, allowing low-privileged users to gain SYSTEM access.

Apache Tomcat 9.0.107 patches three critical DoS flaws (CVE-2025-52434, CVE-2025-52520, CVE-2025-53506) that can disrupt web services via HTTP/2, file uploads, and excessive streams.

Fortinet released a critical patch for FortiWeb (CVE-2025-25257, CVSS 9.6). This unauthenticated SQL injection flaw allows remote code execution; update immediately!

Phoenix Contact warns of critical flaws (CVE-2025-25270 CVSS 9.8 RCE, CVE-2025-25268 Auth Bypass, CVE-2025-25271 OCPP Reconfig, CVE-2025-25269 LPE) in CHARX SEC-3xxx EV controllers.

MediaTek's July 2025 bulletin reveals critical flaws in chipsets, enabling local EoP, remote RCE, and info disclosure in smartphones, AIoT devices, and smart TVs.

SAP's July 2025 Patch Day fixes 27 vulnerabilities, including critical RCE (CVSS 10.0) in Live Auction Cockpit and multiple insecure deserialization flaws (CVSS 9.1) across NetWeaver components.

MongoDB has patched two flaws: CVE-2025-6713 (CVSS 7.7) allows privilege escalation via $mergeCursors, and CVE-2025-6714 (CVSS 7.5) causes mongos DoS.