
 Do Son
A critical RCE flaw (CVE-2025-47812, CVSS 10.0) in Wing FTP Server allows unauthenticated attackers to execute arbitrary Lua code via NULL byte injection, compromising the server
Vulnerability

A critical flaw (CVE-2025-6463, CVSS 8.8) in Forminator WordPress plugin allows unauthenticated arbitrary file deletion, leading to site takeover.

Critical CVSS 9.8 RCE in Netflix Conductor lets attackers gain remote shell via JavaScript injection. Exploit PoC available. Patch now!

DataEase has critical flaws in database connection handling, allowing remote RCE and JDBC parameter bypasses for H2, Redshift, and PostgreSQL. Update to v2.10.11 now!

A flaw (CVE-2025-53106) in Graylog allows authenticated users to escalate privileges via API token abuse. Update to 6.2.4 or 6.3.0-rc.2 immediately.

Three flaws in Frappe Framework allow account takeover via password reset token leaks, XSS via file upload, and SQL injection. Update self-hosted ERPNext immediately!

CERT@VDE and Pilz disclose critical flaws in IndustrialPI 4: unauthenticated remote bypass (CVSS 9.6) and RCE (CVSS 10.0) via exposed Node-RED. Update or mitigate immediately.

Electron has critical flaws: CVE-2024-46993 allows RCE via image buffer overflow, and CVE-2024-46992 is an ASAR integrity bypass on Windows.

A critical CSRF flaw (CVE-2025-53095, CVSS 9.7) in Sunshine game streaming host allows remote attackers to execute arbitrary system commands with admin privileges.

Two Sudo flaws (CVE-2025-32463 & CVE-2025-32462) allow local users full root via PoC. Critical privilege escalation vulnerabilities revealed by Stratascale CRU.

A critical flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway is actively exploited for DoS. Over 2,100 unpatched appliances remain susceptible. Update immediately!

A critical vulnerability—CVE-2025-49596—affected the AI developer ecosystem in June 2025, when Oligo Security Research disclosed a severe...

Google has urgently patched a high-severity zero-day (CVE-2025-6554) in Chrome's V8 JavaScript engine. This type confusion flaw is actively exploited in the wild, risking RCE.

A critical flaw (CVE-2025-6328) in D-Link's EOL DIR-815 router allows remote code execution via a stack-based buffer overflow. No patches will be issued.

Citrix Bleed 2 (CVE-2025-5777, CVSS 9.2) is actively exploited to hijack sessions and bypass MFA on NetScaler ADC/Gateway. Patch immediately to prevent covert access and data theft.

Six critical flaws in D-Link's EOL DIR-816 routers are exposed. No patches will be issued; replace device immediately to avoid remote code execution.

A flaw (CVE-2025-4679) in Synology ABM leaked a static client_secret, allowing unauthenticated attackers read-only access to all Microsoft 365 tenants with ABM installed.

MongoDB discloses CVE-2025-6710 (CVSS 7.5), a pre-authentication DoS flaw. Crafted JSON inputs can crash servers via stack overflow.
IBM warns of a critical RCE flaw (CVE-2025-36038) in WebSphere Application Server 8.5/9.0, allowing unauthenticated attackers to execute arbitrary code via serialization.
A critical flaw (CVE-2025-6561, CVSS 9.8) in Hunt Electronic DVRs allows unauthenticated remote attackers to access configuration files and obtain plaintext admin credentials.
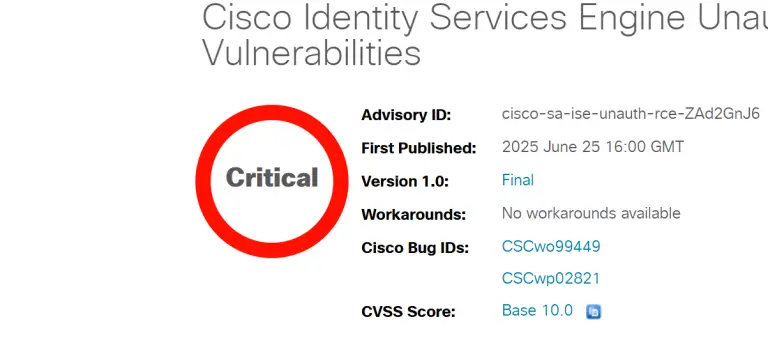
Cisco warns of two critical flaws (CVE-2025-20281, CVE-2025-20282, CVSS 10.0) in ISE and ISE-PIC allowing unauthenticated remote root code execution. Apply patches immediately.
Citrix warns of a critical memory overflow flaw (CVE-2025-6543, CVSS 9.2) in NetScaler ADC/Gateway, actively exploited for DoS. Update to patched versions immediately!