
 Do Son
Google has released a critical Stable Channel update for Chrome Desktop (version 138.0.7204.157/.158), addressing six security vulnerabilities,...
Vulnerability

A newly discovered Server-Side Template Injection (SSTI) vulnerability in the widely-used LaRecipe documentation tool has been assigned...

The Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2025-47812 to its Known Exploited Vulnerabilities (KEV) Catalog...

A flaw has been discovered in ImageMagick, the widely used open-source image manipulation suite, that could lead...

A critical vulnerability has been disclosed in Immich, a rapidly growing open-source project for self-hosted photo and...

A critical remote code execution (RCE) vulnerability has been discovered in the Symantec Endpoint Management suite, also...

A critical XML External Entity (XXE) vulnerability has been identified in multiple versions of Apache Jackrabbit, a...

A critical vulnerability (CVE-2025-7503) has been uncovered in an IP camera manufactured by Shenzhen Liandian Communication Technology...

A critical security flaw in Fortinet’s FortiWeb web application firewall has been publicly weaponized, with proof-of-concept (PoC)...

In a warning issued by CERT/CC, multiple high-impact vulnerabilities have been identified in Gigabyte UEFI firmware that...

Axis Communications has issued a security advisory for a critical vulnerability affecting several of its flagship software...

Rockwell Automation has issued a security advisory detailing two vulnerabilities affecting its Arena Simulation software. Disclosed by...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has officially added CVE-2025-5777 to its Known Exploited Vulnerabilities...

The Apache Software Foundation has issued a new release—Apache HTTP Server version 2.4.64—patching eight security vulnerabilities that...

On July 1, 2025—just a day after its public disclosure—Huntress witnessed the active exploitation of a critical...

Juniper Networks, a cornerstone in enterprise-grade network security, has issued a critical alert for a Missing Authorization...
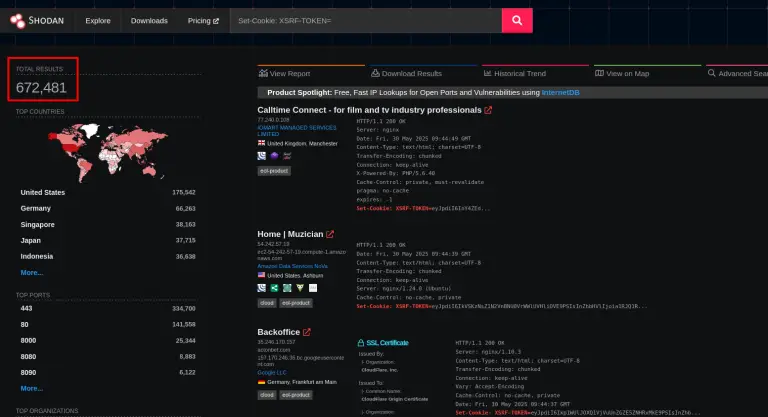
A recent technical deep-dive by Synacktiv has exposed a serious yet often overlooked risk in Laravel—the popular...

The Helm project—the popular Kubernetes package manager—has released a critical security advisory for CVE-2025-53547, a high-severity vulnerability...

A critical vulnerability in the SureForms WordPress plugin—which has over 200,000 active installations—has exposed websites to a...

GitLab has released security updates for its Community Edition (CE) and Enterprise Edition (EE), addressing multiple vulnerabilities...

Security researcher Filip Dragović has been credited by Microsoft for uncovering CVE-2025-48799, a local privilege escalation (LPE)...