
 Do Son
Codecentric detailed the CVE-2022-46166 discovered in the Spring Boot Admins prior version < 2.6.10, prior version < 2.7.8, and < prior version 3.0.0-M6
Vulnerability

The bug, assigned the identifier CVE-2022-20968, has been described as a stack-based buffer overflow, caused by improper bounds checking

CVE-2022-23494 affecting the TinyMCE rich text editor can be exploited for privilege escalation, obtaining information, or account takeover.

CVE-2022-31696 has been assigned an “important” severity rating, which is equivalent to “high severity” based on its CVSSv3 score of 7.5.

daloRADIUS project addressed a high-security vulnerability (CVE-2022-23475), if successfully exploited, could result in an account takeover.

CVE-2022-45313, was caused by a lack of proper validation that allows attackers to remotely execute code on affected devices.

Tracked as CVE-2022-46164, the issue has a CVSS severity score of 9.4. The security flaw affects all versions of NodeBB prior < 2.6.1
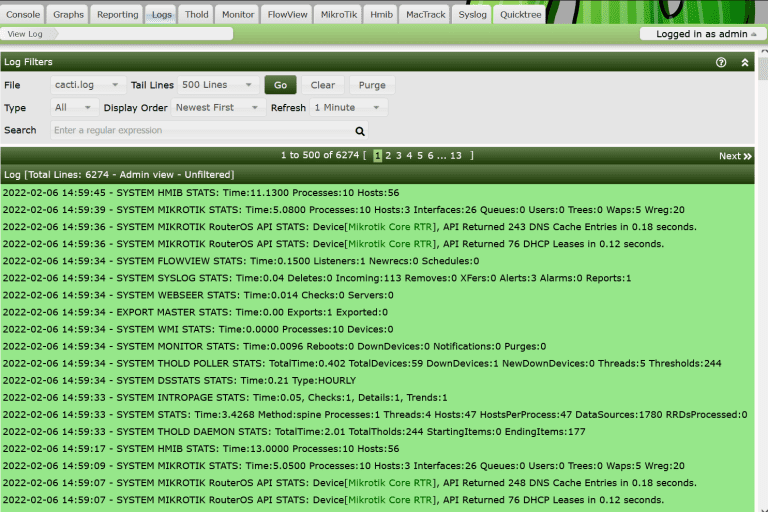
CVE-2022-46169 is a command injection vulnerability that allows unauthenticated attackers to execute arbitrary code on a server running Cacti

Wh04m1001 has made public a PoC code for CVE-2022-41120 that allows an attacker to achieve elevation from local user to SYSTEM admin.
Successful exploitation of CVE-2022-46414 could allow the attacker to gain remote command execution on affected systems.

Tracked as CVE-2022-4262, the high-severity vulnerability has been described as a Type Confusion in the V8 JavaScript engine
As a PoC demonstration, the researchers showed it was possible to exploit CVE-2022-41034 to execute arbitrary code on the system

CVE-2022-23093 can be leveraged to cause a stack overflow, which could lead to a crash or trigger remote code execution in the ping
CVE-2022-4139 affected Linux kernel stable branches and is a result of a security-sensitive bug in the Linux kernel's GPU i915 kernel driver.

CVE-2022-41325 is a buffer overflow that resides in the vnc module and can be triggered using a malicious vnc URL.

An attacker could use the CVE-2022-31097 vulnerability to steal the victim's cookie-based authentication credentials.

CVE-2022-46146 exists in the exporter toolkit that allows hackers who know the hashed password to authenticate against Prometheus.

CVE-2022-44635 allowed an authenticated user to perform RCE due to a path traversal flaw in a file upload component of Apache Fineract

The vulnerability, tracked as CVE-2022-4020, exists in the automatically deployed DXE driver HQSwSmiDxe on some Acer consumer laptops
Cyfirma issued a bulletin warning of CVE-2022-34721 vulnerability affecting Windows systems that is currently being actively exploited in the wild
By using shell metacharacters in the name of a source-code file, attacker could exploit CVE-2022-45939 to execute arbitrary commands on the system
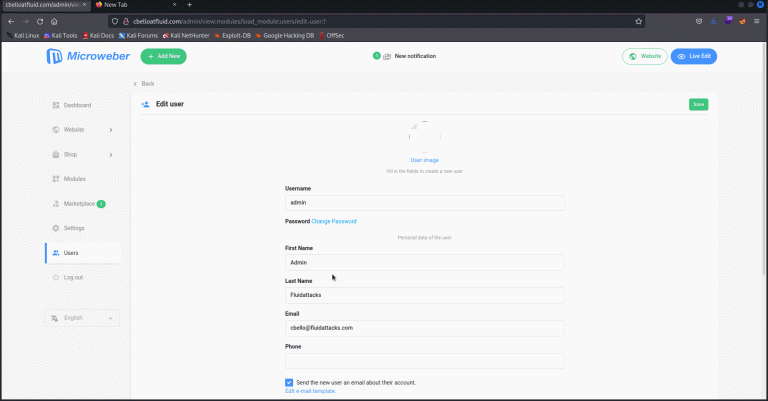
CVE-2022-0698 affects Microweber 1.3.1 and allows an unauthenticated remote attacker to perform an Account Takeover.