
 Do Son
Cacti has recently released a crucial security update to address two significant vulnerabilities (CVE-2024-29895 & CVE-2024-30268)
Vulnerability

The vulnerability, identified as CVE-2024-4761, is an “Out of bounds write” flaw found in V8, Chrome’s JavaScript engine

The vulnerability, CVE-2024-35205, arises from the application's failure to properly sanitize filenames before processing them

PowerDNS, a widely used open-source DNS software provider, has issued a security advisory regarding a vulnerability (CVE-2024-25581)
Among the most alarming vulnerabilities addressed in this update is CVE-2024-25641, with a CVSS score of 9.1.
the update also fixes two other 'High' severity flaws and a unique 'Low' severity vulnerability specific to Microsoft Edge (CVE-2024-30055

Dor Segal has revealed a critical vulnerability in FIDO2, the popular passwordless authentication standard

NHS England Digital has issued a critical alert concerning vulnerabilities in Arcserve’s Unified Data Protection (UDP) software

A serious vulnerability (CVE-2024-32113) has been uncovered in Apache OFBiz, a popular suite of enterprise software tools
CVE-2024-4434 (CVSS score of 9.8), is an unauthenticated time-based SQL Injection through the ‘term_id’ parameter.

The vulnerabilities, tracked as CVE-2024-28075 and CVE-2024-23473, were discovered by ZDI vulnerability researcher Piotr Bazydło

The flaw, tracked as CVE-2024-27793, was discovered by Willy R. Vasquez, a security researcher at The University of Texas at Austin.

A high-severity security vulnerability (CVE-2024-32655) has been discovered in Npgsql, a widely used open-source data provider

Technical details have emerged about a significant security vulnerability, CVE-2024-21115, which has been discovered in Oracle VM VirtualBox
The flaw, designated CVE-2024-4671, is a "use after free" bug located within the browser's "Visuals" component.

Recent discoveries have exposed CVE-2024-34350 & CVE-2024-34351 which could compromise user data and server operations

CVE-2024-4701 (CVSS 9.9) has been discovered in Genie, Netflix's popular open-source job orchestration engine for big data processing

CVE-2024-3806 (CVSS 9.8): An unauthenticated LFI vulnerability within the porto_ajax_posts function of the Porto theme

CVE-2024-32980 (CVSS 9.1) has the potential to allow network sandbox escapes in specifically configured Spin applications.
The Qt Group has released a security advisory and accompanying patch in response to a vulnerability (CVE-2024-33861)
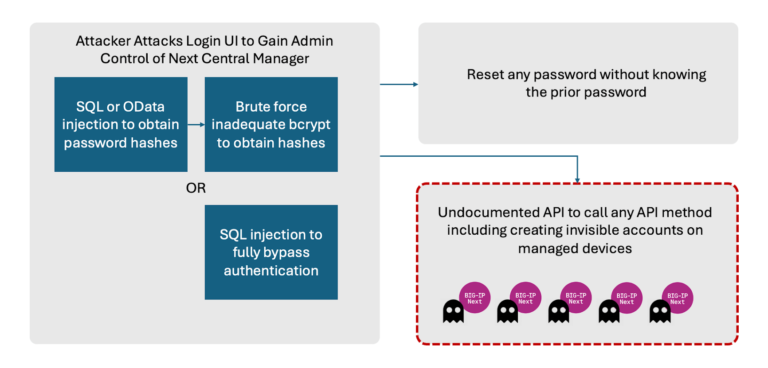
A recent investigation by Eclypsium, a prominent supply chain security firm, has unveiled a series of critical...

These flaws could potentially allow arbitrary code execution (CVE-2024-24787) and cause infinite loops (CVE-2024-24788) in DNS operations