
 Do Son
A CVE-2024-20376 flaw in the web-based management interface could allow attackers to send specially crafted requests
Vulnerability

CVE-2024-32971 vulnerability with a CVSS score of 9.1, has been discovered in versions 1.44.0 and 1.45.0 of the Apollo Router

CVE-2024-32962, carries the highest severity score of 10 on the Common Vulnerability Scoring System (CVSS), indicating its critical nature
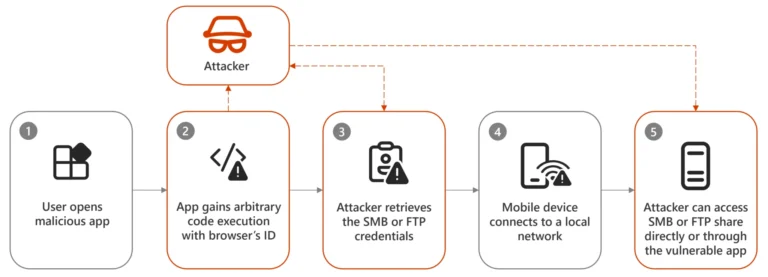
Dirty Stream exploits path traversal vulnerabilities when applications share data using Android's ContentProvider components

HPE Aruba Networking announced a comprehensive update to its ArubaOS software, targeting multiple critical vulnerabilities

Goldoon botnet is ruthlessly exploiting a CVE-2015-2051 vulnerability in D-Link devices to commandeer them for malicious activities

CVE-2024-29010 & CVE-2024-29011 could be exploited by attackers to gain unauthorized access to sensitive data and bypass authentication mechanisms

Cisco Talos have unveiled a coordinated threat actor campaign dubbed "ArcaneDoor," targeting government-owned network devices globally

CVE-2024-27790 could have potentially enabled attackers to gain access to records they should not have been authorized to see or modify.
CISA added a recently patched Microsoft vulnerability (CVE-2024-29988) to its Known Exploited Vulnerabilities (KEV) catalog

CVE-2024-2912 vulnerability lies in the way the software handles data, allowing attackers to run arbitrary code on servers running BentoML

A serious security vulnerability (CVE-2024-32656) foun in Ant Media Server, a popular streaming solution used by thousands of organizations
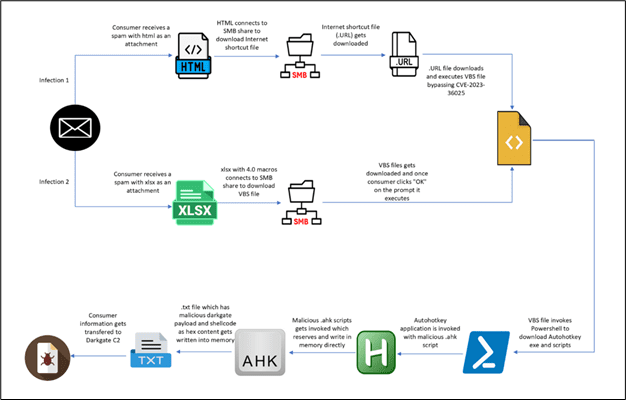
DarkGate, identified as a Remote Access Trojan (RAT), poses a formidable threat due to its array of functionalities including data theft

Researchers from HiddenLayer have discovered a significant vulnerability in the R programming language, tracked as CVE-2024-27322

Modzero unveiled a series of severe vulnerabilities in MailCleaner, a widely-used email filtering appliance designed to protect against spam

If left unpatched, the CVE-2024-33891 (CVSS 8.8) vulnerability allows attackers to bypass authentication completely
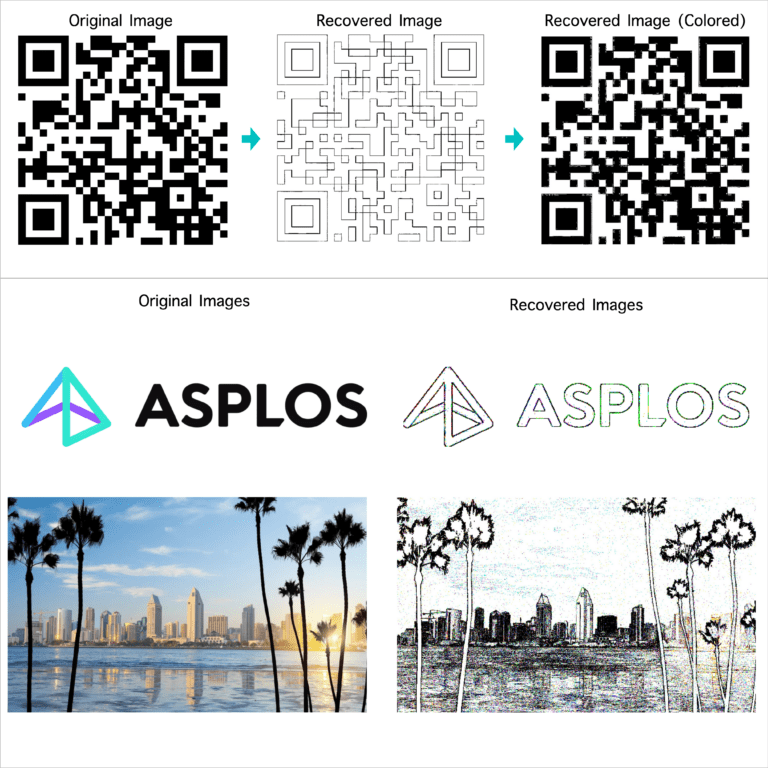
The Pathfinder attack exposes two high-resolution side-channel attacks leveraging the Conditional Branch Predictor (CBP)

CVE-2024-32766 (CVSS 10) is an OS command injection, a technique where attackers can send malicious commands to a vulnerable system

The vulnerability, now patched, resided in Telegram's "Mini App" system. These mini web applications, designed to run within Telegram

Cybersecurity researcher shared technical details and PoC exploit for a high-severity EoP flaw (CVE-2024-26218) bug affecting Windows Kernel.

Cato Networks reported intercepting several attempts aimed at installing the XMRig cryptocurrency mining malware using this vulnerability

Mitel's Security Bulletin 24-0011-001 details a critical stored XSS vulnerability in the Ignite component of MiContact Center Business