
 Do Son
Security researchers have uncovered a critical vulnerability (CVE-2024-2796) within the Perforce Akana Community Manager Developer Portal
Vulnerability
Laravel Framework Hit by Data Exposure Vulnerability (CVE-2024-29291) – Database Credentials at Risk

Laravel Framework Hit by Data Exposure Vulnerability (CVE-2024-29291) – Database Credentials at Risk
CVE-2024-29291 affects versions 8.* through 11.* of Laravel and has the potential to expose sensitive database login credentials.

A discovered flaw in the GNU C Library's (glibc) iconv function (CVE-2024-2961) carries severe implications for web applications built on PHP

Exploit code is now available for a critical vulnerability (CVE-2024-29204, CVSS 9.8) that has been identified in Ivanti Avalanche

Cisco customers are facing an increased risk of attack as publicly accessible exploit code has emerged for CVE-2024-20356

CVE-2024-20380 could allow unauthenticated, remote attackers to crash ClamAV services, causing a Denial-of-Service (DoS) condition.

A recent security advisory has shed light on a vulnerability (CVE-2024-32462) within Flatpak, a popular framework for packaging

Keycloak, a widely used open-source solution for authentication and authorization, has released important security updates addressing multiple flaws

This critical vulnerability (CVE-2024-28890) allows attackers to upload malicious files of dangerous types to a vulnerable website

The attack typically begins with cybercriminals scanning for internet-exposed Kubernetes workloads running vulnerable OpenMetadata instances

HashiCorp has issued an urgent security advisory regarding a critical vulnerability (CVE-2024-3817) within its widely used go-getter library
PSIRT has confirmed that proof-of-concept exploit code exists for the IMC command injection vulnerability (CVE-2024-20295
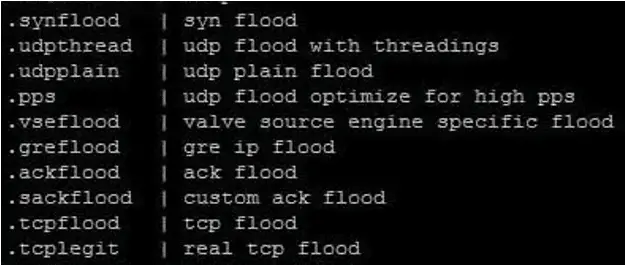
This vulnerability, found in the TP-Link Archer AX21's web management interface, allows hackers to inject malicious code without needing the router's password
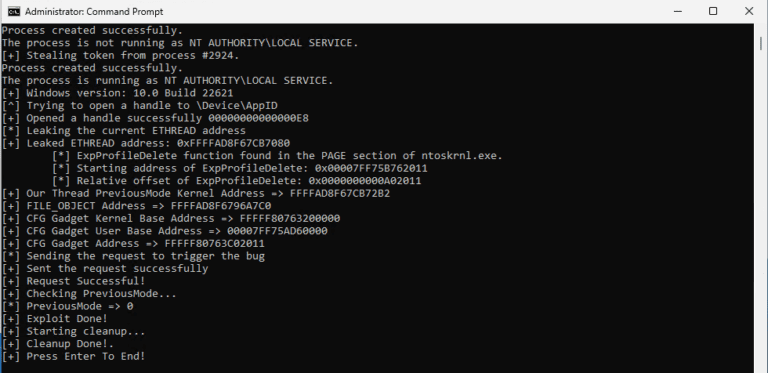
Security researchers published the technical details and PoC exploit code for a dangerous zero-day CVE-2024-21338 vulnerability
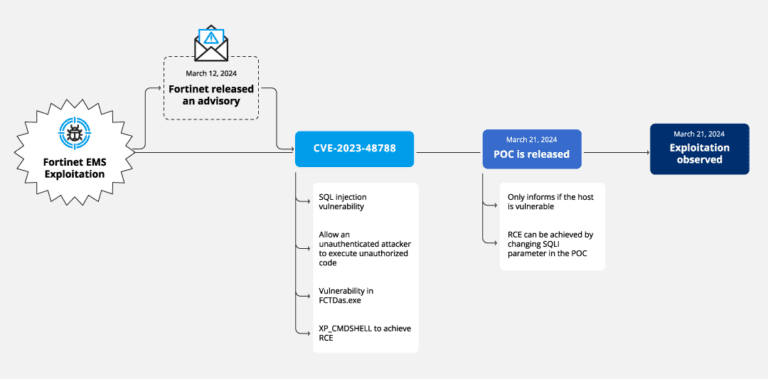
A newly exposed attack campaign, dubbed "Connect:fun," is raising alarms in the media sector, Forescout Research – Vedere Labs warns
A serious security vulnerability (CVE-2024-32019) has been discovered in Netdata, a widely used open-source monitoring and troubleshooting tool
The CVE-2024-3652 vulnerability lies in Libreswan's handling of IKEv1 connections when certain default settings are in place.

A severe security flaw (CVE-2024-31497) has been discovered in the popular SSH client PuTTY (versions 0.68 to 0.80)
CVE-2024-2876 (CVSS score of 9.8) allows unauthenticated attackers to inject malicious code into WordPress sites using the plugin

CVE-2024-1874 (Critical): Improper command-line handling on Windows systems could allow attackers to inject arbitrary commands

Akamai researcher Ben Barnea has released the technical details and PoC for a severe CVE-2023-35628 vulnerability in Microsoft Windows

Security researchers at Redline Cyber Security have revealed a severe security flaw (CVE-2024-22734) within Trux