
 Do Son
CVE-2024-3116 allows attackers to execute malicious code on servers running pgAdmin, potentially compromising the entire database system.
Vulnerability
A vulnerability (CVE-2024-31498) with a CVSS score of 7.7 was discovered, allowing attackers to exploit elevated privileges on Windows systems

The critical severity of CVE-2024-29008 highlights the risk of potential infrastructure takeover if left unpatched.

attacks exploiting unpatched vulnerabilities result in significantly more severe outcomes than those leveraging compromised credentials

Security researchers have uncovered three vulnerabilities in the widely used Apache HTTP Server, prompting an urgent call for users
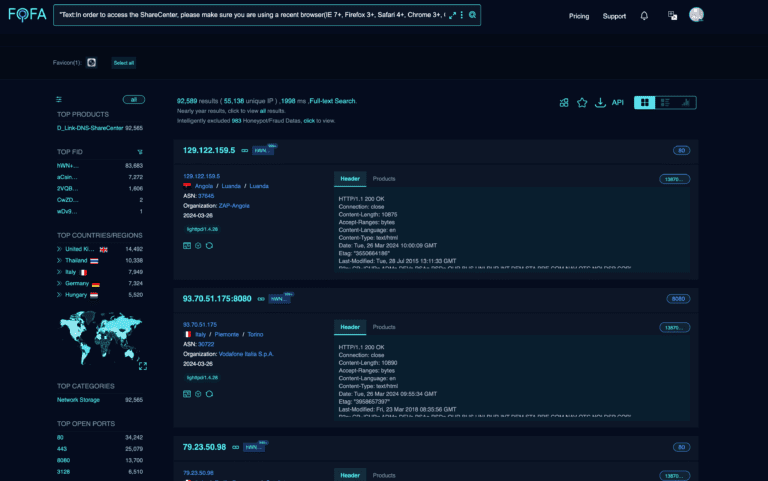
Security researchers have uncovered a serious vulnerability (CVE-2024-3273) in several D-Link Network Attached Storage (NAS) devices

Server Crash Vulnerability (CVE-2024-27983): This high-severity vulnerability resides within Node.js's HTTP/2 server
A recent security advisory from Veridium has exposed a series of significant vulnerabilities in their popular VeridiumID authentication platform

Ivanti has released an urgent security advisory detailing multiple critical vulnerabilities affecting their popular ICS and Policy Secure gateways

A researcher found multiple high-severity vulnerabilities in the REHub WordPress theme and the associated REHub Framework plugin

Two of these vulnerabilities, labeled CVE-2024-29745 and CVE-2024-29748, are already being exploited by bad actors

VMware has released critical security patches to address multiple vulnerabilities in its SD-WAN (Software-Defined Wide Area Network) solution
The flaw, designated CVE-2024-3159, involves an out-of-bounds memory access vulnerability in the V8 JavaScript engine.
The vulnerability, designated CVE-2024-2879 with a CVSS score of 9.8, could allow unauthenticated attackers to inject malicious SQL code
The flaw, designated as CVE-2024-2389, could give attackers unfettered access to sensitive network infrastructure.

The flaw, tracked as CVE-2024-29834, enables unauthorized users to make changes to sensitive data streams and system access rules.
Octopus Deploy has released a security advisory and subsequent patches to address a critical vulnerability (CVE-2024-2975

The most serious of these vulnerabilities (CVE-2024-21473) carries a CVSS score of 9.8 and could allow attackers to corrupt device memory

JumpServer has recently been found to contain CVE-2024-29201 and CVE-2024-29202 that could allow attackers to execute arbitrary code remotely

Successful exploitation of CVE-2023-6154 (CVSS 7.8) requires the attacker to have local access to the target machine.
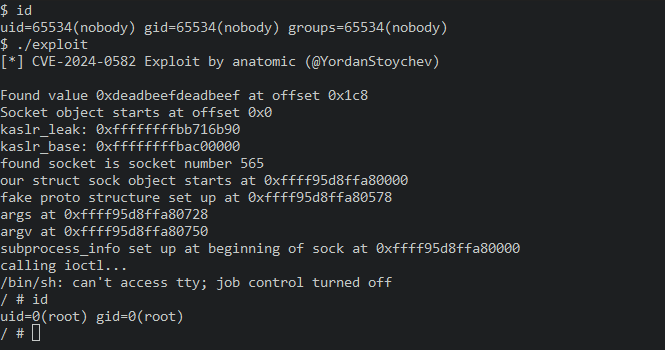
Researchers have provided a detailed analysis of the CVE-2024-0582 vulnerability, including a proof-of-concept (PoC) exploit

CVE-2024-23538 and CVE-2024-23539: These vulnerabilities stem from improper neutralization of special elements used in an SQL command