
 Do Son
Identified as CVE-2024-2194 with a CVSS score of 7.2, this vulnerability is classified as a stored cross-site scripting (XSS) issue
Vulnerability

PoC exploit code will be released at "a later date "for a high-severity CVE-2024-21378 flaw allowing RCE in Microsoft Outlook
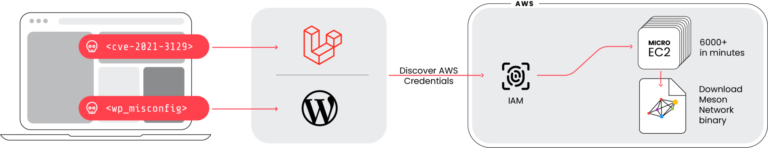
Security researchers have exposed a crafty attack campaign manipulating a decentralized content delivery network (CDN)

A flaw (CVE-2024-2370, CVSS 9.8) has been discovered in older versions of ManageEngine Desktop Central, developed by Zoho Corporation

Security researchers at GuidePoint have uncovered a new weapon in the BianLian ransomware gang’s arsenal – a...

The vulnerability, designated as CVE-2024-22252, could potentially allow attackers to execute malicious code on affected systems.

CVE-2024-22857 is a heap-based buffer overflow that could allow attackers to remotely execute arbitrary code on systems

CVE-2023-41313 allows attackers to exploit weaknesses in the authentication process within Apache Doris using a timing attack

The company's investigation revealed three previously unknown vulnerabilities in popular tools used for font processing and manipulation
Canon has released a security bulletin addressing a buffer overflow vulnerability (CVE-2024-2184, CVSS 9.8) in their WSD protocol process

CVE-2024-21899 (CVSS 9.8): An authentication bypass vulnerability that could allow unauthorized remote access to the NAS device

Magnet Goblin is a financially motivated threat actor demonstrating proficiency in swiftly exploiting 1-day software vulnerabilities

The Balada Injector campaign, a sophisticated malware operation, has set its sights on exploiting a vulnerability within the WordPress plugin

Kontrol and Elock locks, both utilizing firmware from the company Sciener, have been found riddled with security vulnerabilities
CVE-2023-42662: Exposure of Access Tokens (CVSS 9.3) Rated critical, this flaw compromises Artifactory's Single Sign-On (SSO) feature

CVE-2024-2044 in pgAdmin 4 could have allowed a remote, authenticated attacker to execute arbitrary code on affected systems

A severe security vulnerability (CVE-2024-28222) has been uncovered in Veritas NetBackup, the widely used enterprise backup solution
A flaw (CVE-2024-27295) was found in Directus, a versatile open-source content management platform favored by developers

Akamai offers a proof-of-concept (PoC) Theme file and video, aiding in understanding and replicating the CVE-2024-21320 vulnerability.

A vulnerability (CVE-2024-25111, CVSS 8.6) has been uncovered that could allow malicious actors to cripple Squid-powered systems

A newly discovered critical vulnerability (CVE-2024-27917) in Shopware 6, a widely used open-source e-commerce platform

Cado Security Labs' recent discovery exposed a complex malware campaign zeroing in on Linux servers misconfigured with popular cloud services