 Do Son
The vulnerability (CVE-2024-23755, CVSS 8.4) affects both macOS and Windows versions of the ClickUp Desktop app.
Vulnerability

CVE-2024-29190 allows attacker to trick the MobSF server into making requests to internal or otherwise inaccessible resources within your network

A serious security vulnerability (CVE-2024-30156) has been uncovered in Varnish Cache, a widely used tool for boosting website speed

The vulnerabilities in question, CVE-2024-29944, and CVE-2024-29943, were expertly exploited by researcher Manfred Paul (@_manfp)

Mandiant assesses with moderate confidence that UNC5174 operates as an initial access broker for the Chinese MSS.
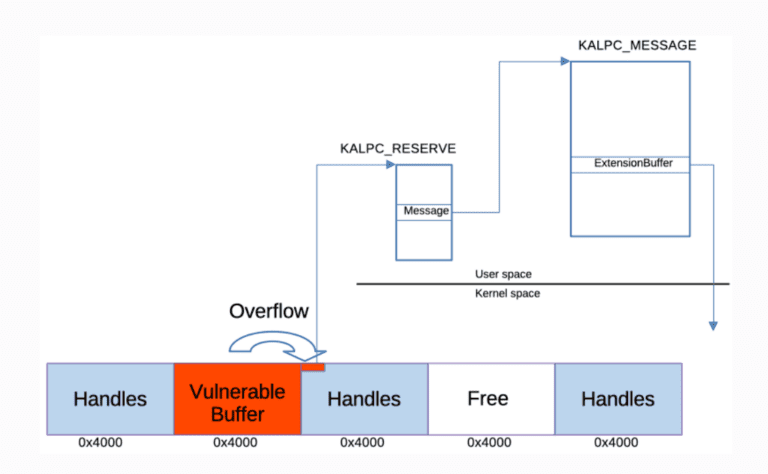
A security researcher has published details and proof-of-concept (PoC) code for a Windows CVE-2023-36424 vulnerability

Given the severity of CVE-2024-27438, Apache Doris users are strongly advised to upgrade to version 2.0.5 or 2.1.x immediately

PoC code releases for a severe vulnerability (CVE-2023-48788) in the Fortinet FortiClient Enterprise Management Server (EMS)

These flaws, tracked as CVE-2024-1147 and CVE-2024-1148, could allow attackers to upload and download sensitive files

The vulnerability, tracked as CVE-2024-2054, could allow unauthenticated attackers to execute malicious code on affected servers.

A major security flaw (CVE-2024-1800) has been discovered in the Progress Telerik Report Server, a widely used business reporting solution

A wave of cyberattacks is crashing down on organizations using the TeamCity CI/CD platform, exploiting recently disclosed vulnerabilities

Researcher published the technical details & PoC exploit for a severe flaw in Progress Kemp LoadMaster load balancers (CVE-2024-1212, CVSS 10)

CVE-2024-2615 is classified as critical & allows attackers to potentially run malicious code on your computer without your knowledge or interaction

AndroxGh0st, a sophisticated Python-based malware that exploits vulnerabilities within Laravel applications, extracting sensitive information
a popular choice for automating content imports on WordPress websites, contains two dangerous flaws (CVE-2024-27956 and CVE-2024-27954)

Proof-of-concept (PoC) code is now available for a critical severity vulnerability (CVE-2024-21762) in FortiOS SSL VPN

A serious vulnerability (CVE-2024-1753) has been discovered in the popular containerization tools Podman and Buildah

The core issue within CVE-2024-22257 lies in the way Spring Security handles authentication checks when its AuthenticatedVoter

CVE-2024-28353 and CVE-2024-28354 leave these routers alarmingly exposed to potential remote takeover by cyberattackers
These patches address two flaws (CVE-2024-23138 & CVE-2024-23139) that could have severe consequences for users of affected software versions

BlueSpy exploit highlights how the widespread use of insecure pairing methods in consumer Bluetooth headsets poses a significant privacy risk