
 Do Son
CVE-2024-22262 in the widely-used Spring Framework software could leave countless applications vulnerable to redirect and SSRF attacks
Vulnerability
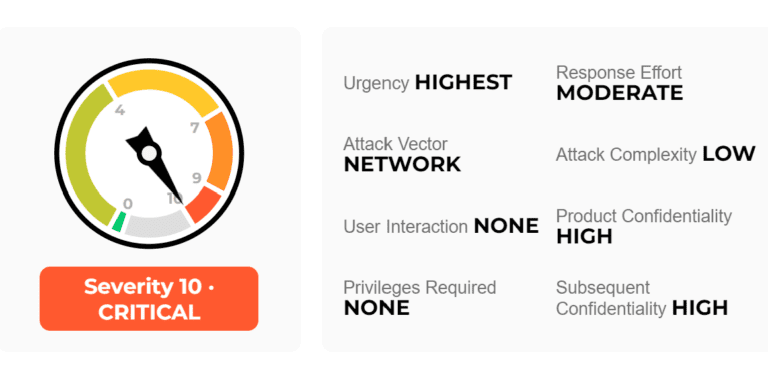
Palo Alto Networks has disclosed a severe zero-day vulnerability (CVE-2024-3400) affecting its market-leading firewall software, PAN-OS

CVE-2024-27309 could allow unauthorized access to sensitive data during the process of migrating a Kafka cluster from ZooKeeper mode to KRaft mode

Bitdefender has released critical updates to address multiple vulnerabilities in its GravityZone and Endpoint Security products
Security researchers have even developed tools, like a Metasploit module and a Python exploit script, specifically tailored to CVE-2024-31819

CVE-2024-27980: Successful exploitation could give attackers the ability to remotely run arbitrary commands on a vulnerable system.

Dubbed CVE-2024-3092, this high-severity Stored XSS issue was promptly neutralized in the latest GitLab release.
Identified as CVE-2024-31861, this flaw gives attackers a way to inject malicious code through Zeppelin's Shell interpreter

The popular Content Management System (CMS) WordPress has released a critical security update, addressing a XSS vulnerability

CVE-2024-26234 status updated: Microsoft confirms active exploitation and public disclosure of the vulnerability.

Spectre v2, an infamous name that echoes through the corridors of cybersecurity history, has found a new form in CVE-2024-2201
a security researcher from the Zero Day Initiative (ZDI) has uncovered evidence of CVE-2024-29988 being exploited in the wild

CVE-2023-45590 - A "code injection" flaw in FortiClient Linux could allow an attacker to trick a user into visiting a malicious website
The flaw, tracked as CVE-2024-24576, could potentially be exploited by attackers to gain unauthorized control of a system.
CVE-2024-0259 allows low-privileged users to gain elevated privileges, potentially granting them full control over affected systems

CVE-2023-48788, a vulnerability within the Fortinet FortiClient EMS, a security management solution pivotal

Threat actors deploy malware to hijack legitimate systems, turning them into unwilling participants in the scanning of networks for vulnerabilities

A newly uncovered path traversal vulnerability in the Java-based deployments of several CData business integration products

This flaw, designated CVE-2023-3454 (CVSS 8.6), could allow malicious actors to remotely execute code on affected switches

Dell has released a critical security patch addressing a severe vulnerability (CVE-2024-0172) in the BIOS software used on a wide range

Attackers are ruthlessly exploiting a recently patched critical vulnerability (CVE-2024-20720) in Magento. They're injecting malicious

CVE-2024-29863 could allow a malicious user with existing access to a Windows system running QlikView to escalate their privileges to the Administrator level