
 Do Son
Security researcher has released PoC exploit code for CVE-2024-21345, a high-severity Windows Kernel Elevation of Privilege vulnerability
Vulnerability
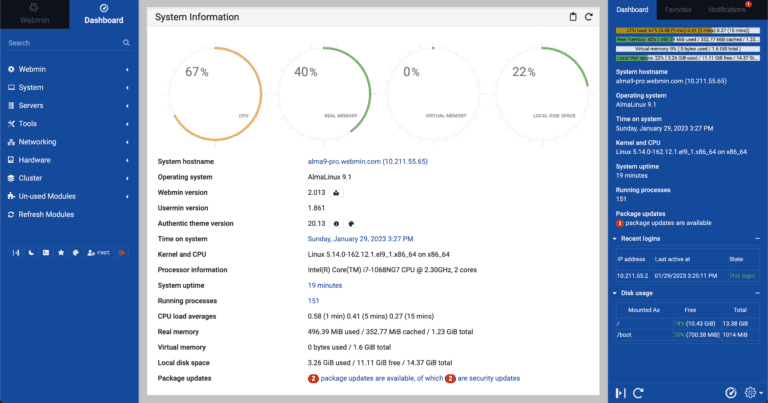
A serious security vulnerability in Webmin, a widely used web-based system administration tool for Unix-like servers, has been discovered

CVE-2023-6095, CVE-2023-6096 & CVE-2023-6116 could potentially allow unauthorized remote code execution and compromise device security.
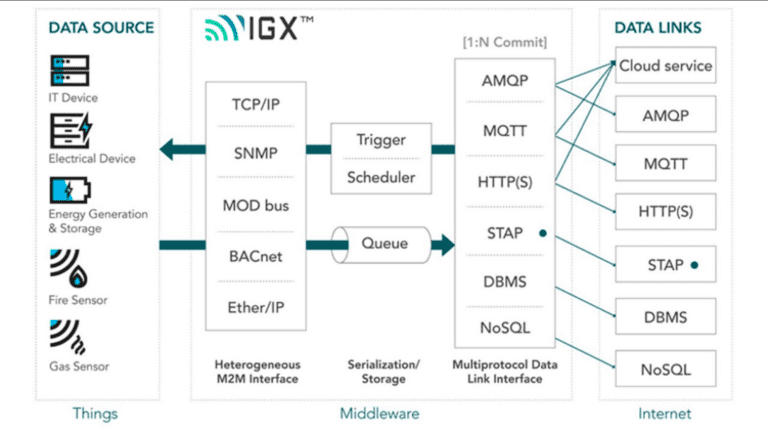
CVE-2024-4163 allows attackers to escalate their privileges and potentially take complete control of the affected devices

Rhino Security Labs has not only disclosed the CVE-2024-2389 vulnerability but has also provided a proof of concept (PoC)

The situation escalated when a security researcher known as W01fh4cker released a proof-of-concept (PoC) exploit code for CVE-2023-20198

A public-private partnership in the Netherlands has revealed critical information about a dangerous ransomware group dubbed Cactus

CVE-2024-29021, CVE-2024-28185, CVE-2024-28189 affecting Judge0 versions 1.13.0 and earlier have the potential to lead to complete system compromises
The revelation that a state-backed hacking group has been exploiting two zero-day vulnerabilities (CVE-2024-20353, CVE-2024-20359)

CVE-2024-4024: an attacker with stolen Bitbucket credentials could potentially take over a GitLab account linked to another user's Bitbucket account

Cisco has identified two vulnerabilities that were abused in the ArcaneDoor campaign (CVE-2024-20353 and CVE-2024-20359).
CVE-2024-4058 (Critical): Type confusion vulnerability in ANGLE that could lead to arbitrary code execution
The vulnerability, labeled CVE-2023-27368 (CVSS 8.4), could allow hackers to completely bypass the router's login system
popular Chinese keyboard apps transmit your keystrokes in ways that leave them shockingly vulnerable to interception

These vulnerabilities, CVE-2024-21508 and CVE-2024-21509, could have far-reaching consequences for organizations across industries.

SSRF flaw, CVE-2024-31461 with a high CVSS score of 9.1, could allow attackers to take control of servers running vulnerable Plane instances.

CVE-2024-2848 with a CVSS score of 7.5, involves a missing authorization check within the save_footer_text_callback function

Apache HugeGraph has recently addressed several critical security vulnerabilities that posed significant risks to its users

Forest Blizzard has leveraged GooseEgg to exploit a critical vulnerability in the Windows Print Spooler service, identified as CVE-2022-38028

This zero-day flaw, identified as CVE-2024-4040 with a CVSS score of 7.7, poses a severe risk to organizations

Naor Hodorov has made public a proof-of-concept (PoC) exploit for a severe vulnerability (CVE-2024-21111) in Oracle VirtualBox

Citrix has released an urgent security advisory regarding a vulnerability (CVE-2024-3902) discovered in its uberAgent software