
 Do Son
The Spring Framework, a cornerstone of countless enterprise Java applications, recently revealed a significant vulnerability (CVE-2024-22243)
Vulnerability

Atlassian has released a security update addressing CVE-2024-21678 (CVSS 8.5), a high-severity stored cross-site scripting vulnerability

Tracked as CVE-2024-1317 (CVSS 8.8), this flaw was pinpointed within all versions up to and including 4.4.2 of the Feedzy plugin

CVE-2024-21726 opens the door to multiple Cross-Site Scripting (XSS) attacks, potentially granting hackers full control of your website

If left unaddressed, threat actors could exploit these flaws (CVE-2024-22245 and CVE-2024-22250) to hijack user sessions and infiltrate sensitive systems

ConnectWise issued a critical security advisory, exposing two gaping security vulnerabilities in its popular ScreenConnect software

A disclosed vulnerability in Spring Security (CVE-2024-22234) could lead to unauthorized access within affected Java web applications
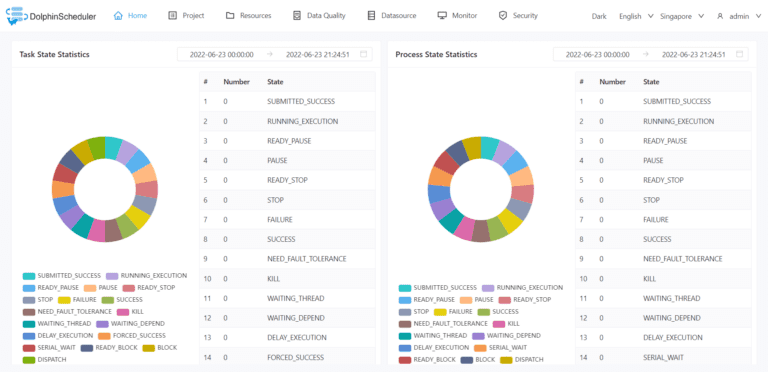
CVE-2023-49109 could potentially permit a remote attacker to execute arbitrary code on the DolphinScheduler server

Zyxel’s recent security advisory spotlights multiple vulnerabilities present in select firewall and access point models. Failure to...
A recently discovered vulnerability (CVE-2024-1597, CVSS 10) highlights the importance of vigilance and proactive security measures

Autodesk AutoCAD, a widely used CAD software across architecture, and manufacturing industries, has been found to contain 40 zero-day flaws

A flaw (CVE-2024-0646, CVSS 7.8) discovered in the Linux Kernel Transport Layer Security could have been exploited to gain elevated system privileges

The Thunderbolt interface has been notably affected, involving both software and firmware vulnerabilities.

The CVE-2024-22030 flaw carries a medium-to-high severity rating and if exploited, a malicious actor to take over existing Rancher nodes.

A PoC was disclosed for a severe design flaw (CVE-2023-50387, KeyTrap) in Domain Name System Security Extensions (DNSSEC)

A critical RCE vulnerability (CVE-2024-25600, CVSS 9.8) has been discovered in the widely used WordPress site builder, Bricks Builder

NIST has assigned CVE-2020-36773 a base score of 9.8 (out of 10) under the CVSS v3.1 system, classifying it as "Critical."

Recently disclosed vulnerabilities (CVE-2023-28078 and CVE-2023-32462) in Dell OS10 Networking Switches pose a severe threat.

A disclosed privilege escalation flaw (CVE-2024-21915) with a critical CVSS score of 9.0 exists in Rockwell's FactoryTalk Service Platform

A vulnerability in Dell EMC Enterprise SONiC (CVE-2023-32484) could have profound consequences for your data center network security

After Check Point published a technical writeup on CVE-2024-21413, the PoC code targeting the critical issue was published on GitHub

CVE-2024-23476, CVE-2024-23477, and CVE-2024-23479, these flaws represent a grave risk to the integrity & security of enterprise systems