
 Do Son
CVE-2024-25089 is a critical security vulnerability discovered in Malwarebytes Binisoft Windows Firewall Control before version 6.9.9.2
Vulnerability
CVE-2024-21399 (CVSS 8.3): there have been no confirmed instances of exploitation or disclosure of this vulnerability.

The consequences of CVE-2023-31505 are significant. This vulnerability affects the latest version of Schlix CMS, specifically version v2.2.8-1
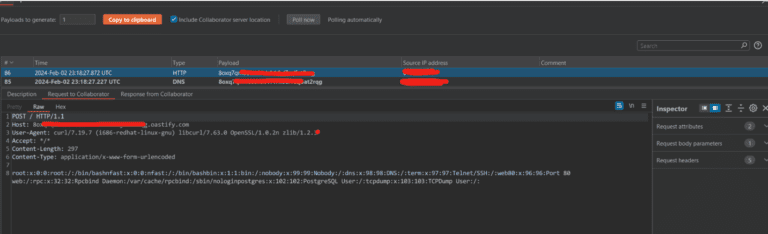
The PoC code not only exposes CVE-2024-21893 but also enables attackers to chain it with CVE-2024-21887, allowing for unauthenticated RCE

CVE-2024-23832 in the decentralized social networking platform Mastodon could be exploited to impersonate and take over any remote account

Wordfence has sounded the alarm, reporting over 1,400 blocked attacks targeting CVE-2023-6700 in the past 24 hours alone

Dubbed CVE-2024-1072, this flaw was a gaping hole rated 8.2 out of 10 on the severity scale. This high rating underscored the potential havoc

There is no publicly available PoC exploit for CVE-2024-21833. Evidence from underground forums indicates active exploitation of this flaw

Discovered by vigilant researchers at Trend Micro, the second vulnerability remedied in this update was the RCE POP chain flaw

CVE-2024-21626, a critical flaw in runc, allowed for a potential container escape, enabling unauthorized access to the host filesystem

Apple has recently confronted a formidable challenge: a zero-day vulnerability within their groundbreaking product, the Apple Vision Pro
Recently, a significant vulnerability in ModSecurity versions 3.0.0 to 3.0.11, identified as CVE-2024-1019, has surfaced.

If CVE-2024-21887 is used in conjunction with CVE-2023-46805, exploitation does not require authentication and enables a threat actor

These vulnerabilities, collectively identified under CVE IDs ranging from CVE-2024-22768 to CVE-2024-23842, have opened a backdoor

The GNU C Library (glibc), a fundamental component in major Linux distributions, has a critical vulnerability, CVE-2023-6246

CVE-2023-41474 can be a gateway to more sinister activities. Unauthenticated attacker could access configuration settings and internal info
three security vulnerabilities have been identified in its systems, two of which are of critical (CVE-2024-22860 and CVE-2024-22862) severity

CVE-2023-6200, with a considerable CVSS score of 7.5, this flaw exposes a critical race condition within the handling of ICMPv6 packets

The privilege escalation vulnerabilities CVE-2024-21326 (CVSS 9.6) and CVE-2024-21385 (CVSS 8.3) were rated as 'Important.'

The technical details and proof-of-concept (PoC) code targeting a critical CVE-2024-23897 vulnerability in Jenkins was published

Identified with a CVSS score of 8.3, CVE-2023-40547 exposes a remote code execution vulnerability within Shim.
The bug (tracked as CVE-2024-0402, CVSS 9.9) affects both GitLab Community Edition (CE) and Enterprise Edition (EE).