 Do Son
CVE-2023-35636 is a security vulnerability found in Microsoft Outlook, specifically in the calendar sharing function.
Vulnerability

Assigned a base score of 9.8 on the Common Vulnerability Scoring System, the CVE-2023-50643 vulnerability is classified as "Critical."

Further investigation revealed that this JSP code was from an open-source web shell known as the Godzilla Webshell.

A critical flaw, CVE-2024-22406 with a CVSS score of 9.3, poses a serious threat to businesses relying on this popular open-source platform

Siemens fixes two critical vulnerabilities (CVE-2023-51438 and CVE-2023-49621) in their SIMATIC IPC and SIMATIC NC 4100 products

tracked as CVE-2018-15133 (CVSS score: 8.1), the vulnerability has been described as a deserialization of untrusted data vulnerability

Citrix has sounded an alarm for its customers regarding two critical zero-day vulnerabilities, CVE-2023-6548 and CVE-2023-6549

Nassim Asrir has released the details, and a proof-of-concept (PoC) exploit for a high-severity vulnerability, CVE-2023-6546

The crux of the LeftoverLocals vulnerability (CVE-2023-4969) lies in the inadequate isolation of process memory in GPGPU platforms.
In a move that underscores the seriousness of the threat, Google confirmed that an exploit for CVE-2024-0519 is already prowling in the wild

Recently, two vulnerabilities were found in the Linux kernel that pose significant security threats: CVE-2024-0562 and CVE-2024-0565.

The recent discovery of CVE-2023-34063, a critical vulnerability with a CVSS score of 9.9, allows attackers to gain remote execution.

CVE-2023-22527 vulnerability, with a CVSS score of 10, signifies the highest level of severity in the realm of cybersecurity threats.

CVE-2023-4001 is an authentication bypass flaw in GRUB. GRUB is the gatekeeper of the booting process in many UEFI-based computers

CVE-2023-31029 and CVE-2023-31030 (CVSS 9.3): Both of these vulnerabilities exist in the NVIDIA DGX A100's baseboard management controller
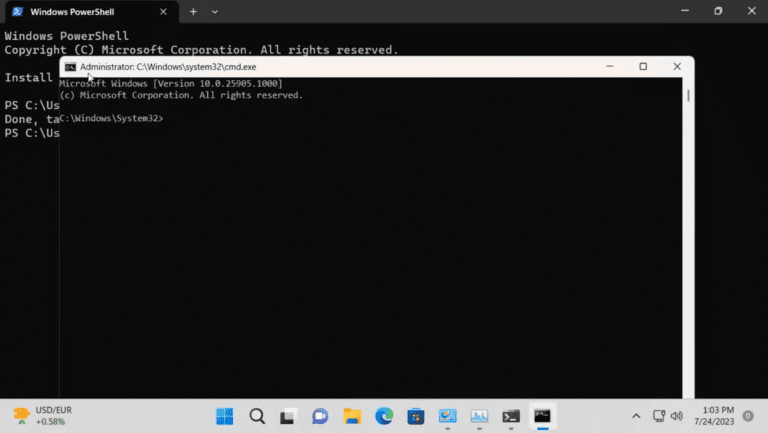
Adding to the severity, Michael Maltsev released a Proof-of-Concept (PoC) code, demonstrating the practical application of CVE-2023-36003
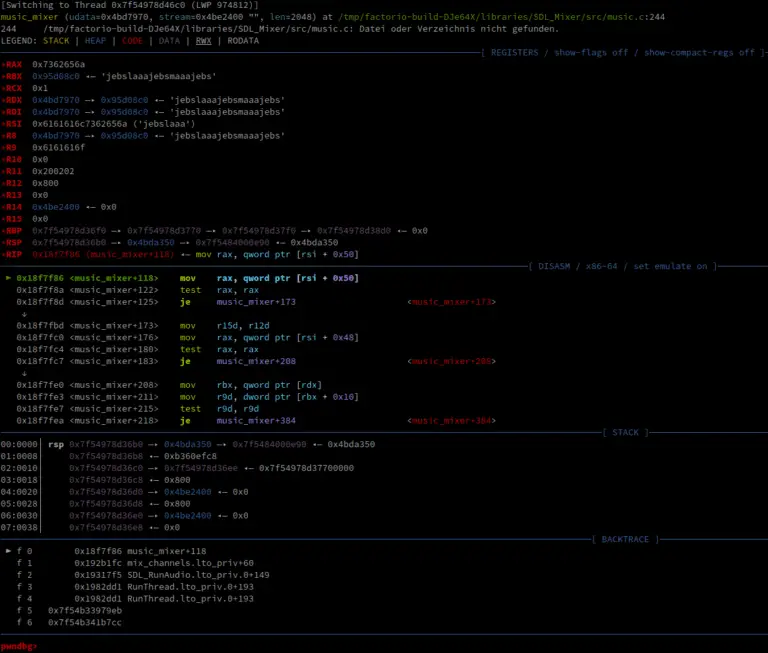
Valentin-Metz unveiled a critical buffer overflow vulnerability in Factorio. This flaw, lurking within the game's custom-engine C++ code

Details and proof-of-concept (PoC) exploit code have emerged about a now-patched security flaw, CVE-2024-20656, in Microsoft Visual Studio

CVE-2023-50290 is a security flaw that allows unauthorized read access to the host environment of Apache Solr instances
The Beijing Office of Justice said it had found a way to bypass AirDrop's encryption, allowing it to see the content and source of data transfers.
Linux Kernel has been hit by a significant security vulnerability, CVE-2023-6040, with a CVSS score of 7.8, impacting its netfilter component

CVE-2024-21611 (CVSS 7.5): A memory leak and eventually an rpd crash, CVE-2024-21591 (CVSS 9.8): J-web allows a preAuth Remote Code Execution