
 Do Son
Dubbed CVE-2023-6933, this security flaw has been classified with a critical severity rating of 9.8 out of 10
Vulnerability

Apache Superset has released fixes to fix a critical CVE-2023-49657 vulnerability that could lead to stored cross-site scripting attacks.
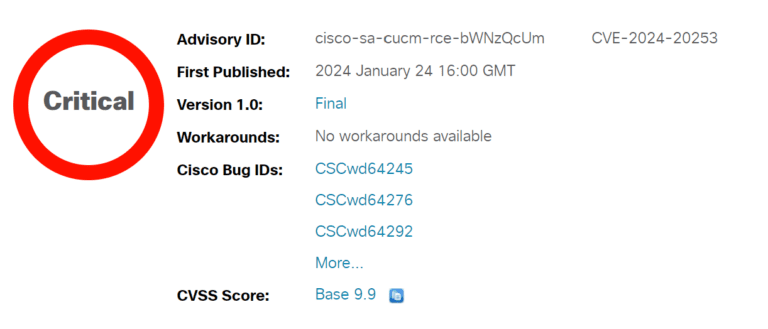
This security flaw tracked as CVE-2024-20253 (CVSS score of 9.9) affects the Cisco products in the default configuration

CVE-2024-23897, (CVSS 9.8), opens the door to arbitrary file reads through the CLI, potentially culminating in remote code execution (RCE).

The Danish Centre for Cyber Security (CFCS) is warning of increased ransomware activity, exploiting CVE-2023-20269, a vulnerability

In response to CVE-2024-0769, D-Link recommends retiring these products and replacing them with products that receive firmware

CVE-2024-0221 (CVSS 9.1) is a directory traversal vulnerability threatened to mar the integrity of the Photo Gallery plugin

A security researcher has published PoC code targeting a recently patched critical CVE-2024-0204 vulnerability in the Fortra GoAnywhere MFT.
PoC exploit code has been made available for critical flaws (CVE-2023-45866, CVE-2024-21306) impacting Bluetooth

CVE-2024-0204 (CVSS 9.8), this flaw is described as an authentication bypass vulnerability in Fortra's GoAnywhere MFT before version 7.4.1

CVE-2024-23222 lies within WebKit, and if exploited, could allow threat actors to execute arbitrary malicious code on unpatched devices.

CVE-2024-22233 (CVSS 7.5) allows an attacker to provide specially crafted HTTP requests that may cause a denial-of-service (DoS) condition

The discovery of CVE-2023-5716 is described as an arbitrary file-write vulnerability that strikes at the heart of its operational integrity.
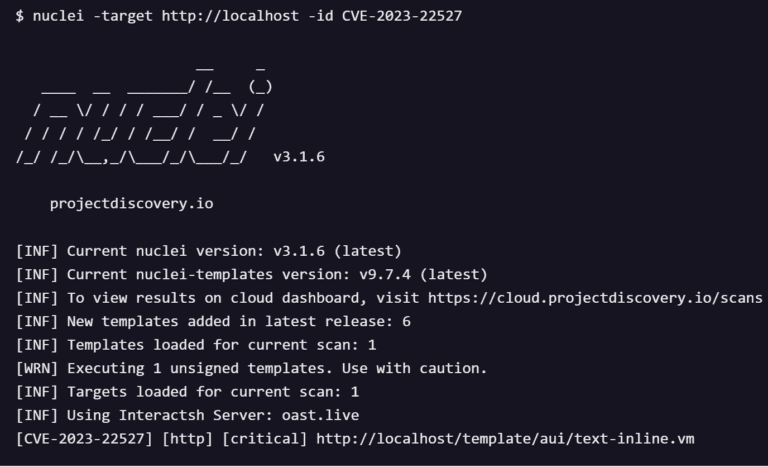
the researchers have created a nuclei template to detect CVE-2023-22527, CVSS score of 10.0, signifies maximum severity
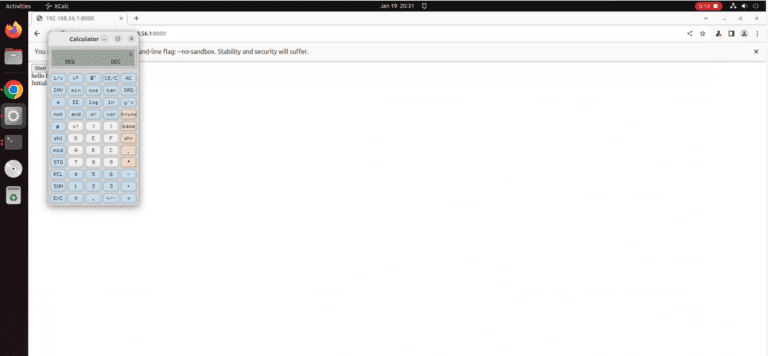
Poc releases a security flaw, CVE-2024-0517, in Google Chrome that could be exploited by threat actors to achieve remote code execution.

Security researchers have brought to light a significant flaw in pyLoad– CVE-2024-22416, a vulnerability with a high CVSS score of 9.6
Duarte Santos uncovered a critical vulnerability, CVE-2023-50447, that could potentially allow attackers to execute arbitrary code.

A critical vulnerability, identified as CVE-2023-40051 (CVSS 9.1), has been spotlighted within several iterations of the PASOE

Users employing these versions are unwittingly exposed to CVE-2024-21733 which could potentially leak sensitive information.

As of January 17, 2024, VMware has reported evidence that the CVE-2023-34048 RCE bug is currently being exploited in attacks
Slippy-Book, identified as CVE-2023-44451 for Xreader and CVE-2023-52076 for Atril, targets the very core of file parsing in Linux’s prominent document

A key discovery in Volexity's investigation was the GIFTEDVISITOR webshell. Over 1,700 compromised Ivanti Connect Secure VPN devices