
 Do Son
PoC code has been released for iOS and macOS vulnerability, CVE-2023-41974, that can be chained to take full control of a mobile device
Vulnerability

Both vulnerabilities, identified as CVE-2023-48419 and CVE-2023-6339, carry the maximum severity rating with a CVSSv3 score of 10.
The first vulnerability addressed by the patches is CVE-2023-48418, carrying the highest severity rating with a CVSSv3 score of 10
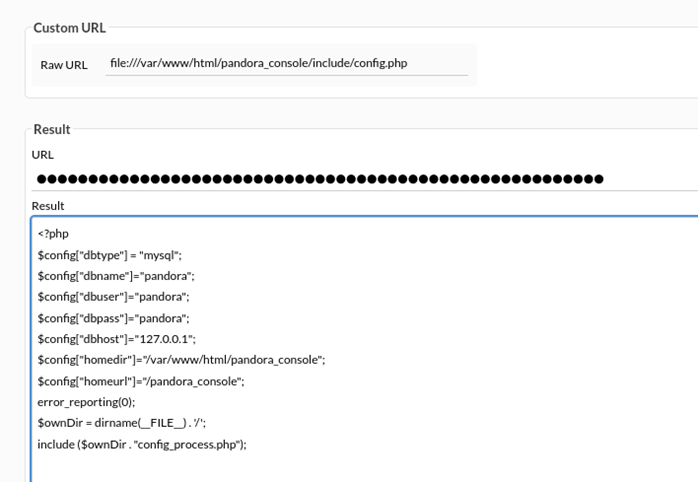
Classified as critical, CVE-2023-4677 allows attackers to execute arbitrary commands on all connected agents, leading to mass compromise.
The agency recently added two significant vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog

PoC code has been released for a zero-day iOS vulnerability (CVE-2023-32434) that can be chained to take full control of a mobile device.
CVE-2023-33025 (CVSS 9.8): This vulnerability, rooted in memory corruption during non-standard SDP bodies in VOLTE calls

Their research has refined the classic DLL Search Order Hijacking technique, leveraging executables in the trusted WinSxS folder of Windows OS

Deepin-Compressor, the default archive manager for the Deepin Linux OS, has been identified as having a path traversal flaw- CVE-2023-50255

PoC exploit code has been made available for a recently disclosed flaw, CVE-2023-50226 (CVSS 7.8), impacting Parallels Desktop

A recent discovery has cast a shadow over its robustness – the CVE-2023-7163 vulnerability, a critical flaw with a maximum CVSSv3 score of 10

A moderate severity flaw, this vulnerability lurked in the shadows of Apache OpenOffice and LibreOffice, where embedded content

CVE-2023-49299 security vulnerability allows an authenticated user to execute arbitrary, unsandboxed JavaScript on the server.

In the firmware versions v3.3 and earlier of the ioLogik E1200 Series, a menacing vulnerability was lurking, codenamed CVE-2023-5961

Recent revelations from Palo Alto Networks have cast a spotlight on two specific vulnerabilities within Google Kubernetes Engine

CVE-2023-41990 was addressed with improved handling of caches. This issue is fixed in tvOS 16.3, iOS 16.3 and iPadOS 16.3

This flaw, identified as CVE-2023-47565 and rated with a concerning CVSS v3 score of 8.0, reveals a significant gap in network security

CVE-2023-45741 allows an authenticated remote attacker to exploit the router by injecting arbitrary commands into the operating system

CVE-2023-51467 enables pre-authentication RCE, allowing attackers to bypass authentication mechanisms and directly perform SSRF attacks

Barracuda Networks has faced a formidable challenge with the discovery of two zero-day vulnerabilities, CVE-2023-7102 and CVE-2023-7101

In the dynamic realm of cybersecurity, the discovery of RetSpill marks a significant evolution in Linux kernel exploitation

CVE-2023-51443, with a CVSS score of 7.5, exposes FreeSWITCH to DoS attacks during the delicate handshake phase of the DTLS protocol