
 Do Son
IDEMIA recently issued an advisory that highlights critical vulnerabilities in its Access and Time Biometric Terminals.
Vulnerability

A PoC exploit for SharePoint Pre-Auth Code Injection RCE chain has been released for two vulnerabilities (CVE-2023-29357 & CVE-2023-24955)

CVE-2023-45849 is a RCE vulnerability with a CVSS score of 10.0, allowing unauthenticated attackers to commandeer systems as LocalSystem

CVE-2023-33107, an integer overflow in KGSL IOMMU SVM memory management can lead to memory corruption in the Graphics Linux kernel during IOCTL call

CVE-2023-35628 allows a remote, unauthenticated attacker to execute arbitrary code on the victim's system.
CVE-2023-47100 (CVSS score of 9.8) has been unearthed, sending ripples of concern through the developer community.

This vulnerability (CVE-2021-44228) in Log4j versions 2.0-beta9 to 2.15.0 allowed for remote code execution (RCE) attacks
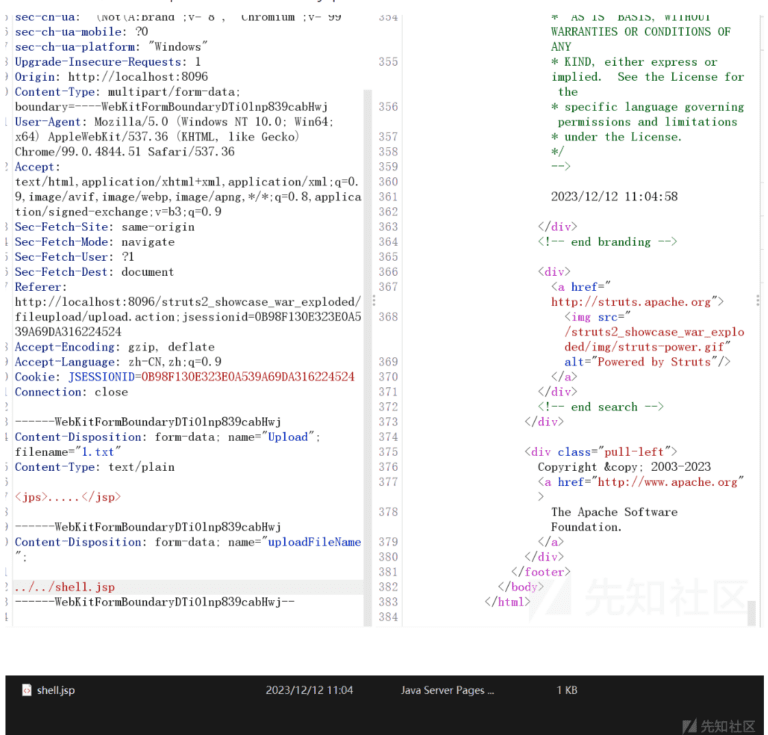
Brace yourselves, as the Proof of Concept (PoC) for the recently disclosed critical vulnerability, CVE-2023-50164, has been released
The first vulnerability, tagged as CVE-2023-46149 with a CVSS score of 9.8, exposes a terrifying reality: Authenticated Arbitrary File Upload
On the 12th of December 2023, SAP Security Patch Day published 15 new Security Notes alongside updates to 2 previously released notes

CVE-2023-6186 affects LibreOffice on all platforms and allows attackers to execute malicious scripts by crafting specially crafted hyperlinks

This vulnerability, known as CVE-2023-6553 (CVSS 9.8), impacts the Backup Migration plugin used by over 90,000 websites.

The recently sensationalized Bitcoin inscriptions have been reported as a cybersecurity vulnerability, designated as CVE-2023-50428
PoC exploit code is about to be published for the zero-day CVE-2023-36036 vulnerability that allows hackers to gain SYSTEM privileges

CVE-2023-6248 could allow attackers to remotely take control of fleets of vehicles, potentially leading to widespread chaos
CVE-2023-48777 allows accounts with edit post permissions, such as those with the Contributor role, to upload potentially malicious files

CVE-2023-35618 could lead to browser sandbox escape, allowing attackers to host or use compromised websites to exploit the vulnerability

This vulnerability cataloged as CVE-2023-49897 with a CVSS v3 score of 8.0, allows authenticated attackers to execute OS commands remotely

Apache Struts is facing a critical vulnerability (CVE-2023-50164) that can allow attackers to execute arbitrary code remotely.

CVE-2023-6448 allows unauthenticated attackers with network access to take complete control of the PLC and manipulate critical infrastructure functions

In the intricate web of modern computing, a new threat has emerged, casting a shadow over the...

While WordPress Core currently does not have any known object injection vulnerabilities, they are rampant in other plugins and themes.