
 Do Son
SLAM emerges from the intersection of hardware features intended for memory efficiency and the notorious Spectre vulnerabilities
Vulnerability

In the dynamic world of machine learning (ML), where innovation and efficiency are paramount, a new challenge...
A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22523 (CVSS score of 9.8), has been discovered in Assets Discovery

A critical Remote Code Execution (RCE) vulnerability, tracked as CVE-2023-22522, has been discovered in Confluence Data Center and Server

CVE-2023-43121 allows unauthenticated users to read root files, thereby exposing password hashes for the device
CVE-2023-33063 vulnerability arises from memory corruption in DSP Services during a remote call from the High-Level Operating System (HLOS)

Identified as CVE-2023-26360, this flaw has been exploited by threat actors for initial access to government servers, as confirmed by CISA
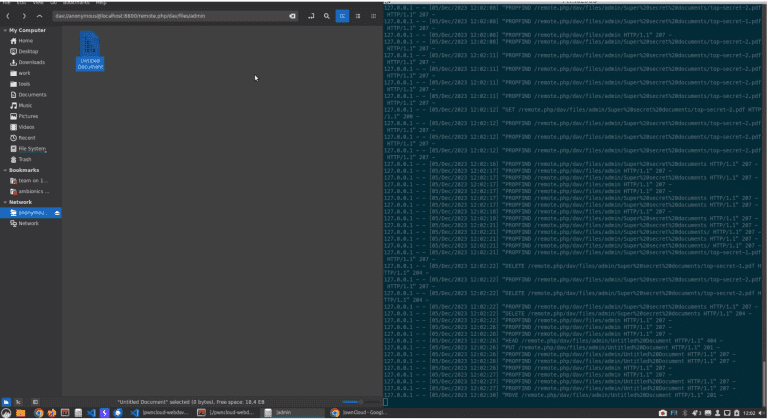
CVE-2023-49105 affecting ownCloud versions 10.6.0 to 10.13.0 has been made public, and a PoC exploit code is readily available
CVE-2023-6269 (CVSS: 10): Unpatched Vulnerability Leaves Atos Unify OpenScape at Risk of Root Access
CVE-2023-6269 (CVSS: 10): Unpatched Vulnerability Leaves Atos Unify OpenScape at Risk of Root Access
Rated with a CVSS3.1 Base score of 10 (critical), the CVE-2023-6269 vulnerability underscores the severity and potential impact

By exploiting the CVE-2023-49070 vulnerability, an attacker can execute arbitrary code on the affected Apache OFBiz server

Protect your business from the powerful cyber threats of state-sponsored Russian group, Forest Blizzard. As Microsoft tracks their exploits, uncover the group's tactics & targets to secure your data.

RCE Attack threats can be avoided with CVE-2023-49093. Upgrading to a secure version of HtmlUnit with XSLT FEATURE_SECURE_PROCESSING is the answer.

Revealed: 8 Aleos security vulnerabilities, including the Remote Code Execution (CVE-2023-40465) on versions prior to 4.17. Read the blog to find out more.
Designated as CVE-2023-6316, the security vulnerability received a CVSS score of 9.8, categorizing it as critical.

Papercut privilege escalation security vulnerability still doesn't seem to be fixed on the current version (23.0.3)
CVE-2023-40626 stems from an issue in the language file parsing process, which could be manipulated to disclose environment variables.
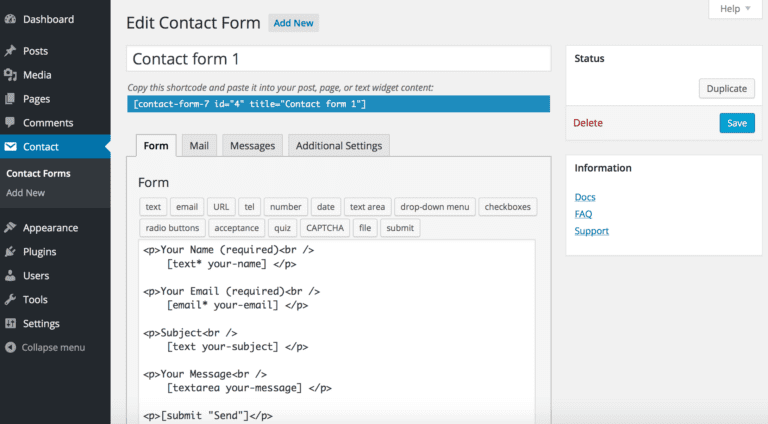
Contact Form 7, a popular WordPress plugin with over 5 million installations, has been found to harbor a vulnerability (CVE-2023-6449)

A critical risk has surfaced within Google Workspace's Domain-Wide Delegation feature, as revealed by Unit 42 researchers at PaloAlto Networks

LogoFAIL vulnerabilities are not vendor-specific and impact devices and chips from a wide range of manufacturers, affecting UEFI firmware
This issue stemmed from a susceptibility to cross-site scripting (XSS) via shortcodes (CVE-2023-48321, CVSS: 6.5).

CVE-2023-42916: An out-of-bounds read vulnerability could allow attackers to read sensitive information from the affected device's memory

The CVE-2023-4473 vulnerability allows an unauthenticated attacker to execute OS commands with a specially crafted URL.