
 Do Son
A new attack technique named SMTP Smuggling has emerged, threatening the integrity of email communication worldwide.
Vulnerability
CVE-2023-51713 exposes a dangerous out-of-bounds buffer read issue in ProFTPD's make_ftp_cmd. This flaw affects version before 1.3.8a

CVE-2023-51385 security vulnerability, with a CVSS score of 9.8, threatened the very core of its secure channel operations.

Tracked as CVE-2023-50254 and scoring a concerning 8.2 on the CVSS scale, this is classified as a file overwrite vulnerability.

Researchers issued CVE-2023-42465 for SUDO for this vulnerability. This flaw classified as critical has been found in sudo up to 1.9.14.

The X.Org Server and XWayland have released updates to address two significant vulnerabilities: CVE-2023-6377 and CVE-2023-6478

Proof-of-concept (PoC) exploit code has been published for a Windows kernel vulnerability tracked as CVE-2023-36424.

One of the most alarming aspects of CVE-2023-7024 is that it had been actively exploited in the wild before its discovery.

Identified as CVE-2023-48738 and rated 9.3 on the CVSS scale, this vulnerability was a ticking time bomb in the Porto theme's code.

A staggering 26,447 vulnerabilities were disclosed in 2023, surpassing 2022's total by over 1,500 CVEs.

The discovery of CVE-2023-50917 serves as a stark reminder of the importance of cybersecurity in the realm of smart home automation
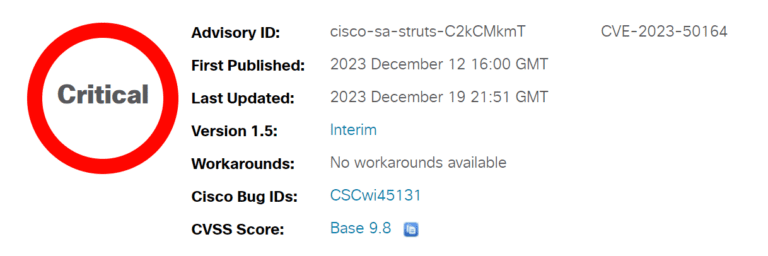
In light of a CVE-2023-50164 vulnerability discovered in Apache Struts, Cisco Systems has elucidated the impact on its products.

Unauthenticated attackers can exploit the CVE-2023-6750 (CVSS 9.8) flaw to download database backups made with the plugin.

Tagged as CVE-2023-43826 (CVSS score of 7.5), this security flaw in Apache Guacamole represents a significant threat

CVE-2023-49734 vulnerability allows a lower-privileged user, or 'Gamma user,' to gain undue control over chart permissions.
CVE-2023-6817, poses a severe threat with a CVSS score of 7.8, categorizing it as a high-severity issue, also PoC exploit published.

Rooted in a flaw within the "file upload logic" of AEM Forms on JEE versions 6.5.19.0 and earlier, this flaw paves the way for unauthorized path traversal

AnyDesk is installed using Netcat, allowing attackers to control the system's screen remotely, bypassing security products

CVE-2023-48795 (Terrapin Attack) revolves around the manipulation of sequence numbers during the SSH handshake process.

The complete PoC exploit source code for CVE-2023-22524 is available on GitHub, providing a detailed blueprint of this vulnerability

CVE-2023-6553 flaw's discovery and the subsequent publication of a technical write-up, coupled with the release of a PoC exploit code

Identified as CVE-2023-49954, this security loophole is an SQL Injection flaw found in 3CX CRM Integration.