
 Do Son
By sending a specially crafted request, an attacker could exploit CVE-2024-0252 to execute arbitrary code on the system.
Vulnerability

GitLab has taken decisive steps to fortify its defenses against two critical flaws - CVE-2023-7028 (CVSS 10) & CVE-2023-5356 (CVSS 9.6)
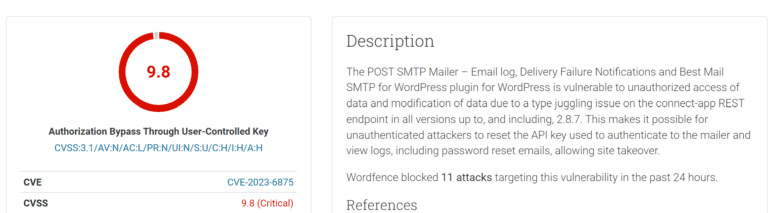
CVE-2023-6875, with a CVSS score of 9.8, exists in the Post SMTP landscape, exploiting a type juggling issue in the connect-app REST endpoint

Identified as CVE-2024-20272, this vulnerability allows unauthenticated attackers could gain root privileges on unpatched devices.

Ivanti has revealed two critical zero-day vulnerabilities (CVE-2024-21887, CVE-2023-46805) in its Connect Secure and Policy Secure products
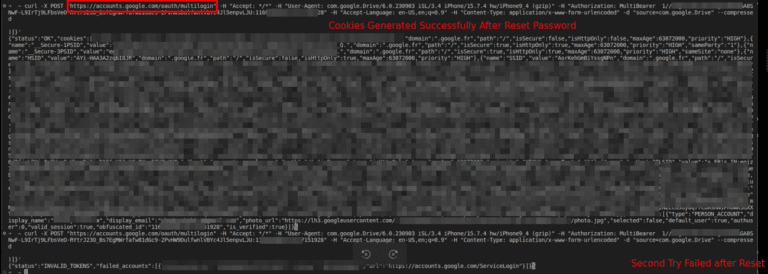
Cybercriminals can access users' Google accounts through a cookie vulnerability without knowing the password.
CVE-2023-49647 could be exploited to gain elevated rights, posing a serious threat to the confidentiality and integrity of Zoom sessions and user data
Rated 8.1 on the CVSS, CVE-2023-41056 is a serious threat that underscores the fragility of even the most secure systems
CVE-2024-20674 in Windows Kerberos could enable an unauthenticated attacker to execute a machine-in-the-middle (MitM) attack

This vulnerability, designated as CVE-2023-47211, carries a high-severity rating of 9.1 on the Common Vulnerability Scoring System scale
CVE-2023-51409 was so critical that it received a Common Vulnerability Scoring System score of 10, indicating the highest level of severity.

CVE-2024-0193 is capable of being exploited by local adversaries to escalate privileges and execute arbitrary code

The report is a comprehensive examination of the vulnerabilities inherent in AI and machine learning (ML) systems.
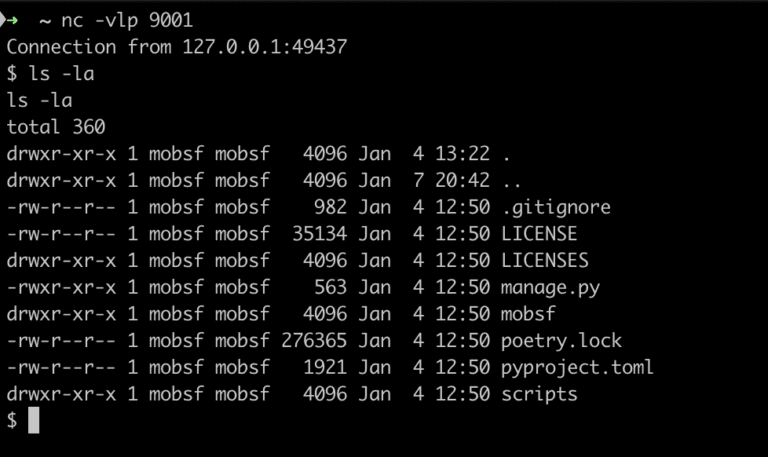
The vulnerability, identified as CVE-2024-21633 (CVSS 7.8), exists in the apktool, a component of the MobSF.

QiAnXin Threat Intelligence Center's detailed analysis linked the binary involved in this operation to a North Korean APT
The technical details and a PoC exploit of CVE-2023-39296 were unveiled by an independent security researcher, DCS
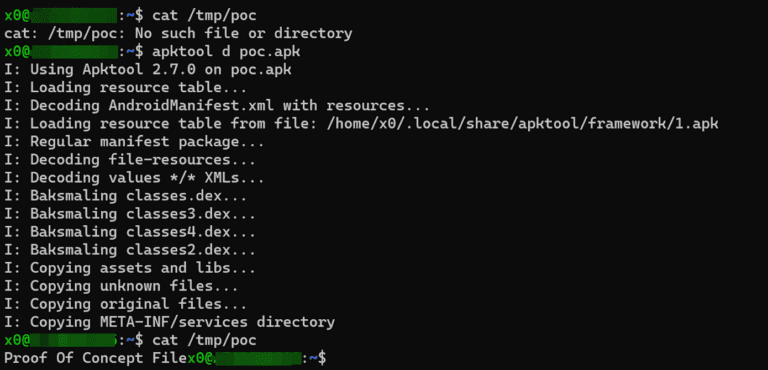
The CVE-2024-21633 (CVSS 7.8) vulnerability allows an attacker to write or overwrite any file to which the user has access.

CVE-2023-39475 & CVE-2023-39476 allow remote attackers to execute arbitrary code on affected systems, bypassing any need for authentication

Another critical vulnerability, identified as 'GHSA-76cc-p55w-63g3', was found in Teleport's version 14 access list feature
The vulnerability, tagged as CVE-2023-39336 (CVSS 9.6), posed a significant risk in the form of a remote code execution (RCE) flaw

Tagged with an 'important' severity rating, CVE-2023-51784 is a Remote Code Execution (RCE) vulnerability in Apache InLong Manager

With a CVSS score of 8.6, this vulnerability exposes a chink in the armor of many websites, leaving them vulnerable to unauthenticated attacks