Skip to content
September 24, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Android
  • Google data shows that Android 8.x is on 12.1% of devices
  • Android

Google data shows that Android 8.x is on 12.1% of devices

Do Son July 25, 2018 1 minute read
Android 8.x
Add Daily CyberSecurity as a preferred source on Google

Under normal circumstances, Google will release the share of each version of Android every month, but the unexpected situation is that Google did not release statistics last month.

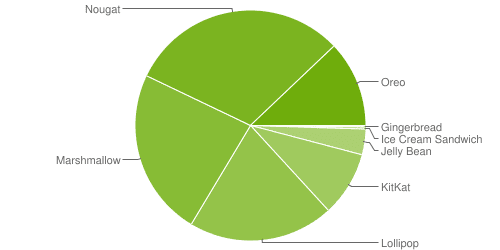
Now the statistics of Android system have been released this month. From the statistics, the market share of Android Oreo has begun to increase substantially.

The launch of the Android Oreo version will be full of the next birthday until next month, and the growth of the Riorio version in the past two months is also the biggest winner.

But even so, Android Oreo’s overall market share is only about 12%, which is low from 23.5% or even 30% of Marshmallow and Nougat.

For Google, the fragmentation of the Android ecosystem has always been a headache. If there are no surprises, Android 9 will be released next month.

So are your friends using the latest version of Android now? It is estimated that the manufacturer has abandoned most of the devices and there is no opportunity to upgrade the newest version.

The following statistics do not include devices without the Google App Store:

Image: Android

Related coverage

  • Aluminum OS Unleashed: Google’s Secret Roadmap to Sunset ChromeOS for an Android Desktop
  • Android P will silently crash app instead of showing popup dialog
  • Android P will allow to use your phone as a Bluetooth Keyboard or Mouse
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Android 8.x

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2026-48842CVSS 8.1
    Roundcube Webmail 1.6.x before 1.6.16 and 1.7.x before 1.7.1 has Pre-authentication SQL injection in the virtuser_query plugin via...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-87902
    Unauthenticated path traversal in page-template resolution leading to conditional RCE An unauthenticated attacker can make get_page_template() page-template resolution...
    Admin intel📅 Updated: Sep 23, 2026
  • CVE-2026-94127CVSS 9.8
    When a BIG-IP APM access policy and an OAuth profile is configured on a virtual server, specific malicious...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-85102CVSS 9.8
    Improper certificate trust validation during VPN negotiation in Check Point Quantum Security Gateway may allow an unauthenticated remote...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93616CVSS 9.8
    A directory traversal and file upload vulnerability allows an unauthenticated attacker to upload and execute arbitrary scripts on...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-93952CVSS 10.0
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intelCISA KEV📅 Added to KEV: Sep 22, 2026📅 Updated: Sep 22, 2026
  • CVE-2026-32996CVSS 7.3
    A vulnerability in Veeam Agent for Microsoft Windows allows for Local Privilege Escalation.
    Admin intel📅 Updated: Sep 22, 2026
  • CVE-2026-7273CVSS 8.8
    A stack-based buffer overflow vulnerability in the CGI program of Zyxel GS1900-48HPv2 firmware versions through 2.90(ABTQ.1)C0 could allow a...
    CISA KEV📅 Added to KEV: Sep 21, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-61741CVSS 9.3
    http4s-scala-xml provides `EntityDecoder[F, scala.xml.Elem]` instances that parse XML message bodies. Prior to versions 0.24.1 and 1.0.0-M39, these decoders...
    📅 Updated: Sep 24, 2026
  • CVE-2026-61732CVSS 10.0
    Decepticon is an autonomous hacking agent for red teams. Versions prior to 1.1.17 wrap web crawl results —...
    📅 Updated: Sep 24, 2026
  • CVE-2026-69843CVSS 10.0
    No description available
    📅 Updated: Sep 24, 2026
  • CVE-2026-62874CVSS 10.0
    No description available
    📅 Updated: Sep 24, 2026
  • CVE-2026-79766CVSS 9.1
    Termix is a web-based server management platform with SSH terminal, tunneling, and file editing capabilities. From 2.4.1 until...
    📅 Updated: Sep 24, 2026
  • CVE-2026-66792CVSS 9.9
    A flaw was found in the multicloud-operators-subscription component. This vulnerability allows a user on a managed cluster to...
    📅 Updated: Sep 24, 2026
  • CVE-2026-69399CVSS 10.0
    No description available
    📅 Updated: Sep 24, 2026
  • CVE-2026-58822CVSS 9.8
    In multiple functions of ftsmooth.c, there is a possible memory safety issue due to improper casting. This could...
    📅 Updated: Sep 24, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.