Skip to content
November 8, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Technology
  • KDE releases the first Plasma Mobile ISO Image
  • Technology

KDE releases the first Plasma Mobile ISO Image

Do Son January 27, 2018 2 minutes read
Plasma Mobile

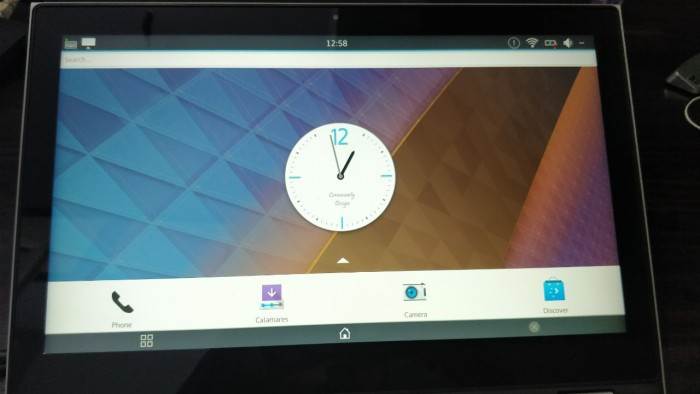
Following last week’s commitment to bring the full-featured Plasma Mobile user interface to mobile devices such as mobile phones and tablets by the end of 2018, the KDE team today shared the latest ISO image in the community and invited early adopters in the community to test.

KDE said that improving and improving Plasma Mobile cannot be separated from the community support, only more users to test, submit more BUG feedback and opinion system to further development. The KDE team also admits that the final release of Plasma Mobile may be postponed, including the forthcoming launch of the Librem 5 Linux handset from Purism in the first quarter of 2019.

The first Plasma Mobile ISO image released today, users can use on real devices or virtual machines like QEMU/KVM and Oracle VirtualBox. After successfully installing Plasma Mobile, the KDE team will invite you to test things like trying to add plug-ins to the desktop, reading comics in the Peruse app, testing the Kaidan XMPP client, and downloading and installing apps from the Plasma Discover software center.

Users can submit feedback to plasma-mobile@kde.org or submit to #plasma IRC at Freenode. At present, Plasma Mobile is still in the Alpha development stage, so some features may not work properly.

Download

Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Windows 10 End-of-Life: Microsoft Extends 365 Support Until 2028 with ESU Program
  • Firefox Pilots AI Search: Perplexity AI Integration Challenges Google’s Dominance
  • EU Classifies ChatGPT as Search Engine
  • 42.5 ExaFLOPS: Google Launches Ironwood TPU to Power Next-Gen Agentic AI
  • OKX Launches Compliant Crypto Services in the US After Regulatory Clearance
  • iPhone 17: The Final Goodbye to the Physical SIM Card?
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our tech and OS security coverage helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Plasma Mobile

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-123158CVSS 8.1
    sshd in OpenSSH before 10.6p2 on Linux, when musl libc is used without PAM, lacks a workaround for...
    Admin intel📅 Updated: Nov 6, 2026
  • CVE-2026-19868CVSS 7.5
    An authentication enforcement vulnerability in SonicOS SSLVPN service may allow a user with valid credentials for an alternate...
    CISA KEV📅 Added to KEV: Nov 6, 2026
  • CVE-2026-120422CVSS 8.9
    Sogou Input Method for Windows contains a vulnerability in the configuration retrieval mechanism of its SGTool.exe component. The...
    Admin intel📅 Updated: Nov 5, 2026
  • CVE-2026-102895CVSS 9.8
    GPUStack is an open-source GPU cluster manager for AI model serving and GPU instance provisioning. Prior to 2.2.0,...
    Watchtower Verified📅 Updated: Nov 5, 2026
  • CVE-2026-115732CVSS 9.0
    Incorrect authorization in the certificate-name matching of trapperkeeper-authorization, as used by Puppet Server, in the affected products, allows...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-18535CVSS 9.6
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 are vulnerable to a Regular Expression Denial of...
    📅 Updated: Nov 8, 2026
  • CVE-2026-17409CVSS 9.4
    IBM API Connect 10.0.8.0 through 10.0.8.12 and 12.1.0.0 through 12.1.1.2 could allow a remote attacker to execute unauthorized...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123614CVSS 9.3
    imgproxy from 4.0.0 before 4.0.16 contains an integer overflow in the ICO loader that allows remote attackers to...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123550CVSS 9.3
    OpenAM before 16.1.4 contains an authentication bypass vulnerability in its SAML v2.0 service provider that accepts unsigned assertions...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123551CVSS 10.0
    OpenAM from 14.0.0 before 16.1.4 contains an information disclosure vulnerability that allows unauthenticated attackers to read live session...
    📅 Updated: Nov 8, 2026
  • CVE-2026-123549CVSS 9.3
    OpenAM before 16.1.4 fails to enforce the Valid Creation Attributes list during self-registration, allowing anonymous attackers to set...
    📅 Updated: Nov 8, 2026
  • CVE-2025-57085CVSS 9.8
    Tenda W30E V16.01.0.19 (5037) was discovered to contain a stack overflow in the v17 parameter in the UploadCfg...
    📅 Updated: Nov 8, 2026
  • CVE-2025-59359CVSS 9.8
    The cleanTcs mutation in Chaos Controller Manager is vulnerable to OS command injection. In conjunction with CVE-2025-59358, this...
    📅 Updated: Nov 8, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.