Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
The Silicon Harvest: Google Seeks Premium Codebases for AI Refinement Google licenses app code Gemini API Prepaid Billing Gemini macOS Desktop Intelligence Gemini API Tier 2 upgrade Google Workspace CLI AI Google Gemini Import AI Chats Google AI Plus subscription 2026, Gemini 3 Pro vs AI Pro cost Apple, Google Gemini, Siri, Apple Intelligence, iOS 26, The Information, Fine-tuning, Private Cloud Compute, AI Partnership, Tech News 2026 Gemini Assistant transition 2026, Google Assistant sunset delay Nano Banana Pro AI Image Text Gemini Deep Research, Workspace Integration Gemini Canvas, presentation generation
  • Technology

The Silicon Harvest: Google Seeks Premium Codebases for AI Refinement

Do Son June 3, 2026 0

Google licenses app code from Play Store developers to train Gemini AI models and compete with GitHub Copilot and Claude Code. Learn more.

Critical Apache Solr Security Flaw Exposes Clusters to Remote Takeover Apache Solr default credentials CVE-2026-44825 workaround CVE-2025-24814 & CVE-2025-24814
  • Vulnerability Report

Critical Apache Solr Security Flaw Exposes Clusters to Remote Takeover

Do Son June 3, 2026 0

A high-severity Apache Solr default credentials vulnerability is exposed. Learn the critical CVE-2026-44825 workaround to secure your clusters.

Critical GitHub Token Stealing Bug Exploits Web-Based Code Editors GitHub token stealing bug VSCode webview security model
  • Vulnerability Report

Critical GitHub Token Stealing Bug Exploits Web-Based Code Editors

Do Son June 3, 2026 0

A critical GitHub token stealing bug targets github.dev web spaces. Learn how it exploits the VSCode webview security model to hijack private repositories.
InHand Router Flaws: Command Injection Patches Released Yarbo robot vulnerability hard-coded MQTT credentials, CVE-2026-10557, CVE-2026-7368 command injection vulnerabilities InHand router flaws
  • Vulnerability Report

InHand Router Flaws: Command Injection Patches Released

Do Son June 3, 2026 0

Severe InHand router flaws expose industrial networks to command injection vulnerabilities. Update your industrial firmware immediately to patch these bugs.

Actively Exploited Vulnerabilities Added to CISA KEV Catalog actively exploited vulnerabilities Android privilege escalation flaw DELMIA Apriso RCE, CISA KEV Exploitation ServiceNow Vulnerabilities
  • Vulnerability Report

Actively Exploited Vulnerabilities Added to CISA KEV Catalog

Do Son June 3, 2026 0

CISA added new actively exploited vulnerabilities to its catalog. Learn how the Android privilege escalation flaw impacts corporate environments.

Critical Security Flaw Exposes Industrial IoT Converters USR-W610 vulnerability hardcoded administrative credentials
  • Vulnerability Report

Critical Security Flaw Exposes Industrial IoT Converters

Do Son June 3, 2026 0

A critical USR-W610 vulnerability exposes hardcoded administrative credentials. Learn how to secure your PUSR IoT converters from exploitation.

Critical Langflow RCE Vulnerability Exposes AI Workflows Langflow RCE vulnerability Shareable Playground security flaw
  • Vulnerability Report

Critical Langflow RCE Vulnerability Exposes AI Workflows

Do Son June 3, 2026 0

A critical Langflow RCE vulnerability impacts the Shareable Playground feature. Learn about the new security patches available.

Laravel CRLF Injection Vulnerability Threatens Web Applications Laravel CRLF injection vulnerability CVE-2026-48019 patch CVE-2024-13918 and CVE-2024-13919
  • Vulnerability Report

Laravel CRLF Injection Vulnerability Threatens Web Applications

Do Son June 3, 2026 0

A severe Laravel CRLF injection vulnerability exposes web apps to mail relay abuse. Apply the latest CVE-2026-48019 patch to protect your infrastructure.

Critical XCharge C6 Vulnerabilities Expose Electric Vehicle Chargers XCharge C6 vulnerabilities EV charger security flaws GNU libtasn1 Vulnerability CVE-2025-13151 Credit Card Skimmer Malware CVE-2024-13892
  • Vulnerability Report

Critical XCharge C6 Vulnerabilities Expose Electric Vehicle Chargers

Do Son June 2, 2026 0

Critical XCharge C6 vulnerabilities expose EV chargers to exploitation. Learn how recent updates address these EV charger security flaws immediately.
Critical ActiveMQ Security Flaws Threaten Enterprise Message Brokers ActiveMQ security flaws Jolokia web console exploit ActiveMQ RCE Jolokia Spring Vulnerability ActiveMQ MQTT Vulnerability CVE-2025-66168 Apache Artemis Vulnerability CVE-2026-27446
  • Vulnerability Report

Critical ActiveMQ Security Flaws Threaten Enterprise Message Brokers

Do Son June 2, 2026 0

Fix critical ActiveMQ security flaws today. Avoid a dangerous Jolokia web console exploit by upgrading your message broker immediately.

Halo Security Honored with 2026 MSP Today Product of the Year Award halo-security-msp-today-2026_1780097763dObw3SFnsr
  • Press Release

Halo Security Honored with 2026 MSP Today Product of the Year Award

cybernewswire June 2, 2026 0
Miami Beach, FL, USA, 2nd June 2026, CyberNewswire
Read More Read more about Halo Security Honored with 2026 MSP Today Product of the Year Award
Kirki Plugin Vulnerability: 150K WordPress Sites Face Critical 9.8 CVSS Privilege Escalation in the Wild Kirki plugin vulnerability WordPress account takeover
  • Vulnerability Report

Kirki Plugin Vulnerability: 150K WordPress Sites Face Critical 9.8 CVSS Privilege Escalation in the Wild

Do Son June 2, 2026 0

An active Kirki plugin vulnerability allows a critical WordPress account takeover. Learn how this 9.8 CVSS flaw impacts 150,000 active websites.

BlackToad Threat Actors Deploy Stealthy Phishing Lures Remcos RAT phishing campaign Network blackout technique
  • Cybercriminals

BlackToad Threat Actors Deploy Stealthy Phishing Lures

Do Son June 2, 2026 0

A novel Remcos RAT phishing campaign utilizes a network blackout technique to evade defense systems. Learn how to protect your enterprise network.
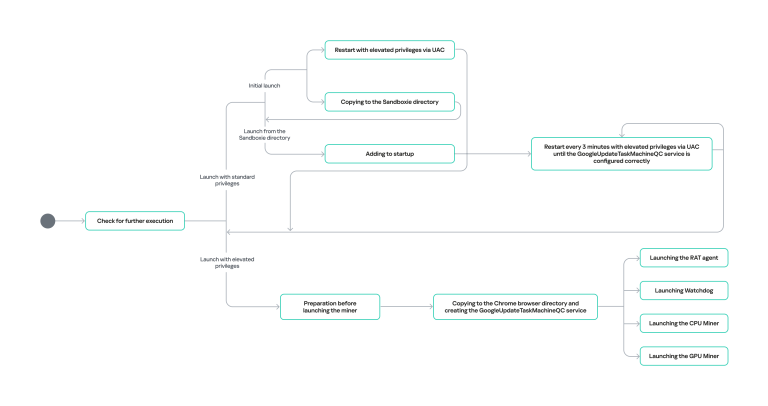
Sophisticated SilentCryptoMiner Variant Delivered via Fake Plugin Overlays Miner-and-RAT
  • Malware

Sophisticated SilentCryptoMiner Variant Delivered via Fake Plugin Overlays

Do Son June 2, 2026 0

A stealthy SilentCryptoMiner variant uses a fake plugin update to infect systems. Protect your enterprise from this advanced cryptocurrency miner.

Fake RVTools Installer Deploys Modular Python RAT Fake RVTools installer Modular Python RAT
  • Malware

Fake RVTools Installer Deploys Modular Python RAT

Do Son June 2, 2026 0

A fake RVTools installer campaign distributes a modular Python RAT. Learn how this malware uses signed certificates to evade security controls.

Grandoreiro Banking Trojan Evades Defense via Lookalike Software TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Grandoreiro Banking Trojan Evades Defense via Lookalike Software

Do Son June 2, 2026 0

The dangerous Grandoreiro banking trojan returns. Discover how it utilizes an advanced DLL side loading technique to bypass corporate defenses.

The Shai-Hulud Infiltration: Red Hat Exploited in Sovereign Supply Chain Breach Red Hat NPM attack
  • Malware

The Shai-Hulud Infiltration: Red Hat Exploited in Sovereign Supply Chain Breach

Do Son June 2, 2026 0

Analyze the recent Red Hat NPM attack. Learn how hackers bypassed trusted publishing via GitHub Actions to deploy the Mini Shai-Hulud worm.

High-Severity Ivanti ITSM Vulnerability Exposes IT Systems Ivanti EPMM security updates Ivanti ITSM vulnerability authenticated privilege escalation Ivanti Xtraction vulnerability CVE-2026-8043 Ivanti EPM RCE, SQL Injection Ivanti EPM, remote code execution CVE-2024-50330 - CVE-2025-0282 and CVE-2025-0283
  • Vulnerability Report

High-Severity Ivanti ITSM Vulnerability Exposes IT Systems

Do Son June 2, 2026 0

A high-severity Ivanti ITSM vulnerability is fixed. Learn how to address this authenticated privilege escalation flaw on cloud and on-premises setups.
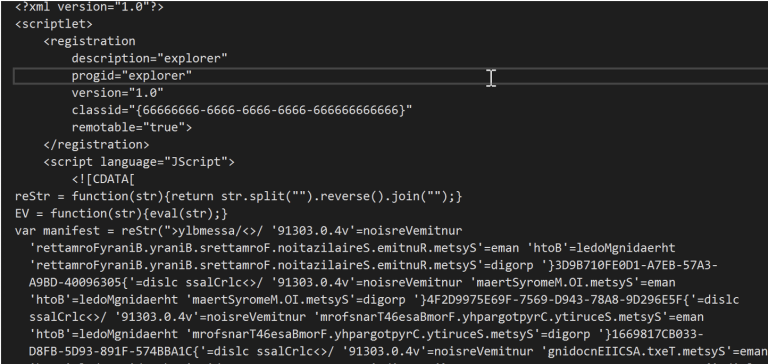
Twill Typhoon RAT Campaign Uses DLL Side Loading to Target APJ Networks Twill Typhoon RAT campaign DLL side loading tradecraft
  • Cyber Security
  • Malware

Twill Typhoon RAT Campaign Uses DLL Side Loading to Target APJ Networks

Do Son June 2, 2026 0

A stealthy Twill Typhoon RAT campaign targets APJ organizations. Discover how this threat exploits DLL side loading tradecraft to evade security.

Apache Fesod SSRF Vulnerability Exposes Internal Networks Apache Fesod SSRF vulnerability CVE-2026-49328 patch
  • Vulnerability Report

Apache Fesod SSRF Vulnerability Exposes Internal Networks

Do Son June 2, 2026 0

A critical Apache Fesod SSRF vulnerability has been found. Learn about the CVE-2026-49328 patch released to protect internal network resources.

The Longevity Gambit: AMD Extends AM5 and Reshapes the Silicon Landscape AMD AM5 platform support AMD Embedded Processors Vulnerabilities
  • Technology

The Longevity Gambit: AMD Extends AM5 and Reshapes the Silicon Landscape

Do Son June 2, 2026 0

Discover the latest AMD AM5 platform support updates. Learn how Team Red enables cost-effective desktop upgrades for future Ryzen processors.

Critical KMW CCTV Vulnerability Exposes Live Surveillance Feeds KMW CCTV vulnerability unauthenticated password reset Xiongmai IP Camera Vulnerability CVE-2025-65856 CVE-2024-8956 (CVSS 9.1): PTZOptics Cameras
  • Vulnerability Report

Critical KMW CCTV Vulnerability Exposes Live Surveillance Feeds

Do Son June 2, 2026 0

A critical KMW CCTV vulnerability allows an unauthenticated password reset. Secure your surveillance cameras and patch your firmware immediately.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 8.7
    WooThemes Diarise through 1.5.9 contains a file read vulnerability that allows unauthenticated attackers to read arbitrary files through...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 5.1
    WPML Multilingual CMS plugin for WordPress before 4.6.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-121609CVSS 10.0
    A vulnerability was identified in Qihoo 360 Whole Home Router M5 4.0.17.1566. This issue affects the function Home...
    📅 Updated: Nov 4, 2026
  • CVE-2026-51912CVSS 9.8
    OpenBMB XAgent v1.0.0 contains directory traversal vulnerability in main-upload_file-the-preserved-live-upload-file-witness-directly-reaches (ToolServer/ToolServerNode/main.py:46).
    📅 Updated: Nov 4, 2026
  • CVE-2026-107056CVSS 9.1
    Insecure permissions in the io.file.importer.ImportActivity component of OpenTracks versionCode 6751 allows unauthorized attackers to inject crafted tracking data...
    📅 Updated: Nov 4, 2026
  • CVE-2026-107050CVSS 9.8
    An issue in libretro RetroArch v1.22.2 allows attackers to force another user into loading attacker-supplied code in their...
    📅 Updated: Nov 4, 2026
  • CVE-2026-107040CVSS 9.1
    Insecure permissions in MBasov OMN-Go versionCode 26080824 allows unauthorized attackers to invoke an exported component, leading to arbitrary...
    📅 Updated: Nov 4, 2026
  • CVE-2026-107045CVSS 9.1
    Insecure permissions in the CitrineContentProvider component of Citrine v3.1.0 (versionCode 62) allows unauthorized attackers to arbitrarily read another's...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121607CVSS 10.0
    A vulnerability was found in Qihoo 360 D603-2, D600-2, D606-6 and D706 up to 6.4.9. This affects the...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.