Skip to content
November 4, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Hundreds of Millions Affected: New “nginx-poolslip” Zero-Day Weaponizes ASLR Bypass for Remote Code Execution nginx-poolslip zero-day Nginx 1.31.0 RCE
  • Vulnerability Report

Hundreds of Millions Affected: New “nginx-poolslip” Zero-Day Weaponizes ASLR Bypass for Remote Code Execution

Do Son May 21, 2026 0

Urgent: Millions affected by "nginx-poolslip," a critical Nginx 1.31.0 zero-day that bypasses ASLR via heap feng shui to grant unauthenticated remote RCE.
Signature Bypass Alert: Critical Coder Flaw (CVE-2026-46354) Exposes Git Keys and Developer Tokens Coder Token Theft Vulnerability CVE-2026-46354 Azure Identity
  • Vulnerability Report

Signature Bypass Alert: Critical Coder Flaw (CVE-2026-46354) Exposes Git Keys and Developer Tokens

Do Son May 21, 2026 0

Coder patches a critical 9.1 CVSS signature bypass (CVE-2026-46354) in Azure identities that allows unauthenticated workspace token theft. Patch now!
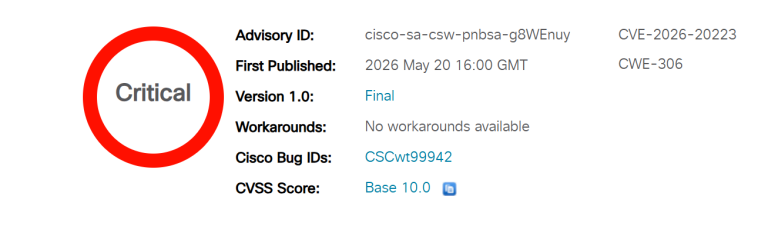
CVSS 10.0 Alert: Critical Cisco Secure Workload Exploit Grants Unauthenticated Site Admin Access Cisco Secure Workload Vulnerability CVE-2026-20223 CVSS 10
  • Vulnerability Report

CVSS 10.0 Alert: Critical Cisco Secure Workload Exploit Grants Unauthenticated Site Admin Access

Do Son May 21, 2026 0

Cisco drops an urgent advisory for CVE-2026-20223 (CVSS 10.0) in Secure Workload. Unauthenticated remote attackers can steal full Site Admin privileges.
Unpatched CVSS 10 Alert: ChromaDB Python Server Grants Pre-Auth RCE via Malicious Hugging Face Models ChromaDB Pre-Auth RCE CVE-2026-45829
  • Vulnerability Report

Unpatched CVSS 10 Alert: ChromaDB Python Server Grants Pre-Auth RCE via Malicious Hugging Face Models

Do Son May 21, 2026 0

Unpatched CVSS 10 flaw (CVE-2026-45829) in ChromaDB allows unauthenticated remote code execution via Hugging Face models. Isolate your servers now!
Double Critical Threat: Google Chrome Rushes Out Urgent Fixes for WebRTC and UI Sandbox Flaws Google Chrome Security Update CVE-2026-9111 Critical Patch
  • Vulnerability Report

Double Critical Threat: Google Chrome Rushes Out Urgent Fixes for WebRTC and UI Sandbox Flaws

Do Son May 21, 2026 0

Google has dropped an urgent Chrome desktop update fixing 16 vulnerabilities, including two critical sandbox subversion flaws in WebRTC and the UI.

Exploited in the Wild: Critical Drupal SQL Injection (CVE-2026-9082) Grants Attacker Root Access CVE-2022-39261 Drupal SQL Injection Vulnerability CVE-2026-9082 PostgreSQL Flaw
  • Vulnerability Report

Exploited in the Wild: Critical Drupal SQL Injection (CVE-2026-9082) Grants Attacker Root Access

Do Son May 21, 2026 0

Urgent: Drupal releases patches for highly critical SQLi flaw CVE-2026-9082. Unauthenticated attackers can exploit PostgreSQL backends for full remote RCE.

Unpatched SGLang Vulnerabilities (CVE-2026-7301) Expose AI Inference Pipelines to RCE SGLang RCE Vulnerability CVE-2026-7301 Zero-Day SGLang RCE AI Infrastructure Vulnerability
  • Vulnerability Report

Unpatched SGLang Vulnerabilities (CVE-2026-7301) Expose AI Inference Pipelines to RCE

Do Son May 21, 2026 0

CERT/CC warns of unpatched critical flaws in SGLang (CVE-2026-7301) exposing AI inference models to unauthenticated RCE. Restrict your ports now!

Critical RCE Exploits Exposed: Apache OFBiz Patches Severe Authentication Bypass Flaws CVE-2022-25371 - CVE-2025-26865 Apache OFBiz RCE Vulnerability CVE-2026-45434 Authentication Bypass
  • Vulnerability Report

Critical RCE Exploits Exposed: Apache OFBiz Patches Severe Authentication Bypass Flaws

Do Son May 21, 2026 0

Apache OFBiz releases version 24.09.06 to patch severe RCE flaws, token forgery, and a critical password-reset authentication bypass. Upgrade now!

Public Exploit Exposes Root Privilege Escalation Flaw in VMware Fusion VMware Fusion TOCTOU Exploit CVE-2026-41702 PoC
  • Vulnerability

Public Exploit Exposes Root Privilege Escalation Flaw in VMware Fusion

Do Son May 21, 2026 0

Technical details and a functional PoC exploit have been released for CVE-2026-41702, a VMware Fusion TOCTOU flaw granting instant root on macOS.

Secret Blizzard Transforms Kazuar into a Modular P2P Botnet Ecosystem Kazuar P2P Botnet Secret Blizzard Malware Evolution
  • Malware

Secret Blizzard Transforms Kazuar into a Modular P2P Botnet Ecosystem

Do Son May 20, 2026 0

Microsoft Threat Intelligence exposes a massive overhaul of the Kazuar backdoor. Secret Blizzard weaponizes a modular, multi-tiered P2P botnet.
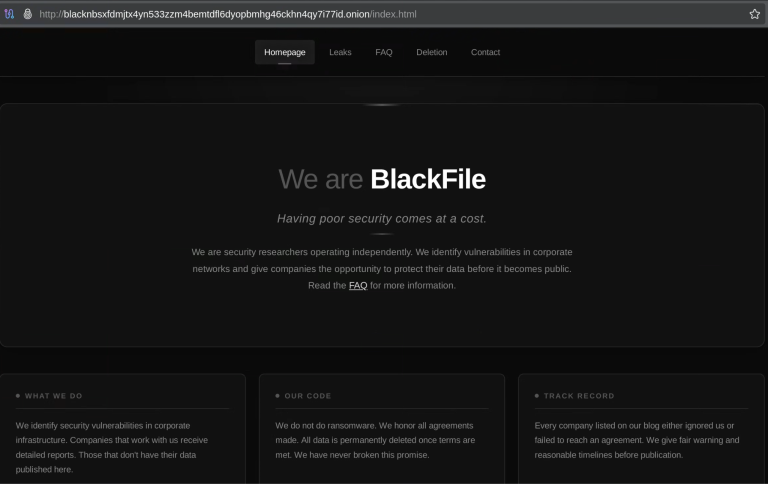
Inside UNC6671’s “BlackFile” Cloud Extortion Campaigns UNC6671 BlackFile Cloud Attacks AiTM MFA Bypass Okta Microsoft
  • Cybercriminals

Inside UNC6671’s “BlackFile” Cloud Extortion Campaigns

Do Son May 20, 2026 0

Google Threat Intelligence exposes UNC6671 ("BlackFile"), an aggressive group using vishing and AiTM proxies to bypass MFA in Microsoft 365 and Okta.

Google Drops Antigravity 2.0 to Orchestrate Teams of Autonomous Coding Agents Gemini CLI deprecation notice as Google moves developers to the Antigravity CLI terminal tool Google Antigravity 2.0 release
  • Technology

Google Drops Antigravity 2.0 to Orchestrate Teams of Autonomous Coding Agents

Do Son May 20, 2026 0

Google launches Antigravity 2.0 at I/O 2026. Powered by Gemini 3.5 Flash, the agent-first platform built a working bare-metal operating system from scratch.

Zero-Trust Voice: Discord Finalizes Mandatory “DAVE” Encryption for All Audio and Video Streams DAVE protocol Discord DAVE protocol encryption
  • Technology

Zero-Trust Voice: Discord Finalizes Mandatory “DAVE” Encryption for All Audio and Video Streams

Do Son May 20, 2026 0

Discord has finalized the global rollout of its open-source DAVE protocol, making end-to-end encryption mandatory for all voice, video, and Go Live streams.

Velvet Chollima Leaves Backend Keys Inside Critical GitLab Dead-Drop Malware Velvet Chollima GitLab Malware Tralert FX EV Certificate
  • Malware

Velvet Chollima Leaves Backend Keys Inside Critical GitLab Dead-Drop Malware

Do Son May 20, 2026 0

Velvet Chollima leaks its own backend infrastructure keys inside a malicious "Tralert FX" installer signed with a valid EV certificate.

Kernel Chaos: Linus Torvalds Blasts “Drive-By” AI Bug Reports Paralyzing Linux Maintainers Linus Torvalds AI bug reports Linux Kernel 7.0 Linux EFI Zboot - CVE-2022-42719 Linux KVM Intel AMX kernel panic, KVM guest host crash 2025
  • Linux

Kernel Chaos: Linus Torvalds Blasts “Drive-By” AI Bug Reports Paralyzing Linux Maintainers

Do Son May 20, 2026 0

Linus Torvalds warns that a massive influx of automated, duplicate AI bug reports is causing severe administrative fatigue across Linux security mailing lists.

Kimsuky Core Upgrades Weaponize Rust Backdoors and VSCode Remote Tunneling Kimsuky HelloDoor Backdoor VSCode Tunneling Espionage
  • Malware

Kimsuky Core Upgrades Weaponize Rust Backdoors and VSCode Remote Tunneling

Do Son May 20, 2026 0

Kimsuky APT evolves its arsenal with "HelloDoor," a new Rust-based backdoor, and hijacks trusted VSCode Remote Tunneling to bypass corporate firewalls.

Google Cloud Abruptly Shuts Down Railway, Sparking Catastrophic Infrastructure Outage Railway infrastructure outage GCP suspension 2026
  • Technology

Google Cloud Abruptly Shuts Down Railway, Sparking Catastrophic Infrastructure Outage

Do Son May 20, 2026 0

Developer cloud platform Railway suffers a widespread, catastrophic infrastructure outage after Google Cloud abruptly suspends its corporate account.

Inside the Breach: How TeamPCP Poisoned a VS Code Extension to Exfiltrate 3,800 GitHub Repositories GitHub source code breach TeamPCP 2026
  • Data Leak

Inside the Breach: How TeamPCP Poisoned a VS Code Extension to Exfiltrate 3,800 GitHub Repositories

Do Son May 20, 2026 0

GitHub confirms a perimeter breach by TeamPCP. An administrative VS Code extension supply-chain worm exfiltrated 3,800 proprietary core source repositories.

Multi-Stage PyInstaller Loader Weaponizes AMSI Patching to Deploy XWorm RAT NATS-as-C2 Sysdig CVE-2026-33017 Langflow RCE Microsoft Phone Link Hijack CloudZ Pheno Plugin Insider Threat BlackCat (ALPHV) OFAC Sanctions DPRK IT Workers Transparent Tribe APT36 React2Shell, EtherRAT SideWinder Espionage, Netlify Phishing DDNS Abuse, C2 Infrastructure Hacking Health Club
  • Malware

Multi-Stage PyInstaller Loader Weaponizes AMSI Patching to Deploy XWorm RAT

Do Son May 20, 2026 0

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!

The Missed Token: Grafana Labs Suffers Source Code Theft via Shai-Hulud npm Worm Campaign CVE-2023-1550 Grafana Labs Cyberattack Mini Shai-Hulud npm Worm
  • Data Leak

The Missed Token: Grafana Labs Suffers Source Code Theft via Shai-Hulud npm Worm Campaign

Do Son May 20, 2026 0

Grafana Labs confirms a targeted cyberattack and source code theft after a missed token from the Mini Shai-Hulud npm worm left a repository exposed.

Critical 9.2 CVSS: NGINX JavaScript Module Flaw (CVE-2026-8711) Triggers Heap Buffer Overflows NGINX JavaScript Module Vulnerability CVE-2026-8711 NGINX 1.30.1 Security Update CVE-2026-42945 RCE NGINX Vulnerability CVE-2026-1642 NGINX Github - CVE-2025-23419
  • Vulnerability Report

Critical 9.2 CVSS: NGINX JavaScript Module Flaw (CVE-2026-8711) Triggers Heap Buffer Overflows

Do Son May 20, 2026 0

F5 warns of a critical 9.2 CVSS flaw (CVE-2026-8711) in NGINX JavaScript (njs). Unauthenticated attackers can trigger heap overflows and potential RCE.

Beyond the Phone: Google Unveils Wear OS 7 with “Wear Widgets” and Wrist-Bound AI Agents Wear OS 7 update Google IO 2026
  • Technology

Beyond the Phone: Google Unveils Wear OS 7 with “Wear Widgets” and Wrist-Bound AI Agents

Do Son May 20, 2026 0

At Google I/O 2026, Google launched Wear OS 7. The smartwatch OS replaces old Tiles with dynamic Wear Widgets and opens up wrist-bound Gemini AI agents.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2026-107441CVSS 8.8
    An out-of-bounds write vulnerability in the CGI program of Zyxel GS1900-24E firmware versions through 2.90(AAHK.2)C0 could allow an...
    Admin intel📅 Updated: Nov 4, 2026
  • CVE-2019-25779CVSS 7.5
    The Diarise theme for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.5.9....
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2023-54413CVSS 6.1
    The WPML plugin for WordPress is vulnerable to Reflected Cross-Site Scripting via the wp_lang parameter in versions up...
    Watchtower Verified📅 Updated: Nov 4, 2026
  • CVE-2026-81648CVSS 10.0
    The CryptoPayment Gateway WordPress plugin from 1.2.1 to 1.2.2 does not apply an authorization check on one of...
    Admin intel📅 Updated: Nov 3, 2026
  • CVE-2026-119977CVSS 8.1
    WordPress Core is vulnerable to Remote Code Execution in versions 4.7 through 7.1.3. This is due to predictable,...
    CISA KEV📅 Added to KEV: Nov 3, 2026
  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114425CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 trusts a file path supplied in externally provided Large File Transfer attachment...
    📅 Updated: Nov 4, 2026
  • CVE-2026-114424CVSS 9.2
    SEPPmail Secure Email Gateway before 15.1.1 can evaluate attacker-influenced replacement text as Perl code in sender or recipient...
    📅 Updated: Nov 4, 2026
  • CVE-2026-28336CVSS 9.9
    SolarWinds Dameware was found to be affected by a command injection vulnerability that could lead to the compromise...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13594CVSS 9.1
    Zoho Corporation's ManageEngine Log360 and EventLog Analyzer versions 13062 and below are vulnerable to an issue that could...
    📅 Updated: Nov 4, 2026
  • CVE-2026-13214CVSS 9.8
    The OCPP 1.6 client in subsys/net/lib/ocpp/ocpp_j.c contains a stack buffer overflow in parse_getconfig_msg(). When handling a GetConfiguration request...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121246CVSS 9.6
    Use after free in WebGL in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121247CVSS 9.6
    Buffer overflow in Dawn in Google Chrome on on Android prior to 157.0.8103.38 allowed a remote attacker to...
    📅 Updated: Nov 4, 2026
  • CVE-2026-121185CVSS 9.6
    Use after free in PictureInPicture in Google Chrome prior to 157.0.8103.38 allowed a remote attacker leveraging social engineering...
    📅 Updated: Nov 4, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.