Skip to content
September 18, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
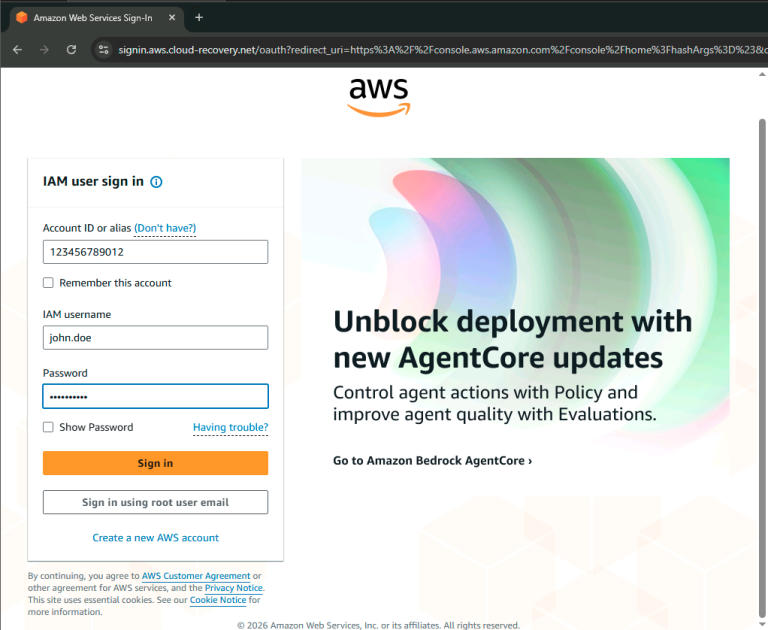
AWS Console Alert: Real-Time “AiTM” Phishing Campaign Bypasses MFA with Rapid Precision AWS Phishing AiTM Attack
  • Cybercriminals

AWS Console Alert: Real-Time “AiTM” Phishing Campaign Bypasses MFA with Rapid Precision

Do Son March 9, 2026 0
Read More Read more about AWS Console Alert: Real-Time “AiTM” Phishing Campaign Bypasses MFA with Rapid Precision
Industrial Alert: Urgent Apache IoTDB Patches Fix RCE and “Open Door” Default Flaws Apache IoTDB JEXL injection Apache IoTDB, Security Vulnerabilities
  • Vulnerability

Industrial Alert: Urgent Apache IoTDB Patches Fix RCE and “Open Door” Default Flaws

Do Son March 9, 2026 0
Read More Read more about Industrial Alert: Urgent Apache IoTDB Patches Fix RCE and “Open Door” Default Flaws
The Hidden Toggle: Why Windows 11’s New One-Click Dark Mode is Hiding in Your Battery Settings Windows 11 Dark Mode toggle
  • Windows

The Hidden Toggle: Why Windows 11’s New One-Click Dark Mode is Hiding in Your Battery Settings

Do Son March 9, 2026 0
Read More Read more about The Hidden Toggle: Why Windows 11’s New One-Click Dark Mode is Hiding in Your Battery Settings
The AI Arms Race for Developers: OpenAI Counters Anthropic with “Codex for Open Source” Codex rate limit reset OpenAI Codex limits, flexible rate limit resets, Codex vs Claude Code Vibe coding software engineer jobs OpenAI Codex for Open Source
  • Technology

The AI Arms Race for Developers: OpenAI Counters Anthropic with “Codex for Open Source”

Do Son March 9, 2026 0
Read More Read more about The AI Arms Race for Developers: OpenAI Counters Anthropic with “Codex for Open Source”
The Robotics Revolt: Why OpenAI’s Top Hardware Executive Quit Over the Pentagon’s New AI Pact OpenAI confidential IPO filing OpenAI code signing certificate rotation AI private equity joint ventures OpenAI Axios Supply Chain Attack OpenAI Promptfoo acquisition OpenAI military resignation ChatGPT Plus military fraud OpenAI smart speaker Jony Ive OpenAI Frontier platform ChatGPT AI age prediction 2026, OpenAI Persona age verification Sarah Friar OpenAI infrastructure, AI Scaling Law revenue OpenAI Gumdrop AI pen, Jony Ive OpenAI hardware 2027 OpenAI New CRO, Denise Dresser Monetization Strategy OpenAI Competitive Pressure Gemini 3 Overtake OpenAI Infrastructure, AI Closed Loop Economy
  • Technology

The Robotics Revolt: Why OpenAI’s Top Hardware Executive Quit Over the Pentagon’s New AI Pact

Do Son March 9, 2026 0
Read More Read more about The Robotics Revolt: Why OpenAI’s Top Hardware Executive Quit Over the Pentagon’s New AI Pact
The Ethics Embargo: Why the Pentagon Blacklisted Anthropic and the Tech Giants Struck Back Anthropic confidential IPO filing Anthropic Google $200 billion deal Anthropic Mythos Preview Anthropic Pentagon blacklist Claude Max 20x open-source Model Distillation Anthropic vs DeepSeek Claude Free tier update 2026
  • Technology

The Ethics Embargo: Why the Pentagon Blacklisted Anthropic and the Tech Giants Struck Back

Do Son March 9, 2026 0
Read More Read more about The Ethics Embargo: Why the Pentagon Blacklisted Anthropic and the Tech Giants Struck Back
Nintendo Sues the U.S. Government Over “Unlawful” Trump Tariffs Nintendo tariff lawsuit 2026 Nintendo Switch 2, MIG Tool Nintendo Switch 2, USB-C Restrictions Nintendo Switch 2, Vulnerability
  • Technology

Nintendo Sues the U.S. Government Over “Unlawful” Trump Tariffs

Do Son March 9, 2026 0
Read More Read more about Nintendo Sues the U.S. Government Over “Unlawful” Trump Tariffs
Torrent of Threats: China-Nexus APT UAT-9244 Hijacks South American Telecoms with PeerTime Backdoor BingX cyberattack FortiGate SSO Attacks Firewall Config Theft
  • Cyber Security
  • Malware

Torrent of Threats: China-Nexus APT UAT-9244 Hijacks South American Telecoms with PeerTime Backdoor

Do Son March 9, 2026 0
Read More Read more about Torrent of Threats: China-Nexus APT UAT-9244 Hijacks South American Telecoms with PeerTime Backdoor
Escalation in the Shadows: Iranian APT Seedworm Deploys ‘Dindoor’ Backdoor in New Cyberoffensive Vulnerability Digest Zero-Day Exploits Seedworm APT Dindoor Backdoor RedKitten Campaign AI-Generated Malware WSUS RCE ShadowPad CVE-2025-59287
  • Cyber Security
  • Malware

Escalation in the Shadows: Iranian APT Seedworm Deploys ‘Dindoor’ Backdoor in New Cyberoffensive

Do Son March 9, 2026 0
Read More Read more about Escalation in the Shadows: Iranian APT Seedworm Deploys ‘Dindoor’ Backdoor in New Cyberoffensive
Fake GitHub Repositories Unleash BoryptGrab Stealer and TunnesshClient Backdoor TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Fake GitHub Repositories Unleash BoryptGrab Stealer and TunnesshClient Backdoor

Do Son March 9, 2026 0
Read More Read more about Fake GitHub Repositories Unleash BoryptGrab Stealer and TunnesshClient Backdoor
Critical 9.4 CVSS Zephyr RTOS Flaw Exposes Millions of IoT Devices to RCE Zephyr RTOS Vulnerability CVE-2026-1678
  • Vulnerability Report

Critical 9.4 CVSS Zephyr RTOS Flaw Exposes Millions of IoT Devices to RCE

Do Son March 9, 2026 0
Read More Read more about Critical 9.4 CVSS Zephyr RTOS Flaw Exposes Millions of IoT Devices to RCE
Vault Unlocked: High-Severity Flaws in Vaultwarden Expose Encrypted Secrets and Allow Privilege Escalation Vaultwarden Vulnerabilities CVE-2026-27898
  • Vulnerability Report

Vault Unlocked: High-Severity Flaws in Vaultwarden Expose Encrypted Secrets and Allow Privilege Escalation

Do Son March 9, 2026 0
Read More Read more about Vault Unlocked: High-Severity Flaws in Vaultwarden Expose Encrypted Secrets and Allow Privilege Escalation
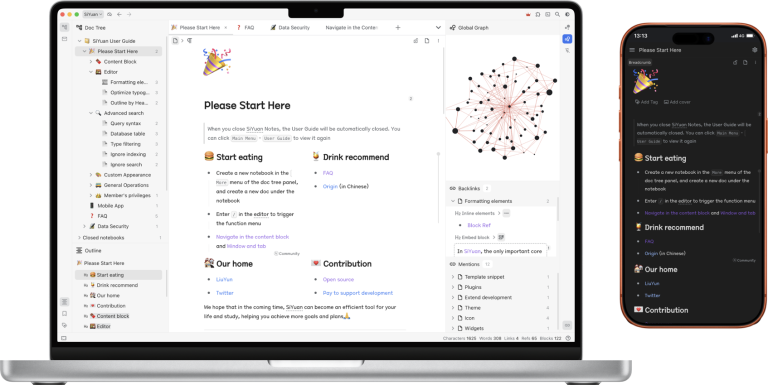
Critical 9.3 CVSS Flaw in SiYuan Lets Hackers Steal Private Notes via SVG Injection SiYuan XSS Vulnerability CVE-2026-29183
  • Vulnerability Report

Critical 9.3 CVSS Flaw in SiYuan Lets Hackers Steal Private Notes via SVG Injection

Do Son March 9, 2026 0
Read More Read more about Critical 9.3 CVSS Flaw in SiYuan Lets Hackers Steal Private Notes via SVG Injection
Critical Bypasses and Secret Leaks Patched in Apache ZooKeeper CVE-2023-44981 Apache ZooKeeper Vulnerabilities CVE-2026-24281
  • Vulnerability Report

Critical Bypasses and Secret Leaks Patched in Apache ZooKeeper

Do Son March 9, 2026 0
Read More Read more about Critical Bypasses and Secret Leaks Patched in Apache ZooKeeper
Polygon Powered: Vietnamese Operator Deploys 16 Generations of LuaJIT Malware via GitHub Cemu emulator Linux malware Blitz Brigantine AOBackdoor GitHub Malware Campaign StealC Infostealer TamperedChef Malware, SEO Poisoning Carbanak malware RubyGems Supply Chain, Infostealer
  • Malware

Polygon Powered: Vietnamese Operator Deploys 16 Generations of LuaJIT Malware via GitHub

Do Son March 9, 2026 0
Read More Read more about Polygon Powered: Vietnamese Operator Deploys 16 Generations of LuaJIT Malware via GitHub
1-Click to Compromise: Critical 9.3 CVSS Flaw in ZITADEL Exposes Accounts to Full Takeover ZITADEL Vulnerability CVE-2026-29191 CVE-2025-27507 ZITADEL SSRF, Login UI Hijack
  • Vulnerability Report

1-Click to Compromise: Critical 9.3 CVSS Flaw in ZITADEL Exposes Accounts to Full Takeover

Do Son March 9, 2026 0
Read More Read more about 1-Click to Compromise: Critical 9.3 CVSS Flaw in ZITADEL Exposes Accounts to Full Takeover
From Theory to Threat: Hackers Are Now Weaponizing Web Pages to Brainwash AI Agents axios Supply Chain Attack WAVESHAPER.V2 SnappyBee Malware Salt Typhoon Stately Taurus ScoringMathTea RAT, Lazarus Reflective DLL
  • Cybercriminals

From Theory to Threat: Hackers Are Now Weaponizing Web Pages to Brainwash AI Agents

Do Son March 9, 2026 0
Read More Read more about From Theory to Threat: Hackers Are Now Weaponizing Web Pages to Brainwash AI Agents
Dust Specter: Iran-Linked Hackers Weaponize Iraqi Government Sites in New Cyber Espionage Campaign Zyxel security - Mitel MiCollab Vulnerability
  • Cyber Security
  • Malware

Dust Specter: Iran-Linked Hackers Weaponize Iraqi Government Sites in New Cyber Espionage Campaign

Do Son March 9, 2026 0
Read More Read more about Dust Specter: Iran-Linked Hackers Weaponize Iraqi Government Sites in New Cyber Espionage Campaign
Unauthenticated Nginx UI Flaw Leaks Decryption Keys and Server Secrets Nginx UI Vulnerability CVE-2026-27944
  • Vulnerability Report

Unauthenticated Nginx UI Flaw Leaks Decryption Keys and Server Secrets

Do Son March 8, 2026 0
Read More Read more about Unauthenticated Nginx UI Flaw Leaks Decryption Keys and Server Secrets
AI vs. Bugs: OpenAI Launches “Codex Security” to Revolutionize AppSec OpenAI Advanced Account Security Phishing-Resistant AI Authentication OpenAI Codex Security AI Application Security
  • Technology

AI vs. Bugs: OpenAI Launches “Codex Security” to Revolutionize AppSec

Do Son March 7, 2026 0
Read More Read more about AI vs. Bugs: OpenAI Launches “Codex Security” to Revolutionize AppSec
The Silicon Squeeze: Apple Sacrifices High-End Memory to Survive the Global AI Chip Famine Apple memory supply chain crisis
  • Technology

The Silicon Squeeze: Apple Sacrifices High-End Memory to Survive the Global AI Chip Famine

Do Son March 7, 2026 0
Read More Read more about The Silicon Squeeze: Apple Sacrifices High-End Memory to Survive the Global AI Chip Famine
The Personhood Barrier: Why the US Supreme Court and UK Creators Just Slammed the Door on AI Copyright AI pre-release vetting AI copyright law US UK FoundationMotion, AI Motion Understanding AI Deregulation, DOGE AI Self-Preservation, GPT-4o Country of Geniuses
  • Technology

The Personhood Barrier: Why the US Supreme Court and UK Creators Just Slammed the Door on AI Copyright
Do Son March 7, 2026 0
Read More Read more about The Personhood Barrier: Why the US Supreme Court and UK Creators Just Slammed the Door on AI Copyright
❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📧

Email Delivery
Get threat intel straight to your inbox.

♾️

Unlimited Vendors
Track every technology in your stack.

🚨

All New CVE Alerts
Be the first to know about new flaws.

⚙️

Custom EPSS Threshold
Filter noise, focus on real risks.

💬

Slack & Teams Webhook
Integrate directly into your SecOps.

🚫

100% Ad-Free
Enjoy an uninterrupted reading experience.

$7/mo
Subscribe Now

🚨 Active Exploits in the Wild

  • CVE-2025-39964CVSS 7.8
    In the Linux kernel, the following vulnerability has been resolved: crypto: af_alg - Disallow concurrent writes in af_alg_sendmsg...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-53266CVSS 8.8
    In the Linux kernel, the following vulnerability has been resolved: netfilter: bridge: make ebt_snat ARP rewrite writable The...
    CISA KEV📅 Added to KEV: Sep 18, 2026
  • CVE-2026-76460CVSS 10.0
    A vulnerability in an API of Cisco Identity Services Engine (ISE) could allow an unauthenticated, remote attacker to...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-89026CVSS 9.8
    The Issabel Framework, the web framework supporting Issabel PBX software, before commit b97dbaf contains a hard-coded HS256 JWT...
    Admin intel📅 Updated: Sep 16, 2026
  • CVE-2026-58704
    In Cellular Modem, there is a possible permission bypass due to a logic error in the code. This...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-87886
    Exploitation of this vulnerability has been detected in the wild in limited, targeted attacks against Acronis Backup plugin...
    Admin intelCISA KEV📅 Added to KEV: Sep 16, 2026📅 Updated: Sep 16, 2026
  • CVE-2026-87827CVSS 10.0
    Certain KGUARD DVR devices running vulnerable firmware expose a system command execution service on all network interfaces without...
    Admin intel📅 Updated: Sep 15, 2026
  • CVE-2026-78006CVSS 9.8
    The The Events Calendar plugin for WordPress is vulnerable to Remote Code Execution in all versions up to,...
    Admin intel📅 Updated: Sep 15, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-59163CVSS 9.1
    Mnemosyne is a memory layer for artificial intelligence agents. Prior to v3.10.1, the auth check in mnemosyne/core/sync_server.py parsed...
    📅 Updated: Sep 18, 2026
  • CVE-2026-92489CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: xfrm: Fix skb double-free in xfrm_dev_direct_output() A return...
    📅 Updated: Sep 18, 2026
  • CVE-2026-90414CVSS 9.1
    In the Linux kernel, the following vulnerability has been resolved: IB/isert: reject PDUs declaring more data than was...
    📅 Updated: Sep 18, 2026
  • CVE-2026-90413CVSS 9.1
    In the Linux kernel, the following vulnerability has been resolved: IB/isert: reject login PDUs declaring more data than...
    📅 Updated: Sep 18, 2026
  • CVE-2026-90235CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: sunrpc: xprtsock: annotate shared socket callbacks with READ_ONCE/WRITE_ONCE...
    📅 Updated: Sep 18, 2026
  • CVE-2026-90230CVSS 9.1
    In the Linux kernel, the following vulnerability has been resolved: nvmet: fix heap out-of-bounds read in nvmet_auth_negotiate() nvmet_execute_auth_send()...
    📅 Updated: Sep 18, 2026
  • CVE-2026-90173CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: smb: smbdirect: free completion queues with ib_free_cq() smbdirect_connection_destroy_qp()...
    📅 Updated: Sep 18, 2026
  • CVE-2026-90151CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: NFSv4: remove callback IDR entry on client allocation...
    📅 Updated: Sep 18, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q2 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.