Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
JetBrains Software Vulnerabilities Impact TeamCity JetBrains software vulnerabilities TeamCity RCE bugs
  • Vulnerability Report

JetBrains Software Vulnerabilities Impact TeamCity

Do Son October 10, 2026 0

Discover the latest JetBrains software vulnerabilities, including TeamCity RCE bugs and Exposed SQLi flaws. Apply security patches immediately.
Ricardo Data Leak Exposes User Contact Details Ricardo data leak illustration highlighting the SMG security vulnerability.
  • Data Leak

Ricardo Data Leak Exposes User Contact Details

Do Son October 9, 2026 0

A recent Ricardo data leak exposed 890,000 users. SMG fixed the security vulnerability, confirming passwords remain safe.
Nginx UI RCE Vulnerability Disclosed With PoC Exploit Code Nginx UI RCE vulnerability CVE-2026-107806
  • Vulnerability Report

Nginx UI RCE Vulnerability Disclosed With PoC Exploit Code

Do Son October 9, 2026 0

A critical Nginx UI RCE vulnerability (CVE-2026-107806) is publicly disclosed with PoC exploit code. Admins must patch now to prevent system takeover.
Critical Apache Camel Karavan Vulnerabilities Threaten Servers Apache Camel Karavan vulnerabilities CVE-2026-103413 CVE-2026-103412
  • Vulnerability Report

Critical Apache Camel Karavan Vulnerabilities Threaten Servers

Do Son October 9, 2026 0

Discover how critical Apache Camel Karavan vulnerabilities (CVE-2026-103413 and CVE-2026-103412) allow code execution. Update to version 4.22.1 now.
Grid Protection Alliance openPDC and openHistorian Flaws openPDC openHistorian vulnerabilities CVE-2026-100730 CVE-2026-105281
  • Vulnerability Report

Grid Protection Alliance openPDC and openHistorian Flaws

Do Son October 9, 2026 0

Fix critical openPDC openHistorian vulnerabilities like CVE-2026-100730 and CVE-2026-105281. CISA urges patching these severe RCE flaws immediately.
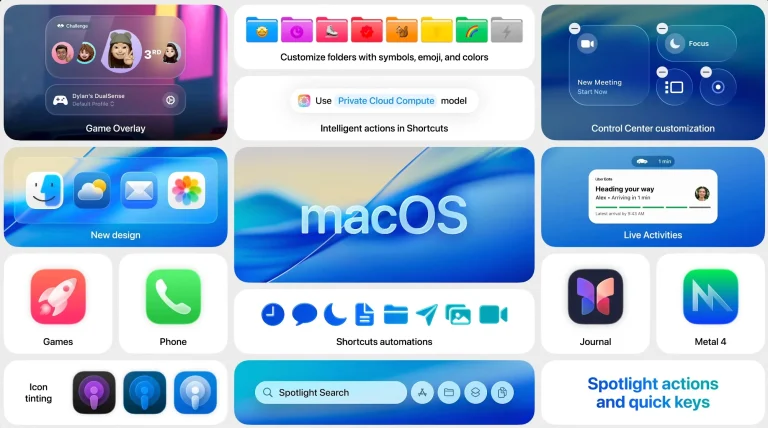
The Growing Backlash Against Apple Intelligence Integration Apple Intelligence storage macOS 27 Golden Gate enterprise security
  • Data Leak

The Growing Backlash Against Apple Intelligence Integration

Do Son October 9, 2026 0

Explore how massive Apple Intelligence storage demands in macOS 27 Golden Gate face fierce backlash regarding enterprise security and user limitations.
Controversy Surrounding the .lan Domain Application ICANN gTLD applications .lan domain OpenWrt local network configuration
  • Technology

Controversy Surrounding the .lan Domain Application

Do Son October 9, 2026 0

Discover the controversy surrounding ICANN gTLD applications for the .lan domain. Learn how this impacts OpenWrt and local network configurations worldwide.
How residential proxy networks get abused and what defenders can detect image
  • Technique

How residential proxy networks get abused and what defenders can detect

Do Son October 9, 2026 0
The alert fires on the login endpoint, but the traffic behind it looks clean. Each attempt comes...
Read More Read more about How residential proxy networks get abused and what defenders can detect
The Reality of Ransomware Recovery Services MonsterCloud ransomware decryption fraud Zohar Pinhasi data recovery
  • Cybercriminals

The Reality of Ransomware Recovery Services

Do Son October 9, 2026 0

Discover the MonsterCloud ransomware decryption fraud. Learn how Zohar Pinhasi allegedly deceived clients by secretly paying hackers for data recovery keys.
SonicWall SMA1000 Vulnerability Exploited in the Wild A security warning highlighting a critical SonicWall SMA1000 vulnerability under active exploitation
  • Vulnerability Report

SonicWall SMA1000 Vulnerability Exploited in the Wild

Do Son October 9, 2026 0

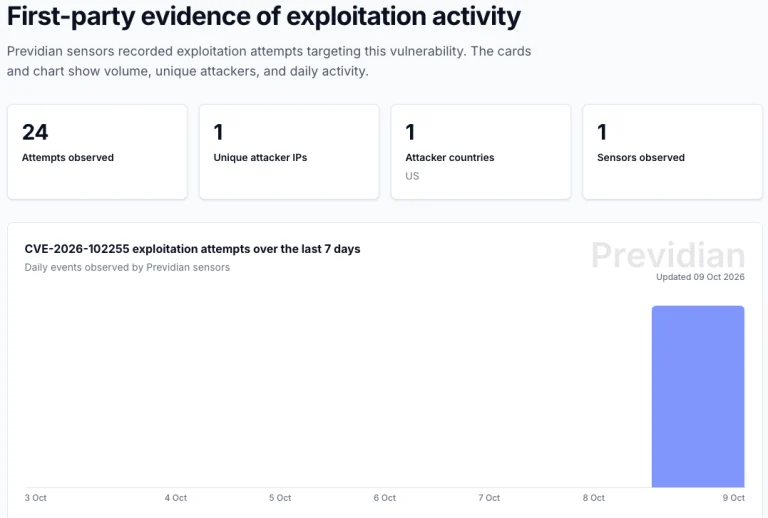
Attackers target a critical SonicWall SMA1000 vulnerability in the wild. Apply vendor hotfixes to secure remote access gateways against CVE-2026-102255.
OpenAI GPT-6 Introduces Revolutionary Intelligent UI OpenAI GPT-6 Intelligent UI interactive interface ChatGPT upgrade
  • Technology

OpenAI GPT-6 Introduces Revolutionary Intelligent UI

Do Son October 9, 2026 0

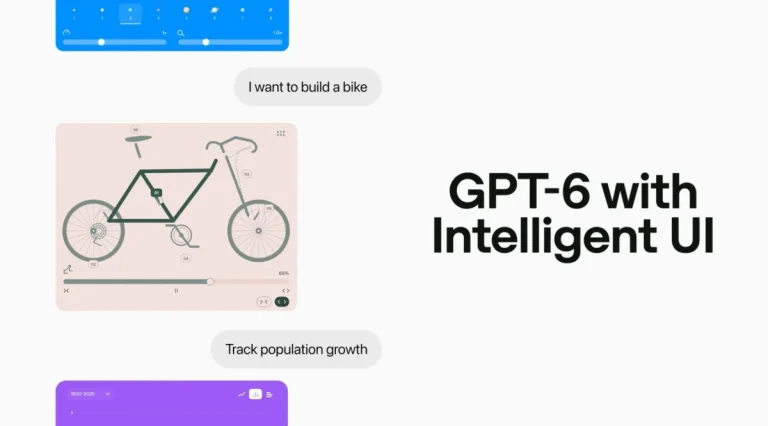
Discover how the new OpenAI GPT-6 Intelligent UI transforms ChatGPT into an on-demand software factory with interactive interfaces and streaming reasoning.
SoftBank IDCF Cloud Ransomware Attack Exposed by Hackers SoftBank IDCF Cloud ransomware attack East Japan Region 1 outage
  • Cybercriminals

SoftBank IDCF Cloud Ransomware Attack Exposed by Hackers

Do Son October 9, 2026 0

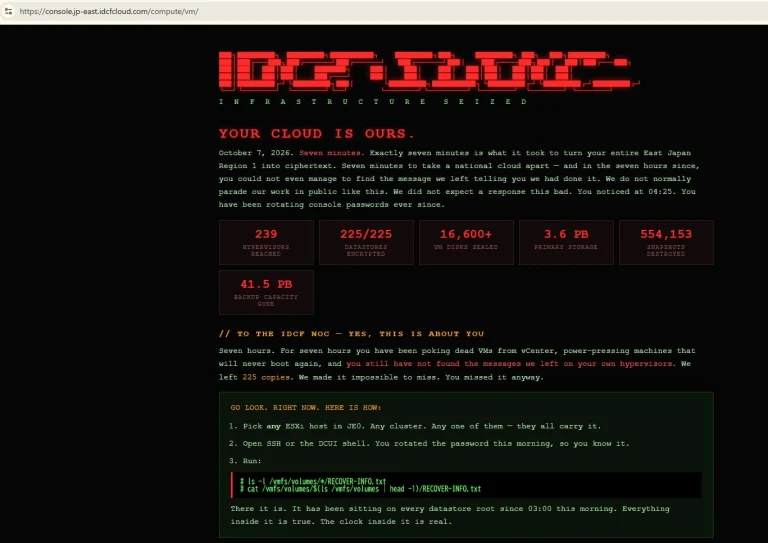
Explore the devastating SoftBank IDCF Cloud ransomware attack. Read the hackers' humiliating note revealing the massive East Japan Region 1 outage.
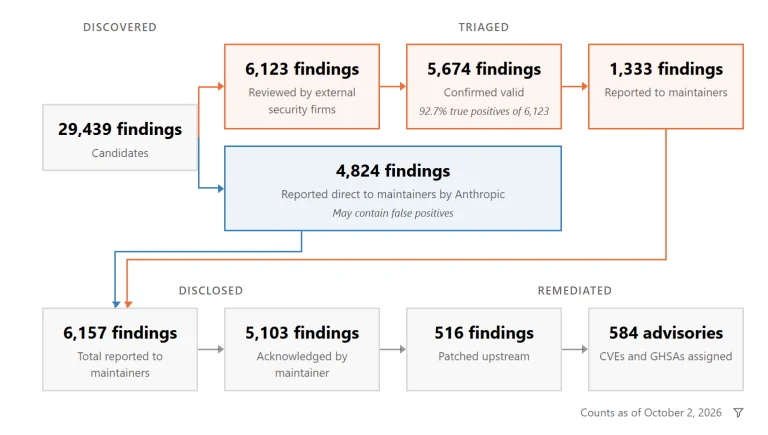
Anthropic Introduces OSS Scanner for Open Source Projects Anthropic OSS Scanner open source vulnerability scanning
  • Technology

Anthropic Introduces OSS Scanner for Open Source Projects

Do Son October 9, 2026 0

Discover the Anthropic OSS Scanner. Learn how AI models provide automated vulnerability scanning and remediation for open source projects.
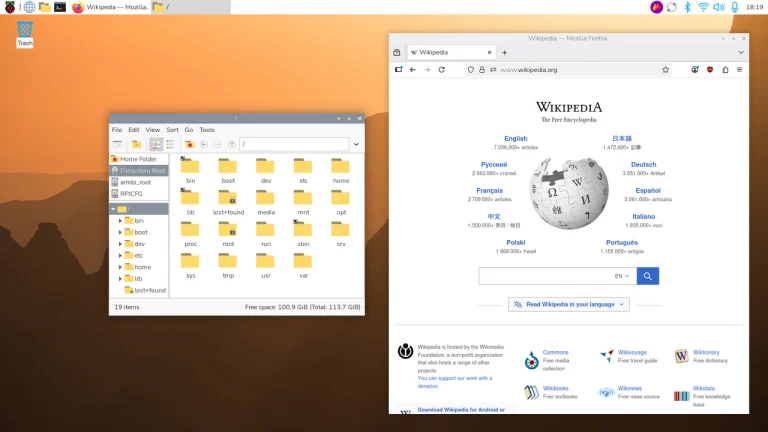
Raspberry Pi OS Update: Squashing Desktop Bugs Raspberry Pi OS update Linux desktop environments bug fixes
  • Linux

Raspberry Pi OS Update: Squashing Desktop Bugs

Do Son October 9, 2026 0

Discover the latest Raspberry Pi OS update. Learn how this release squashes critical bugs, optimizes Linux desktop environments, and refines the Dock interface.
Microsoft 365 Squeezes Family Plan Storage Microsoft 365 storage adjustments family plan OneDrive changes
  • Technology

Microsoft 365 Squeezes Family Plan Storage

Do Son October 9, 2026 0

Discover the impact of the Microsoft 365 storage changes. Learn how the new 2TB shared OneDrive limit severely squeezes Family Plan users and their files.
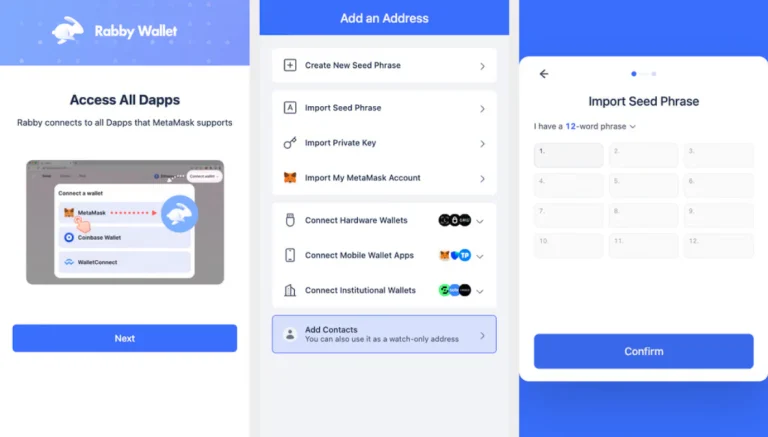
16 Fake Rabby and OKX Firefox Extensions Stole Crypto Wallet Recovery Phrases Malicious Firefox extensions posing as Rabby and OKX wallets acting as crypto wallet stealers
  • Malware

16 Fake Rabby and OKX Firefox Extensions Stole Crypto Wallet Recovery Phrases

Do Son October 9, 2026 0

Socket found 16 malicious Firefox extensions posing as Rabby and OKX. These crypto wallet stealers grabbed seed phrases. Here is what to do.
Let’s Encrypt Accelerates the Push for Automation Let's Encrypt certificate lifespan reduction automation TLS certificates
  • Technology

Let’s Encrypt Accelerates the Push for Automation

Do Son October 9, 2026 0

Discover the impact of the Let's Encrypt certificate lifespan reduction. Learn how the shift to 45-day TLS certificates demands robust ACME automated renewal.
The Silent Threat of Midnight Mimosa Malware Midnight Mimosa malware cheap Android devices Bitdefender report cybersecurity
  • Malware

The Silent Threat of Midnight Mimosa Malware

Do Son October 9, 2026 0

Discover the Midnight Mimosa malware threatening cheap Android devices. Read the Bitdefender report on how OEMs pre-install this dangerous cybersecurity threat.
CrowdStrike Links South Korean Bank Breaches to Chinese AI Pentesting Tool ARTEX ARTEX AI tool used by a suspected Chinese-speaking attacker against South Korean banks
  • Cybercriminals

CrowdStrike Links South Korean Bank Breaches to Chinese AI Pentesting Tool ARTEX

Do Son October 9, 2026 0

CrowdStrike links the ARTEX AI tool to breaches at South Korean banks, run by a suspected Chinese-speaking, profit-driven attacker.
Actively Exploited Software Vulnerabilities Demand Patching, CISA Warns Actively exploited software vulnerabilities enabling critical remote code execution.
  • Vulnerability Report

Actively Exploited Software Vulnerabilities Demand Patching, CISA Warns

Do Son October 9, 2026 0

Five actively exploited software vulnerabilities threaten critical systems. Update your servers now to prevent critical remote code execution attacks.
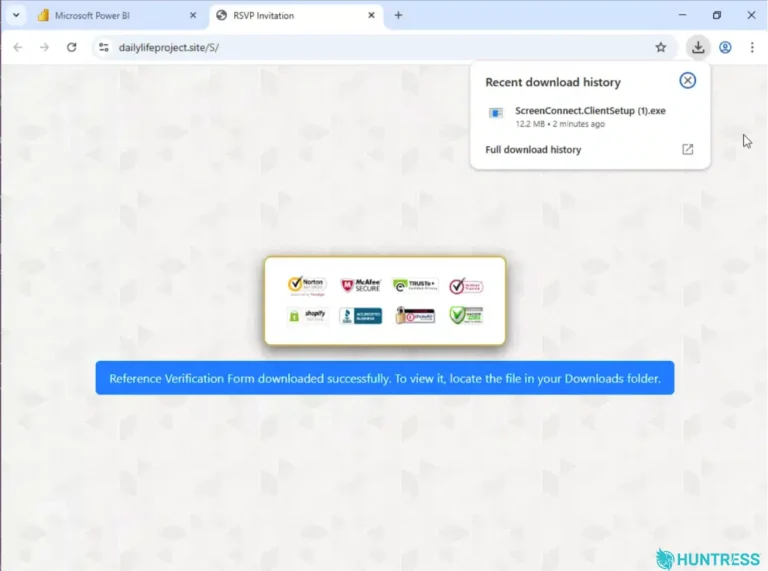
Phishing Campaign Abuses Microsoft Power BI to Install Rogue ScreenConnect Clients Power BI phishing campaign delivering rogue ScreenConnect remote access clients
  • Malware

Phishing Campaign Abuses Microsoft Power BI to Install Rogue ScreenConnect Clients

Do Son October 9, 2026 0

A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
Urgent Security Patches Fix IBM Verify Access Vulnerabilities Urgent Security Patches Fix IBM Verify Access Vulnerabilities
  • Vulnerability Report

Urgent Security Patches Fix IBM Verify Access Vulnerabilities

Do Son October 9, 2026 0

Multiple IBM Verify Access vulnerabilities expose systems to remote attacks. Update your software now to block these critical security flaws.

❮ Prev Page
Next Page ❯

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
  • CVE-2026-101767CVSS 9.8
    Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2023-22793CVSS 9.3
    A vulnerability allowing an unauthenticated attacker to perform remote code execution (RCE) on servers running the Veeam Virtualization...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61707CVSS 9.0
    SOCFortress CoPilot focuses on providing a single pane of glass for all your security operations needs. Prior to...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61645CVSS 9.1
    Docat is a tool for hosting versioned static documentation. In the affected implementation, an arbitrary file upload vulnerability...
    📅 Updated: Oct 29, 2026
  • CVE-2026-31158CVSS 9.8
    SQL Injection vulnerability in CRM SOFTTRADE Infotech (aka softtradeindia) 1.0 allows a remote attacker to execute arbitrary code...
    📅 Updated: Oct 29, 2026
  • CVE-2026-107032CVSS 9.1
    Insecure permissions in Bulk Share : Location Sender v2.1.0 (versionCode 5) allows unauthorized attackers to invoke an exported...
    📅 Updated: Oct 29, 2026
  • CVE-2024-8517CVSS 9.8
    SPIP before 4.3.2, 4.2.16, and 4.1.18 is vulnerable to a command injection issue. A remote and unauthenticated attacker...
    📅 Updated: Oct 29, 2026
  • CVE-2026-82854CVSS 9.3
    Nodemailer before 8.0.4 is vulnerable to SMTP command injection through the unsanitized envelope.size parameter. When an application passes...
    📅 Updated: Oct 29, 2026
  • CVE-2026-81694CVSS 9.3
    openssl-encrypt (pip package, versions
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.