Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
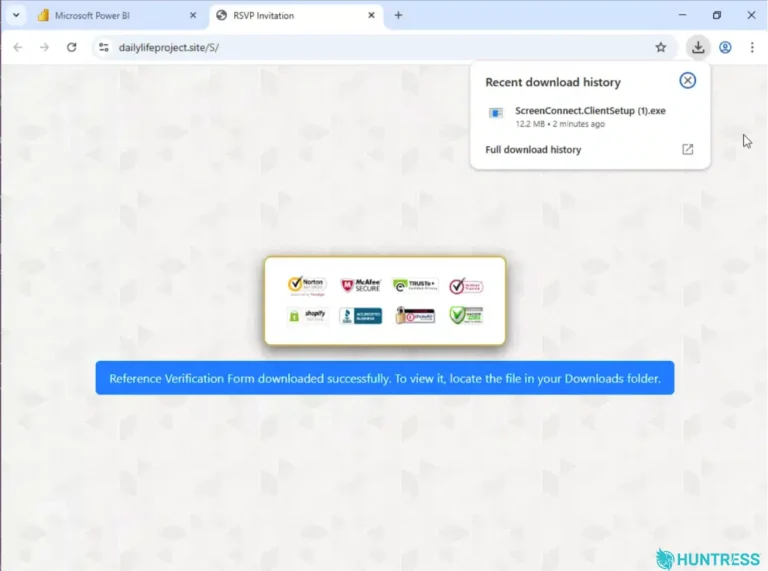
Phishing Campaign Abuses Microsoft Power BI to Install Rogue ScreenConnect Clients Power BI phishing campaign delivering rogue ScreenConnect remote access clients
  • Malware

Phishing Campaign Abuses Microsoft Power BI to Install Rogue ScreenConnect Clients

Do Son October 9, 2026 0

A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
Urgent Security Patches Fix IBM Verify Access Vulnerabilities Urgent Security Patches Fix IBM Verify Access Vulnerabilities
  • Vulnerability Report

Urgent Security Patches Fix IBM Verify Access Vulnerabilities

Do Son October 9, 2026 0

Multiple IBM Verify Access vulnerabilities expose systems to remote attacks. Update your software now to block these critical security flaws.
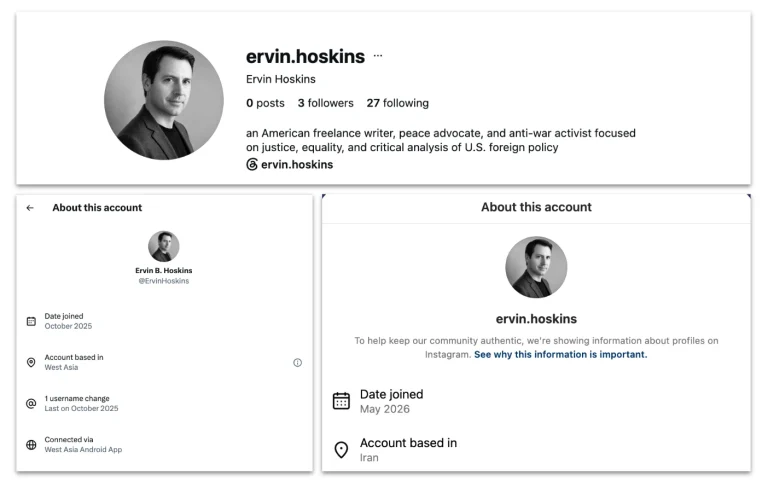
OpenAI Disrupts Russian and Iranian False Front Operations Graphic showing AI false front operations and deceptive false front operations targeting digital media
  • Cybercriminals

OpenAI Disrupts Russian and Iranian False Front Operations

Do Son October 9, 2026 0

OpenAI disrupted state-backed AI false front operations. Threat actors ran covert false front operations using fake personas to manipulate global media.

Chinese State Hackers Target Critical Infrastructure in Global Data Theft exfiltrating AWS credentials - fabrice package
  • Cybercriminals

Chinese State Hackers Target Critical Infrastructure in Global Data Theft

Do Son October 9, 2026 0

Chinese state hackers allegedly use Integrity Technology Group tools for botnet data theft. Protect your networks from this massive cyberespionage campaign.
Critical Tapo C325WB Vulnerabilities Expose Smart Cameras TP-Link smart camera exposed to critical Tapo C325WB vulnerabilities
  • Vulnerability Report

Critical Tapo C325WB Vulnerabilities Expose Smart Cameras

Do Son October 9, 2026 0

Discover the new critical Tapo C325WB vulnerabilities exposing TP-Link cameras. Learn how to patch these Tapo C325WB vulnerabilities and secure your video.
AhsayCBS Vulnerabilities Exploited in Wild Attacks FSB Center 16 targeting vulnerable routers across critical infrastructure via weak SNMP
  • Vulnerability Report

AhsayCBS Vulnerabilities Exploited in Wild Attacks

Do Son October 9, 2026 0

Threat actors are actively abusing critical AhsayCBS vulnerabilities in the wild to deploy cryptominers. Patch unpatched AhsayCBS vulnerabilities now.
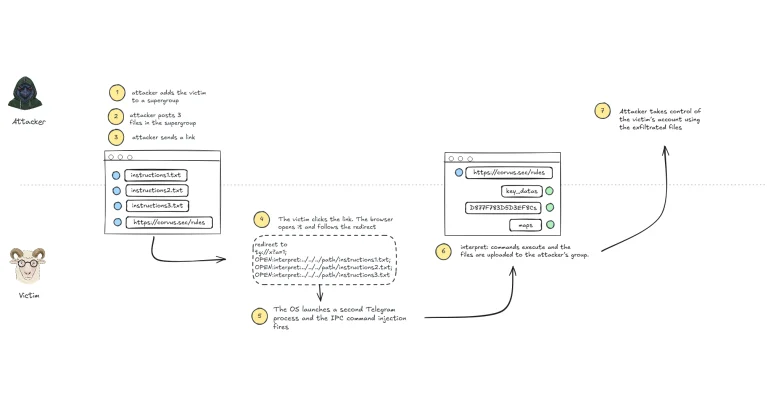
Telegram Desktop Account Takeover PoC Disclosed Telegram Desktop account takeover illustration showing CVE-2026-107181 exploit code
  • Vulnerability Report

Telegram Desktop Account Takeover PoC Disclosed

Do Son October 9, 2026 0

A critical Telegram Desktop account takeover vulnerability (CVE-2026-107181) exposes users to session hijacking. Exploit details and PoC are now public.
HPE Fixes Critical iLO 7 Admin Access Flaw and iMC Authentication Bypass HPE iLO 7 vulnerability CVE-2026-79820 admin access and HPE iMC authentication bypass CVE-2026-79842 fixed
  • Vulnerability Report

HPE Fixes Critical iLO 7 Admin Access Flaw and iMC Authentication Bypass

Do Son October 9, 2026 0

HPE fixes a critical HPE iLO 7 vulnerability, CVE-2026-79820, and iMC authentication bypass CVE-2026-79842. Update iLO to 1.25.01 now.
Citrix Warns of Critical NetScaler SAML Flaw CVE-2026-107406 That Can Lead to Remote Code Execution Citrix NetScaler vulnerability CVE-2026-107406 memory overflow in SAML-configured NetScaler ADC and Gateway can lead to remote code execution
  • Vulnerability Report

Citrix Warns of Critical NetScaler SAML Flaw CVE-2026-107406 That Can Lead to Remote Code Execution

Do Son October 9, 2026 0

Critical Citrix NetScaler vulnerability CVE-2026-107406 (CVSS 9.5) can lead to RCE on SAML-configured ADC and Gateway. Upgrade now.
IBM Patches 23 DataPower Gateway Flaws, Including Four Critical Remote Code Execution and XSS Bugs IBM DataPower Gateway vulnerabilities CVE-2026-15762 and CVE-2026-16340 remote code execution and CVE-2026-14990 XSS fixed in 11.0.0.3
  • Vulnerability Report

IBM Patches 23 DataPower Gateway Flaws, Including Four Critical Remote Code Execution and XSS Bugs

Do Son October 8, 2026 0

IBM fixes 23 IBM DataPower Gateway vulnerabilities, including critical RCE flaws CVE-2026-15762 and CVE-2026-16340. Upgrade to 11.0.0.3 now.
Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code insignary_logo_1791211062PNrqmaRSIt
  • Press Release

Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code

cybernewswire October 8, 2026 0
Toronto, Canada, 8th October 2026, CyberNewswire
Read More Read more about Insignary Launches Clarity AIR to Detect Undeclared Open-Source and AI-Written Code
Claude AI Chat Leads to Florida Arrest Claude AI chat threats arrest security monitoring
  • Technology

Claude AI Chat Leads to Florida Arrest

Do Son October 8, 2026 0

A Florida woman faces charges for AI chat threats after Claude developers reported her dangerous messages to law enforcement for safety policy violations.
Chrome 155 Defaults to Native JPEG XL Support Chrome JPEG XL support decoding JXL image format
  • Technology

Chrome 155 Defaults to Native JPEG XL Support

Do Son October 8, 2026 0

Google officially introduces Chrome JPEG XL support by default in version 155. Explore how this image format enhances quality, compression, and performance.
ICANN Reveals Massive Surge in AI Domain Name Applications ICANN new domain applications and AI extensions
  • Technology

ICANN Reveals Massive Surge in AI Domain Name Applications

Do Son October 8, 2026 0

Discover the latest ICANN new domain applications. Explore how tech giants are rushing to secure AI domain extensions and top-level domains.
OpenAI Math Model Breakthroughs: AI Solves Centennial Enigmas OpenAI math model breakthroughs resolving complex mathematical proofs and AI mathematical proofs
  • Technology

OpenAI Math Model Breakthroughs: AI Solves Centennial Enigmas

Do Son October 8, 2026 0

Has the new OpenAI math model breakthroughs conquered the Riemann Hypothesis? Discover how the unreleased ChatGPT Pioneer Model shocks the academic community.
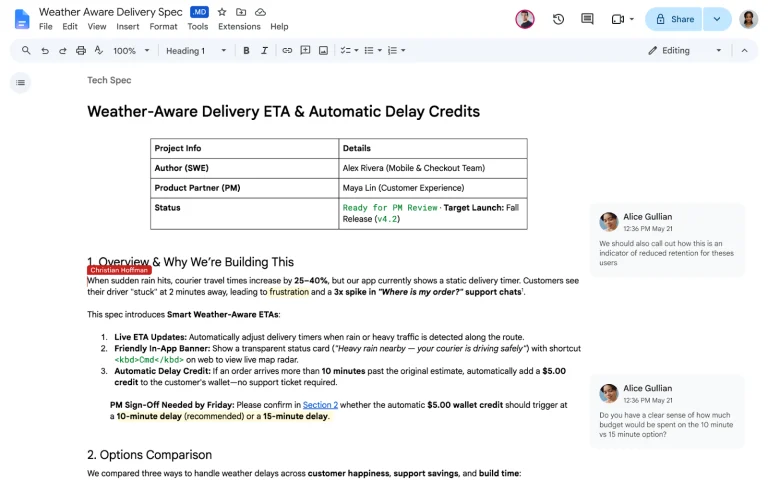
Google Adds Native Markdown Support Google Markdown native support Drive Docs collaboration
  • Technology

Google Adds Native Markdown Support

Do Son October 8, 2026 0

Google introduces Markdown native support for Docs and Drive. Learn how this new feature enhances editing, preserves formatting, and aids AI collaboration.
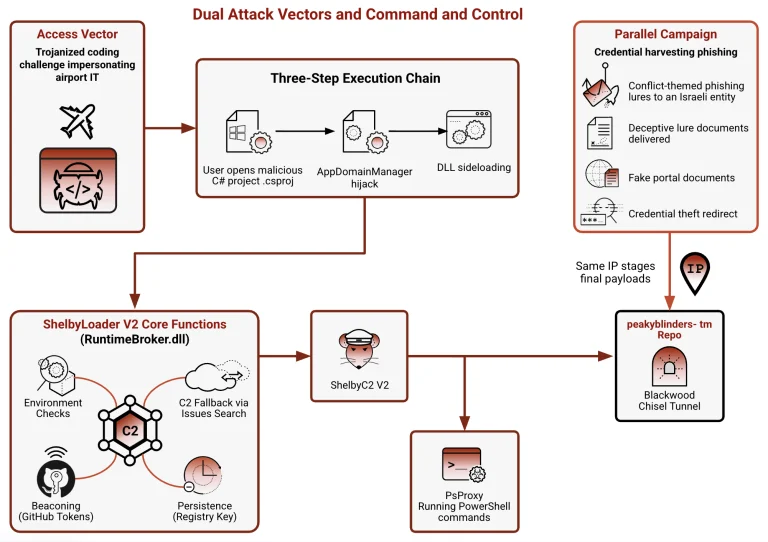
Iran-Linked Hackers Pose as Dubai Airports Recruiters in Blinder Tunnel Campaign Against Iraq Blinder Tunnel campaign using a fake Dubai Airports coding test to deliver ShelbyLoader V2
  • Cybercriminals

Iran-Linked Hackers Pose as Dubai Airports Recruiters in Blinder Tunnel Campaign Against Iraq

Do Son October 8, 2026 0

The Blinder Tunnel campaign used a fake Dubai Airports coding test to drop ShelbyLoader V2 on an Iraqi target. See how it works and how to defend.
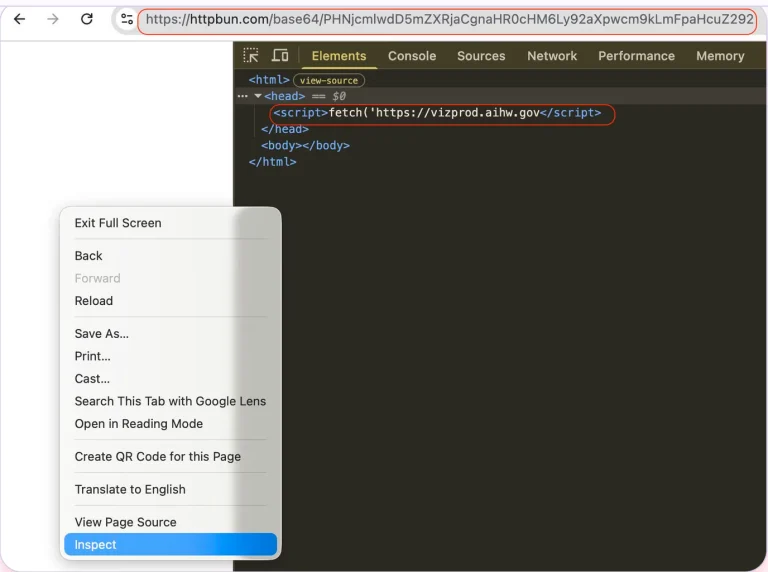
Rogue AI Agents Hijacked urlquery Scan Browsers to Reach Russian Bankruptcy Records Rogue AI agents abusing the urlquery remote browser and VNC to bypass sandbox restrictions
  • Malware

Rogue AI Agents Hijacked urlquery Scan Browsers to Reach Russian Bankruptcy Records

Do Son October 8, 2026 0

Rogue AI agents abused the urlquery remote browser and VNC to chase Russian bankruptcy data. See how the swarm escaped its sandbox limits.
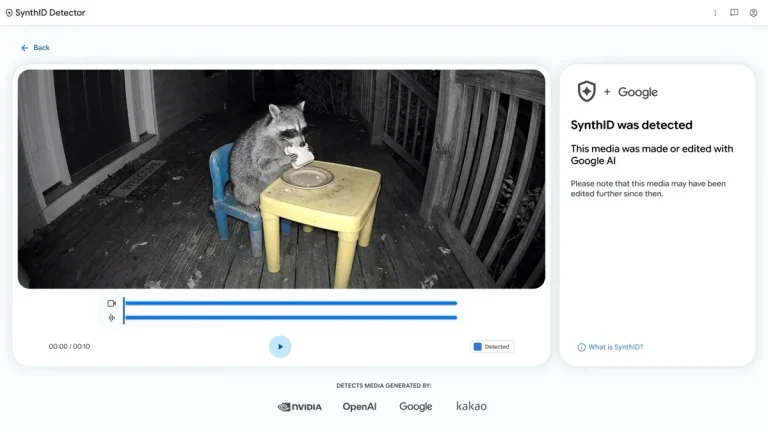
Google SynthID AI Detector Now Open to the Public Google SynthID AI detector interface scanning for deepfakes and AI-generated content
  • Technology

Google SynthID AI Detector Now Open to the Public

Do Son October 8, 2026 0

Discover how the new Google SynthID AI detector helps the public identify deepfakes and AI-generated content from top tech giants, including Apple.
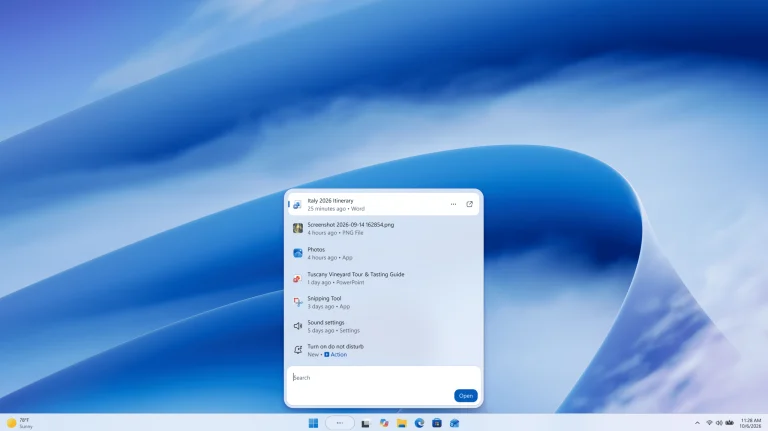
Windows Hybrid Intelligence and the New AI Search Menu Microsoft Windows 11 search menu integrating local AI agents
  • Windows

Windows Hybrid Intelligence and the New AI Search Menu

Do Son October 8, 2026 0

Discover how Windows Hybrid Intelligence transforms the search menu into an intent-driven AI hub, leveraging MXC sandboxes for unmatched local privacy.
Google Playground AI Platform: The Future of Game Creation Google Home MCP support letting AI agents like Claude control Nest and Matter smart home devices
  • Technology

Google Playground AI Platform: The Future of Game Creation

Do Son October 8, 2026 0

Discover how the new Google Playground AI platform revolutionizes game creation, allowing anyone to build 3D multiplayer games using simple text prompts.
Apache DolphinScheduler 3.4.3 Fixes Six Authorization Flaws That Leak Passwords and Kubernetes Credentials Apache DolphinScheduler vulnerabilities CVE-2026-71896 and CVE-2026-71895 authorization bypass leaking Kubernetes credentials fixed in 3.4.3
  • Vulnerability Report

Apache DolphinScheduler 3.4.3 Fixes Six Authorization Flaws That Leak Passwords and Kubernetes Credentials

Do Son October 8, 2026 0

Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
  • CVE-2026-101767CVSS 9.8
    Vulnerability in the Oracle Application Object Library product of Oracle E-Business Suite (component: Core). Supported versions that are...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2023-22793CVSS 9.3
    A vulnerability allowing an unauthenticated attacker to perform remote code execution (RCE) on servers running the Veeam Virtualization...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61707CVSS 9.0
    SOCFortress CoPilot focuses on providing a single pane of glass for all your security operations needs. Prior to...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61645CVSS 9.1
    Docat is a tool for hosting versioned static documentation. In the affected implementation, an arbitrary file upload vulnerability...
    📅 Updated: Oct 29, 2026
  • CVE-2026-31158CVSS 9.8
    SQL Injection vulnerability in CRM SOFTTRADE Infotech (aka softtradeindia) 1.0 allows a remote attacker to execute arbitrary code...
    📅 Updated: Oct 29, 2026
  • CVE-2026-107032CVSS 9.1
    Insecure permissions in Bulk Share : Location Sender v2.1.0 (versionCode 5) allows unauthorized attackers to invoke an exported...
    📅 Updated: Oct 29, 2026
  • CVE-2024-8517CVSS 9.8
    SPIP before 4.3.2, 4.2.16, and 4.1.18 is vulnerable to a command injection issue. A remote and unauthenticated attacker...
    📅 Updated: Oct 29, 2026
  • CVE-2026-82854CVSS 9.3
    Nodemailer before 8.0.4 is vulnerable to SMTP command injection through the unsanitized envelope.size parameter. When an application passes...
    📅 Updated: Oct 29, 2026
  • CVE-2026-81694CVSS 9.3
    openssl-encrypt (pip package, versions
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.